Sophos Integration for Elastic
Elastic Cloud Serverless projects are autoscaled environments, fully managed by Elastic and available on Elastic Cloud. Availability This functionality is generally available and ready for production usage. Elastic Cloud Serverless projects are autoscaled environments, fully managed by Elastic and available on Elastic Cloud. Availability This functionality is generally available and ready for production usage. The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes.
Serverless Observability
Generally available
Serverless Security
Generally available
Stack
9.0+
Generally available since 9.0
| Version | 3.17.2 (View all) |
| Subscription level What's this? |
Basic |
| Developed by What's this? |
Elastic |
| Ingestion method(s) | File, Network Protocol |
| Minimum Kibana version(s) | 9.0.0 8.11.0 |
The Sophos integration for Elastic allows you to ingest, parse, and visualize logs from Sophos Unified Threat Management (UTM) and Sophos XG Firewall (SFOS) devices. This integration provides comprehensive security monitoring, threat detection, and network traffic analysis capabilities within the Elastic Stack.
By collecting these logs, you can gain visibility into firewall activity, monitor security heartbeats, audit policy compliance, and troubleshoot network issues efficiently.
This integration is compatible with the following third-party vendor products:
- Sophos XG Firewall (SFOS): Explicitly tested on versions 17.5.x and 18.0.x. Versions above 18.0.x are expected to be compatible.
- Sophos Unified Threat Management (UTM): Supports modern Sophos UTM/Astaro Security Gateway versions.
This integration collects logs from Sophos firewalls by receiving syslog data over TCP or UDP, or by reading directly from log files. An Elastic Agent is deployed on a host that is configured as a syslog receiver or has access to the log files. The agent forwards the logs to your Elastic deployment, where they are parsed into the Elastic Common Schema (ECS) for unified analysis.
You can collect comprehensive firewall telemetry, including:
- Security heartbeats
- System events
- Traffic logs
- Specific log categories such as DNS, DHCP, HTTP, and packet filter logs
All logs are expected in the default Sophos syslog format.
The Sophos integration collects the following types of log data:
- Sophos XG logs (
xg): Comprehensive firewall telemetry including security heartbeats, system events, and traffic logs. These logs can be ingested via TCP, UDP, or by reading directly from a logfile. - Sophos UTM logs (
utm): Telemetry from Unified Threat Management (formerly Astaro) devices, covering specific log categories such as DNS, DHCP, HTTP, and Packet Filter logs. - Security events: Captures Antivirus detections, Intrusion Prevention System (IPS) alerts, and Advanced Threat Protection (ATP) events.
- System activity: Tracks administrative logons, configuration changes, and system health notifications from the Sophos appliances.
All logs are expected in the default Sophos syslog format, which is then parsed into the Elastic Common Schema (ECS) for unified analysis.
The Sophos integration for Elastic Agent allows organizations to ingest, parse, and visualize logs from Sophos Unified Threat Management (UTM) and Sophos XG Firewall (SFOS) devices. This integration supports the following use cases:
- Threat detection and security monitoring: Monitor firewall logs, packet filter events, and intrusion prevention alerts to identify and respond to potential security threats in real-time.
- Network visibility and traffic analysis: Analyze DNS, DHCP, and HTTP traffic logs to understand network usage patterns and identify shadow IT or unauthorized resource access.
- Compliance and auditing: Maintain long-term storage of firewall activity and administrative changes to satisfy regulatory requirements and support forensic investigations.
- Troubleshooting and performance optimization: Use detailed log data to diagnose connectivity issues, identify misconfigured firewall rules, and monitor system health across the security estate.
Before you can use this integration, you need to ensure the following prerequisites are met.
You need the following from the Sophos environment:
- Administrative credentials for the Sophos WebAdmin or XG Firewall web console to configure log export settings.
- Network connectivity between the firewall and the Elastic Agent host on the configured ports (default ports are UDP
9005/9549or TCP9005/9549). - For Sophos XG, the syslog format set to
Device Standard FormatorDefaultfor correct parsing. - Appropriate logging and reporting features enabled within your Sophos licensing tier.
You need the following for the Elastic deployment:
- Elastic Stack version 8.0 or higher.
- An Elastic Agent installed and enrolled in Fleet on a host reachable by the Sophos devices.
- The Sophos integration added to the Elastic Agent policy in Kibana.
- The host running the Elastic Agent configured to listen on the selected ports (for example,
9005or9549).
Elastic Agent must be installed. For more details, check the Elastic Agent installation instructions. You can install only one Elastic Agent per host.
Elastic Agent is required to stream data from the syslog or log file receiver and ship the data to Elastic, where the events will then be processed via the integration's ingest pipelines.
Configure your Sophos device to send logs to the Elastic Agent using the following instructions.
To configure Sophos XG Firewall to send logs via syslog:
- Log in to the Sophos XG Firewall web admin console.
- Navigate to System services > Log settings.
- Click Add under the Syslog server section.
- Configure the syslog server with these settings:
- Name: Enter a descriptive name like
Elastic-Agent-XG. - IP address/domain: Enter the IP address of the Elastic Agent.
- Port: Enter the port (e.g.,
9005). - Facility: Select
DAEMON. - Severity level: Select
Information. - Format: Select Device Standard Format.
- Name: Enter a descriptive name like
- Click Save.
- Scroll down to the Log settings section on the main page.
- Check the boxes for all log modules you wish to forward (Firewall, IPS, Antivirus, etc.) in the column for your new syslog server.
- Click Apply.
To configure Sophos UTM to send logs via syslog:
- Log in to the Sophos UTM WebAdmin interface.
- Navigate to Logging & Reporting > Log Settings.
- Click on the Remote Syslog Server tab.
- Toggle the Syslog Server Status to enabled.
- In the Syslog Servers section, click the Plus (+) icon.
- Configure the server:
- Name:
Elastic-Agent-UTM. - Server: Select or create the network definition for the Elastic Agent IP.
- Port: Enter the port (e.g.,
9549).
- Name:
- Click Save.
- Under Remote Syslog Log Selection, check the log types to forward (e.g., Firewall, Packet Filter).
- Click Apply.
- Sophos Firewall: Add a syslog server
- Sophos Firewall: Log settings
- Sophos Community: XGS Firewall Syslog Communication
- In Kibana, navigate to Management > Integrations and search for Sophos.
- Click Add Sophos.
- Select the input type that matches your configuration (UDP, TCP, or File).
Select Collecting syslog from Sophos via UDP and configure the settings for your specific device type.
For Sophos XG logs:
- Syslog Host (
syslog_host): The interface to listen on. Default:localhost. Use0.0.0.0to bind to all interfaces. - Syslog Port (
syslog_port): The port to listen on. Default:9005. - Default Host Name (
default_host_name): Fallback observer name. Default:firewall.localgroup.local. - Known Devices (
known_devices): Maps serial numbers to hostnames. - Preserve original event (
preserve_original_event): Default:False. - Tags (
tags): Default:['sophos-xg', 'forwarded']. - Timezone (
tz_offset): IANA time zone for syslog timestamps. Default:UTC. - Timezone Map (
tz_map): Advanced mapping for Sophos XG log timezones. - Custom UDP Options (
udp_options): Configureread_bufferormax_message_size. - Processors (
processors): Add custom pre-parsing logic.
For Sophos UTM logs:
- UDP host to listen on (
udp_host): The interface to listen on. Default:localhost. - UDP port to listen on (
udp_port): The port to listen on. Default:9549. - Timezone offset (
tz_offset): The timezone offset (e.g.,Europe/Amsterdamor+05:00). Default:UTC. - Preserve original event (
preserve_original_event): Default:False. - Tags (
tags): Default:['sophos-utm', 'forwarded']. - Processors (
processors): Add custom pre-parsing logic.
Select Collecting syslog from Sophos via TCP and configure the settings for your specific device type.
For Sophos XG logs:
- Syslog Host (
syslog_host): The interface to listen on. Default:localhost. - Syslog Port (
syslog_port): The port to listen on. Default:9005. - Default Host Name (
default_host_name): Fallback observer name. Default:firewall.localgroup.local. - Known Devices (
known_devices): Serial number to hostname mapping. - Preserve original event (
preserve_original_event): Default:False. - Tags (
tags): Default:['sophos-xg', 'forwarded']. - Timezone (
tz_offset): Default:UTC. - Timezone Map (
tz_map): Mapping for Sophos log timezones. - SSL Configuration (
ssl): Configurecertificateandkeyfor encrypted TCP. - Custom TCP Options (
tcp_options): Configuremax_connectionsandframing. - Processors (
processors): Add custom pre-parsing logic.
For Sophos UTM logs:
- TCP host to listen on (
tcp_host): The interface to listen on. Default:localhost. - TCP port to listen on (
tcp_port): The port to listen on. Default:9549. - Timezone offset (
tz_offset): The timezone offset (e.g.,Europe/Amsterdamor+05:00). Default:UTC. - Preserve original event (
preserve_original_event): Default:False. - Tags (
tags): Default:['sophos-utm', 'forwarded']. - Processors (
processors): Add custom pre-parsing logic.
Select Collecting syslog from Sophos via file and configure the settings for your specific device type.
For Sophos XG logs:
- Paths (
paths): List of paths to monitor. - Default Host Name (
default_host_name): Fallback observer name. Default:firewall.localgroup.local. - Known Devices (
known_devices): Serial number to hostname mapping. - Preserve original event (
preserve_original_event): Default:False. - Tags (
tags): Default:['sophos-xg', 'forwarded']. - Timezone (
tz_offset): Default:UTC. - Timezone Map (
tz_map): Mapping for Sophos log timezones. - Processors (
processors): Add custom pre-parsing logic.
For Sophos UTM logs:
- Paths (
paths): Paths to UTM logs (e.g.,['/var/log/sophos-utm.log']). - Timezone offset (
tz_offset): The timezone offset (e.g.,Europe/Amsterdamor+05:00). Default:UTC. - Preserve original event (
preserve_original_event): Default:False. - Tags (
tags): Default:['sophos-utm', 'forwarded']. - Processors (
processors): Add custom pre-parsing logic.
After configuration is complete, follow these steps to verify data is flowing correctly from Sophos to the Elastic Stack.
- Verify Elastic Agent status: Navigate to Management > Fleet > Agents in Kibana and ensure the Elastic Agent status is "Healthy" and "Active".
- Trigger data flow on Sophos:
- Generate Traffic Event: From a client machine behind the Sophos firewall, browse to several public websites to generate HTTP and Firewall log entries.
- Generate Admin Event: Log out of the Sophos WebAdmin/Web Console and log back in to trigger authentication and system audit events.
- Generate Config Event: Make a minor, non-disruptive change to a description field in a firewall rule and click Save or Apply to trigger a configuration log.
- Check data in Kibana:
- Navigate to Analytics > Discover.
- Select the
logs-*data view. - Enter the following KQL filter:
data_stream.dataset : "sophos.xg" OR data_stream.dataset : "sophos.utm". - Verify logs appear in the results. Expand a log entry and confirm these fields are populated:
event.dataset(should matchsophos.xgorsophos.utm)source.ipand/ordestination.ipevent.actionorevent.outcomemessage(containing the raw Sophos syslog payload)
- Navigate to Analytics > Dashboards and search for "Sophos" to view pre-built visualizations for traffic and security events.
For help with Elastic ingest tools, check Common problems.
The following are common configuration issues and their solutions:
- Format mismatch:
- Ensure the Sophos XG is set to Device Standard Format. Other formats like CEF or JSON are not currently supported by this integration's parsers.
- Timezone displacement:
- If logs appear in the future or past, check the Timezone or Timezone Map settings in the integration. Sophos XG often uses non-standard abbreviations that require explicit mapping.
- Port binding conflicts:
- If the Elastic Agent fails to start the input, verify that no other service is using the configured UDP/TCP ports (e.g.,
9005or9549).
- If the Elastic Agent fails to start the input, verify that no other service is using the configured UDP/TCP ports (e.g.,
- Serial number mapping issues:
- If hostnames appear as
firewall.localgroup.local, ensure you have correctly mapped the firewall's serial number to a hostname in the Known Devices configuration section.
- If hostnames appear as
- Parsing failures:
- Check for the
error.messagefield in Kibana. This often occurs if the Sophos device sends logs in a non-default format or if a new SFOS version introduces unexpected log fields. - Enable Preserve original event in the integration settings to see the raw log in
event.originalfor debugging.
- Check for the
- Incomplete UTM data:
- If specific UTM logs (like DNS) are missing, verify that those specific categories are checked in the Remote Syslog Log Selection menu on the UTM device.
To ensure optimal performance in high-volume environments, consider the following strategies:
This integration supports both UDP and TCP for syslog collection:
- UDP: Offers higher performance with lower overhead. It is often sufficient if the Elastic Agent and Sophos device are on the same local network.
- TCP: Recommended for high-volume environments or where data delivery guarantees are required to prevent log loss during network congestion.
To optimize performance, you can filter data at the source:
- Use the Log Settings on the Sophos device to select only high-value log categories (e.g., Firewall, IPS) for export.
- Filter out high-noise events like "Allowed" packet filter logs to significantly reduce the volume of data processed by the Elastic Agent and stored in Elasticsearch.
For high-throughput environments processing logs from multiple large Sophos clusters:
- Deploy multiple Elastic Agents behind a network load balancer to distribute the syslog ingestion load and provide high availability.
- Place Agents close to the data source to minimize latency and potential packet loss.
For more information on architectures that can be used for scaling this integration, check the Ingest Architectures documentation.
These inputs can be used with this integration:
logfile
For more details about the logfile input settings, check the Filebeat documentation.
To collect logs via logfile, select Collect logs via the logfile input and configure the following parameter:
- Paths: List of glob-based paths to crawl and fetch log files from. Supports glob patterns like
/var/log/*.logor/var/log/*/*.logfor subfolder matching. Each file found starts a separate harvester.
tcp
For more details about the TCP input settings, check the Filebeat documentation.
To collect logs via TCP, select Collect logs via TCP and configure the following parameters:
Required Settings:
- Host
- Port
Common Optional Settings:
- Max Message Size - Maximum size of incoming messages
- Max Connections - Maximum number of concurrent connections
- Timeout - How long to wait for data before closing idle connections
- Line Delimiter - Character(s) that separate log messages
To enable encrypted connections, configure the following SSL settings:
SSL Settings:
- Enable SSL - Toggle to enable SSL/TLS encryption
- Certificate - Path to the SSL certificate file (
.crtor.pem) - Certificate Key - Path to the private key file (
.key) - Certificate Authorities - Path to CA certificate file for client certificate validation (optional)
- Client Authentication - Require client certificates (
none,optional, orrequired) - Supported Protocols - TLS versions to support (e.g.,
TLSv1.2,TLSv1.3)
Example SSL Configuration:
ssl.enabled: true
ssl.certificate: "/path/to/server.crt"
ssl.key: "/path/to/server.key"
ssl.certificate_authorities: ["/path/to/ca.crt"]
ssl.client_authentication: "optional"
udp
For more details about the UDP input settings, check the Filebeat documentation.
To collect logs via UDP, select Collect logs via UDP and configure the following parameters:
Required Settings:
- Host
- Port
Common Optional Settings:
- Max Message Size - Maximum size of UDP packets to accept (default: 10KB, max: 64KB)
- Read Buffer - UDP socket read buffer size for handling bursts of messages
- Read Timeout - How long to wait for incoming packets before checking for shutdown
This integration uses the following vendor documentation:
The utm data stream collects Sophos UTM logs.
Exported fields
| Field | Description | Type |
|---|---|---|
| @timestamp | Date/time when the event originated. This is the date/time extracted from the event, typically representing when the event was generated by the source. If the event source has no original timestamp, this value is typically populated by the first time the event was received by the pipeline. Required field for all events. | date |
| client.as.number | Unique number allocated to the autonomous system. The autonomous system number (ASN) uniquely identifies each network on the Internet. | long |
| client.as.organization.name | Organization name. | keyword |
| client.as.organization.name.text | Multi-field of client.as.organization.name. |
match_only_text |
| client.geo.city_name | City name. | keyword |
| client.geo.continent_name | Name of the continent. | keyword |
| client.geo.country_iso_code | Country ISO code. | keyword |
| client.geo.country_name | Country name. | keyword |
| client.geo.location | Longitude and latitude. | geo_point |
| client.geo.name | User-defined description of a location, at the level of granularity they care about. Could be the name of their data centers, the floor number, if this describes a local physical entity, city names. Not typically used in automated geolocation. | keyword |
| client.geo.postal_code | Postal code associated with the location. Values appropriate for this field may also be known as a postcode or ZIP code and will vary widely from country to country. | keyword |
| client.geo.region_iso_code | Region ISO code. | keyword |
| client.geo.region_name | Region name. | keyword |
| client.geo.timezone | The time zone of the location, such as IANA time zone name. | keyword |
| client.ip | IP address of the client (IPv4 or IPv6). | ip |
| client.mac | MAC address of the client. The notation format from RFC 7042 is suggested: Each octet (that is, 8-bit byte) is represented by two [uppercase] hexadecimal digits giving the value of the octet as an unsigned integer. Successive octets are separated by a hyphen. | keyword |
| client.port | Port of the client. | long |
| cloud.account.id | The cloud account or organization id used to identify different entities in a multi-tenant environment. Examples: AWS account id, Google Cloud ORG Id, or other unique identifier. | keyword |
| cloud.availability_zone | Availability zone in which this host is running. | keyword |
| cloud.image.id | Image ID for the cloud instance. | keyword |
| cloud.instance.id | Instance ID of the host machine. | keyword |
| cloud.instance.name | Instance name of the host machine. | keyword |
| cloud.machine.type | Machine type of the host machine. | keyword |
| cloud.project.id | Name of the project in Google Cloud. | keyword |
| cloud.provider | Name of the cloud provider. Example values are aws, azure, gcp, or digitalocean. | keyword |
| cloud.region | Region in which this host is running. | keyword |
| container.id | Unique container id. | keyword |
| container.image.name | Name of the image the container was built on. | keyword |
| container.labels | Image labels. | object |
| container.name | Container name. | keyword |
| data_stream.dataset | Data stream dataset. | constant_keyword |
| data_stream.namespace | Data stream namespace. | constant_keyword |
| data_stream.type | Data stream type. | constant_keyword |
| destination.as.number | Unique number allocated to the autonomous system. The autonomous system number (ASN) uniquely identifies each network on the Internet. | long |
| destination.as.organization.name | Organization name. | keyword |
| destination.as.organization.name.text | Multi-field of destination.as.organization.name. |
match_only_text |
| destination.geo.city_name | City name. | keyword |
| destination.geo.continent_name | Name of the continent. | keyword |
| destination.geo.country_iso_code | Country ISO code. | keyword |
| destination.geo.country_name | Country name. | keyword |
| destination.geo.location | Longitude and latitude. | geo_point |
| destination.geo.name | User-defined description of a location, at the level of granularity they care about. Could be the name of their data centers, the floor number, if this describes a local physical entity, city names. Not typically used in automated geolocation. | keyword |
| destination.geo.postal_code | Postal code associated with the location. Values appropriate for this field may also be known as a postcode or ZIP code and will vary widely from country to country. | keyword |
| destination.geo.region_iso_code | Region ISO code. | keyword |
| destination.geo.region_name | Region name. | keyword |
| destination.geo.timezone | The time zone of the location, such as IANA time zone name. | keyword |
| destination.ip | IP address of the destination (IPv4 or IPv6). | ip |
| destination.mac | MAC address of the destination. The notation format from RFC 7042 is suggested: Each octet (that is, 8-bit byte) is represented by two [uppercase] hexadecimal digits giving the value of the octet as an unsigned integer. Successive octets are separated by a hyphen. | keyword |
| destination.port | Port of the destination. | long |
| device.id | The unique identifier of a device. The identifier must not change across application sessions but stay fixed for an instance of a (mobile) device. On iOS, this value must be equal to the vendor identifier (https://developer.apple.com/documentation/uikit/uidevice/1620059-identifierforvendor). On Android, this value must be equal to the Firebase Installation ID or a globally unique UUID which is persisted across sessions in your application. For GDPR and data protection law reasons this identifier should not carry information that would allow to identify a user. | keyword |
| ecs.version | ECS version this event conforms to. ecs.version is a required field and must exist in all events. When querying across multiple indices -- which may conform to slightly different ECS versions -- this field lets integrations adjust to the schema version of the events. |
keyword |
| error.message | Error message. | match_only_text |
| event.action | The action captured by the event. This describes the information in the event. It is more specific than event.category. Examples are group-add, process-started, file-created. The value is normally defined by the implementer. |
keyword |
| event.category | This is one of four ECS Categorization Fields, and indicates the second level in the ECS category hierarchy. event.category represents the "big buckets" of ECS categories. For example, filtering on event.category:process yields all events relating to process activity. This field is closely related to event.type, which is used as a subcategory. This field is an array. This will allow proper categorization of some events that fall in multiple categories. |
keyword |
| event.dataset | Event dataset | constant_keyword |
| event.id | Unique ID to describe the event. | keyword |
| event.kind | This is one of four ECS Categorization Fields, and indicates the highest level in the ECS category hierarchy. event.kind gives high-level information about what type of information the event contains, without being specific to the contents of the event. For example, values of this field distinguish alert events from metric events. The value of this field can be used to inform how these kinds of events should be handled. They may warrant different retention, different access control, it may also help understand whether the data is coming in at a regular interval or not. |
keyword |
| event.module | Event module | constant_keyword |
| event.original | Raw text message of entire event. Used to demonstrate log integrity or where the full log message (before splitting it up in multiple parts) may be required, e.g. for reindex. This field is not indexed and doc_values are disabled. It cannot be searched, but it can be retrieved from _source. If users wish to override this and index this field, please see Field data types in the Elasticsearch Reference. |
keyword |
| event.provider | Source of the event. Event transports such as Syslog or the Windows Event Log typically mention the source of an event. It can be the name of the software that generated the event (e.g. Sysmon, httpd), or of a subsystem of the operating system (kernel, Microsoft-Windows-Security-Auditing). | keyword |
| event.severity | The numeric severity of the event according to your event source. What the different severity values mean can be different between sources and use cases. It's up to the implementer to make sure severities are consistent across events from the same source. The Syslog severity belongs in log.syslog.severity.code. event.severity is meant to represent the severity according to the event source (e.g. firewall, IDS). If the event source does not publish its own severity, you may optionally copy the log.syslog.severity.code to event.severity. |
long |
| event.timezone | This field should be populated when the event's timestamp does not include timezone information already (e.g. default Syslog timestamps). It's optional otherwise. Acceptable timezone formats are: a canonical ID (e.g. "Europe/Amsterdam"), abbreviated (e.g. "EST") or an HH:mm differential (e.g. "-05:00"). | keyword |
| event.type | This is one of four ECS Categorization Fields, and indicates the third level in the ECS category hierarchy. event.type represents a categorization "sub-bucket" that, when used along with the event.category field values, enables filtering events down to a level appropriate for single visualization. This field is an array. This will allow proper categorization of some events that fall in multiple event types. |
keyword |
| file.name | Name of the file including the extension, without the directory. | keyword |
| group.name | Name of the group. | keyword |
| host.architecture | Operating system architecture. | keyword |
| host.containerized | If the host is a container. | boolean |
| host.domain | Name of the domain of which the host is a member. For example, on Windows this could be the host's Active Directory domain or NetBIOS domain name. For Linux this could be the domain of the host's LDAP provider. | keyword |
| host.hostname | Hostname of the host. It normally contains what the hostname command returns on the host machine. |
keyword |
| host.id | Unique host id. As hostname is not always unique, use values that are meaningful in your environment. Example: The current usage of beat.name. |
keyword |
| host.ip | Host ip addresses. | ip |
| host.mac | Host mac addresses. | keyword |
| host.name | Name of the host. It can contain what hostname returns on Unix systems, the fully qualified domain name, or a name specified by the user. The sender decides which value to use. |
keyword |
| host.os.build | OS build information. | keyword |
| host.os.codename | OS codename, if any. | keyword |
| host.os.family | OS family (such as redhat, debian, freebsd, windows). | keyword |
| host.os.kernel | Operating system kernel version as a raw string. | keyword |
| host.os.name | Operating system name, without the version. | keyword |
| host.os.name.text | Multi-field of host.os.name. |
text |
| host.os.platform | Operating system platform (such centos, ubuntu, windows). | keyword |
| host.os.version | Operating system version as a raw string. | keyword |
| host.type | Type of host. For Cloud providers this can be the machine type like t2.medium. If vm, this could be the container, for example, or other information meaningful in your environment. |
keyword |
| http.request.bytes | Total size in bytes of the request (body and headers). | long |
| http.request.id | A unique identifier for each HTTP request to correlate logs between clients and servers in transactions. The id may be contained in a non-standard HTTP header, such as X-Request-ID or X-Correlation-ID. |
keyword |
| http.request.method | HTTP request method. The value should retain its casing from the original event. For example, GET, get, and GeT are all considered valid values for this field. |
keyword |
| http.request.referrer | Referrer for this HTTP request. | keyword |
| http.response.status_code | HTTP response status code. | long |
| input.type | Input type. | keyword |
| log.file.path | Full path to the log file this event came from. | keyword |
| log.flags | Flags for the log file. | keyword |
| log.offset | Log offset | long |
| log.source.address | Source address from which the log event was read / sent from. | keyword |
| log.syslog.facility.code | The Syslog numeric facility of the log event, if available. According to RFCs 5424 and 3164, this value should be an integer between 0 and 23. | long |
| log.syslog.facility.name | The Syslog text-based facility of the log event, if available. | keyword |
| log.syslog.priority | Syslog numeric priority of the event, if available. According to RFCs 5424 and 3164, the priority is 8 * facility + severity. This number is therefore expected to contain a value between 0 and 191. | long |
| log.syslog.severity.code | The Syslog numeric severity of the log event, if available. If the event source publishing via Syslog provides a different numeric severity value (e.g. firewall, IDS), your source's numeric severity should go to event.severity. If the event source does not specify a distinct severity, you can optionally copy the Syslog severity to event.severity. |
long |
| log.syslog.severity.name | The Syslog numeric severity of the log event, if available. If the event source publishing via Syslog provides a different severity value (e.g. firewall, IDS), your source's text severity should go to log.level. If the event source does not specify a distinct severity, you can optionally copy the Syslog severity to log.level. |
keyword |
| message | For log events the message field contains the log message, optimized for viewing in a log viewer. For structured logs without an original message field, other fields can be concatenated to form a human-readable summary of the event. If multiple messages exist, they can be combined into one message. | match_only_text |
| network.application | When a specific application or service is identified from network connection details (source/dest IPs, ports, certificates, or wire format), this field captures the application's or service's name. For example, the original event identifies the network connection being from a specific web service in a https network connection, like facebook or twitter. The field value must be normalized to lowercase for querying. |
keyword |
| network.iana_number | IANA Protocol Number (https://www.iana.org/assignments/protocol-numbers/protocol-numbers.xhtml). Standardized list of protocols. This aligns well with NetFlow and sFlow related logs which use the IANA Protocol Number. | keyword |
| network.protocol | In the OSI Model this would be the Application Layer protocol. For example, http, dns, or ssh. The field value must be normalized to lowercase for querying. |
keyword |
| network.transport | Same as network.iana_number, but instead using the Keyword name of the transport layer (udp, tcp, ipv6-icmp, etc.) The field value must be normalized to lowercase for querying. | keyword |
| network.type | In the OSI Model this would be the Network Layer. ipv4, ipv6, ipsec, pim, etc The field value must be normalized to lowercase for querying. | keyword |
| observer.egress.interface.name | Interface name as reported by the system. | keyword |
| observer.ingress.interface.name | Interface name as reported by the system. | keyword |
| observer.product | The product name of the observer. | keyword |
| observer.type | The type of the observer the data is coming from. There is no predefined list of observer types. Some examples are forwarder, firewall, ids, ips, proxy, poller, sensor, APM server. |
keyword |
| observer.vendor | Vendor name of the observer. | keyword |
| process.name | Process name. Sometimes called program name or similar. | keyword |
| process.name.text | Multi-field of process.name. |
match_only_text |
| process.pid | Process id. | long |
| related.hosts | All hostnames or other host identifiers seen on your event. Example identifiers include FQDNs, domain names, workstation names, or aliases. | keyword |
| related.ip | All of the IPs seen on your event. | ip |
| related.user | All the user names or other user identifiers seen on the event. | keyword |
| rule.id | A rule ID that is unique within the scope of an agent, observer, or other entity using the rule for detection of this event. | keyword |
| server.as.number | Unique number allocated to the autonomous system. The autonomous system number (ASN) uniquely identifies each network on the Internet. | long |
| server.as.organization.name | Organization name. | keyword |
| server.as.organization.name.text | Multi-field of server.as.organization.name. |
match_only_text |
| server.geo.city_name | City name. | keyword |
| server.geo.continent_name | Name of the continent. | keyword |
| server.geo.country_iso_code | Country ISO code. | keyword |
| server.geo.country_name | Country name. | keyword |
| server.geo.location | Longitude and latitude. | geo_point |
| server.geo.name | User-defined description of a location, at the level of granularity they care about. Could be the name of their data centers, the floor number, if this describes a local physical entity, city names. Not typically used in automated geolocation. | keyword |
| server.geo.postal_code | Postal code associated with the location. Values appropriate for this field may also be known as a postcode or ZIP code and will vary widely from country to country. | keyword |
| server.geo.region_iso_code | Region ISO code. | keyword |
| server.geo.region_name | Region name. | keyword |
| server.geo.timezone | The time zone of the location, such as IANA time zone name. | keyword |
| server.ip | IP address of the server (IPv4 or IPv6). | ip |
| server.port | Port of the server. | long |
| sophos.utm.action | Event action. | keyword |
| sophos.utm.ad_domain | keyword | |
| sophos.utm.app_id | Application ID. | keyword |
| sophos.utm.aptptime | long | |
| sophos.utm.auth | Auth ID. | keyword |
| sophos.utm.authtime | Authorization time. | long |
| sophos.utm.avscantime | AntiVirus scan time. | long |
| sophos.utm.cached | Cached bytes. | keyword |
| sophos.utm.category | Array of category IDs. | keyword |
| sophos.utm.categoryname | Array of category names. | keyword |
| sophos.utm.cattime | long | |
| sophos.utm.client.hostname | Client hostname in DHCP events. | keyword |
| sophos.utm.code | Code ID. | keyword |
| sophos.utm.content_type | HTTP header content-type. | keyword |
| sophos.utm.country | HTTP request country source. | keyword |
| sophos.utm.dnstime | DNS time. | long |
| sophos.utm.exceptions | keyword | |
| sophos.utm.extension | URL extension. | keyword |
| sophos.utm.filteraction | Filter action. | keyword |
| sophos.utm.fullreqtime | Full HTTP request time. | long |
| sophos.utm.function | The failed function in case of error. | keyword |
| sophos.utm.id | Packet Filter rule ID. | keyword |
| sophos.utm.length | Packet length in bytes. | long |
| sophos.utm.line | The failed line in case of error. | keyword |
| sophos.utm.mark | The Netfilter conntrack mark. | keyword |
| sophos.utm.name | Event description. | keyword |
| sophos.utm.overridecategory | keyword | |
| sophos.utm.overridereputation | keyword | |
| sophos.utm.prec | keyword | |
| sophos.utm.profile | HTTP profile. | keyword |
| sophos.utm.reason | keyword | |
| sophos.utm.reputation | keyword | |
| sophos.utm.router.ip | DHCP router IP. | ip |
| sophos.utm.sandbox | keyword | |
| sophos.utm.severity | Event severity. | keyword |
| sophos.utm.socket | Socket where DHCP server is listening. | keyword |
| sophos.utm.sub | keyword | |
| sophos.utm.subnet | Subnet where DHCP server is listening. | keyword |
| sophos.utm.sys | System name. | keyword |
| sophos.utm.tcpflags | TCP flags set in any packet of session. | keyword |
| sophos.utm.tos | Type of Service. | keyword |
| sophos.utm.ttl | Time to Live. | long |
| sophos.utm.type | Type ID. | keyword |
| sophos.utm.url | HTTP request URL. | keyword |
| source.as.number | Unique number allocated to the autonomous system. The autonomous system number (ASN) uniquely identifies each network on the Internet. | long |
| source.as.organization.name | Organization name. | keyword |
| source.as.organization.name.text | Multi-field of source.as.organization.name. |
match_only_text |
| source.geo.city_name | City name. | keyword |
| source.geo.continent_name | Name of the continent. | keyword |
| source.geo.country_iso_code | Country ISO code. | keyword |
| source.geo.country_name | Country name. | keyword |
| source.geo.location | Longitude and latitude. | geo_point |
| source.geo.name | User-defined description of a location, at the level of granularity they care about. Could be the name of their data centers, the floor number, if this describes a local physical entity, city names. Not typically used in automated geolocation. | keyword |
| source.geo.postal_code | Postal code associated with the location. Values appropriate for this field may also be known as a postcode or ZIP code and will vary widely from country to country. | keyword |
| source.geo.region_iso_code | Region ISO code. | keyword |
| source.geo.region_name | Region name. | keyword |
| source.geo.timezone | The time zone of the location, such as IANA time zone name. | keyword |
| source.ip | IP address of the source (IPv4 or IPv6). | ip |
| source.mac | MAC address of the source. The notation format from RFC 7042 is suggested: Each octet (that is, 8-bit byte) is represented by two [uppercase] hexadecimal digits giving the value of the octet as an unsigned integer. Successive octets are separated by a hyphen. | keyword |
| source.port | Port of the source. | long |
| tags | List of keywords used to tag each event. | keyword |
| url.domain | Domain of the url, such as "www.elastic.co". In some cases a URL may refer to an IP and/or port directly, without a domain name. In this case, the IP address would go to the domain field. If the URL contains a literal IPv6 address enclosed by [ and ] (IETF RFC 2732), the [ and ] characters should also be captured in the domain field. |
keyword |
| url.extension | The field contains the file extension from the original request url, excluding the leading dot. The file extension is only set if it exists, as not every url has a file extension. The leading period must not be included. For example, the value must be "png", not ".png". Note that when the file name has multiple extensions (example.tar.gz), only the last one should be captured ("gz", not "tar.gz"). | keyword |
| url.fragment | Portion of the url after the #, such as "top". The # is not part of the fragment. |
keyword |
| url.full | If full URLs are important to your use case, they should be stored in url.full, whether this field is reconstructed or present in the event source. |
wildcard |
| url.full.text | Multi-field of url.full. |
match_only_text |
| url.original | Unmodified original url as seen in the event source. Note that in network monitoring, the observed URL may be a full URL, whereas in access logs, the URL is often just represented as a path. This field is meant to represent the URL as it was observed, complete or not. | wildcard |
| url.original.text | Multi-field of url.original. |
match_only_text |
| url.password | Password of the request. | keyword |
| url.path | Path of the request, such as "/search". | wildcard |
| url.port | Port of the request, such as 443. | long |
| url.query | The query field describes the query string of the request, such as "q=elasticsearch". The ? is excluded from the query string. If a URL contains no ?, there is no query field. If there is a ? but no query, the query field exists with an empty string. The exists query can be used to differentiate between the two cases. |
keyword |
| url.registered_domain | The highest registered url domain, stripped of the subdomain. For example, the registered domain for "foo.example.com" is "example.com". This value can be determined precisely with a list like the public suffix list (https://publicsuffix.org). Trying to approximate this by simply taking the last two labels will not work well for TLDs such as "co.uk". | keyword |
| url.scheme | Scheme of the request, such as "https". Note: The : is not part of the scheme. |
keyword |
| url.subdomain | The subdomain portion of a fully qualified domain name includes all of the names except the host name under the registered_domain. In a partially qualified domain, or if the the qualification level of the full name cannot be determined, subdomain contains all of the names below the registered domain. For example the subdomain portion of "www.east.example.com" is "east". If the domain has multiple levels of subdomain, such as "sub2.sub1.example.com", the subdomain field should contain "sub2.sub1", with no trailing period. | keyword |
| url.top_level_domain | The effective top level domain (eTLD), also known as the domain suffix, is the last part of the domain name. For example, the top level domain for example.com is "com". This value can be determined precisely with a list like the public suffix list (https://publicsuffix.org). Trying to approximate this by simply taking the last label will not work well for effective TLDs such as "co.uk". | keyword |
| url.username | Username of the request. | keyword |
| user.name | Short name or login of the user. | keyword |
| user.name.text | Multi-field of user.name. |
match_only_text |
| user_agent.device.name | Name of the device. | keyword |
| user_agent.name | Name of the user agent. | keyword |
| user_agent.original | Unparsed user_agent string. | keyword |
| user_agent.original.text | Multi-field of user_agent.original. |
match_only_text |
| user_agent.os.full | Operating system name, including the version or code name. | keyword |
| user_agent.os.full.text | Multi-field of user_agent.os.full. |
match_only_text |
| user_agent.os.name | Operating system name, without the version. | keyword |
| user_agent.os.name.text | Multi-field of user_agent.os.name. |
match_only_text |
| user_agent.os.version | Operating system version as a raw string. | keyword |
| user_agent.version | Version of the user agent. | keyword |
Example
{
    "@timestamp": "2023-03-08T15:00:00.000Z",
    "agent": {
        "ephemeral_id": "1c14ef92-e910-4bef-84c4-4ceecac7a048",
        "id": "60d18e37-b683-4bd5-a0e9-e19bb64cc7bb",
        "name": "docker-fleet-agent",
        "type": "filebeat",
        "version": "8.10.3"
    },
    "data_stream": {
        "dataset": "sophos.utm",
        "namespace": "ep",
        "type": "logs"
    },
    "destination": {
        "as": {
            "number": 29518,
            "organization": {
                "name": "Bredband2 AB"
            }
        },
        "geo": {
            "city_name": "Linköping",
            "continent_name": "Europe",
            "country_iso_code": "SE",
            "country_name": "Sweden",
            "location": {
                "lat": 58.4167,
                "lon": 15.6167
            },
            "region_iso_code": "SE-E",
            "region_name": "Östergötland County"
        },
        "ip": "89.160.20.129"
    },
    "device": {
        "id": "0"
    },
    "ecs": {
        "version": "8.17.0"
    },
    "elastic_agent": {
        "id": "60d18e37-b683-4bd5-a0e9-e19bb64cc7bb",
        "snapshot": false,
        "version": "8.10.3"
    },
    "event": {
        "action": "pass",
        "agent_id_status": "verified",
        "category": [
            "web"
        ],
        "dataset": "sophos.utm",
        "id": "0001",
        "ingested": "2023-11-19T21:23:10Z",
        "kind": "event",
        "provider": "http",
        "severity": 6,
        "timezone": "+00:00",
        "type": [
            "info"
        ]
    },
    "group": {
        "name": "testgroup"
    },
    "host": {
        "hostname": "sophos-test-vm1",
        "name": "sophos-test-vm1"
    },
    "http": {
        "request": {
            "bytes": 311,
            "id": "0x7fad9e44ac00",
            "method": "HEAD",
            "referrer": "https://referer.example.com/"
        },
        "response": {
            "status_code": 200
        }
    },
    "input": {
        "type": "udp"
    },
    "log": {
        "source": {
            "address": "172.28.0.5:49278"
        }
    },
    "network": {
        "application": "googplay",
        "protocol": "http"
    },
    "observer": {
        "product": "UTM",
        "type": "firewall",
        "vendor": "Sophos"
    },
    "process": {
        "name": "httpproxy",
        "pid": 6267
    },
    "related": {
        "hosts": [
            "sophos-test-vm1"
        ],
        "ip": [
            "67.43.156.2",
            "89.160.20.129"
        ],
        "user": [
            "testuser"
        ]
    },
    "sophos": {
        "utm": {
            "ad_domain": "example.com",
            "app_id": "816",
            "aptptime": 0,
            "auth": "0",
            "authtime": 0,
            "avscantime": 0,
            "cached": "0",
            "category": [
                "178"
            ],
            "categoryname": [
                "Internet Services"
            ],
            "cattime": 200,
            "content_type": "application/octet-stream",
            "country": "United States",
            "dnstime": 5,
            "filteraction": "REF_HTTP_ACTION",
            "fullreqtime": 32181,
            "name": "http access",
            "profile": "HTTP_Sophos_Profile_1",
            "reputation": "trusted",
            "severity": "info",
            "sub": "http",
            "sys": "SecureWeb"
        }
    },
    "source": {
        "as": {
            "number": 35908
        },
        "geo": {
            "continent_name": "Asia",
            "country_iso_code": "BT",
            "country_name": "Bhutan",
            "location": {
                "lat": 27.5,
                "lon": 90.5
            }
        },
        "ip": "67.43.156.2"
    },
    "tags": [
        "sophos-utm",
        "forwarded"
    ],
    "url": {
        "domain": "myurl.example.com",
        "original": "https://myurl.example.com/extension",
        "path": "/extension",
        "scheme": "https"
    },
    "user": {
        "name": "testuser"
    },
    "user_agent": {
        "device": {
            "name": "Other"
        },
        "name": "Other",
        "original": "Microsoft BITS/7.8"
    }
}
The xg data stream collects Sophos XG (SFOS) logs.
Exported fields
| Field | Description | Type |
|---|---|---|
| @timestamp | Event timestamp. | date |
| cloud.account.id | The cloud account or organization id used to identify different entities in a multi-tenant environment. Examples: AWS account id, Google Cloud ORG Id, or other unique identifier. | keyword |
| cloud.availability_zone | Availability zone in which this host is running. | keyword |
| cloud.image.id | Image ID for the cloud instance. | keyword |
| cloud.instance.id | Instance ID of the host machine. | keyword |
| cloud.instance.name | Instance name of the host machine. | keyword |
| cloud.machine.type | Machine type of the host machine. | keyword |
| cloud.project.id | Name of the project in Google Cloud. | keyword |
| cloud.provider | Name of the cloud provider. Example values are aws, azure, gcp, or digitalocean. | keyword |
| cloud.region | Region in which this host is running. | keyword |
| container.id | Unique container id. | keyword |
| container.image.name | Name of the image the container was built on. | keyword |
| container.labels | Image labels. | object |
| container.name | Container name. | keyword |
| data_stream.dataset | Data stream dataset. | constant_keyword |
| data_stream.namespace | Data stream namespace. | constant_keyword |
| data_stream.type | Data stream type. | constant_keyword |
| destination.as.number | Unique number allocated to the autonomous system. The autonomous system number (ASN) uniquely identifies each network on the Internet. | long |
| destination.as.organization.name | Organization name. | keyword |
| destination.as.organization.name.text | Multi-field of destination.as.organization.name. |
match_only_text |
| destination.bytes | Bytes sent from the destination to the source. | long |
| destination.domain | The domain name of the destination system. This value may be a host name, a fully qualified domain name, or another host naming format. The value may derive from the original event or be added from enrichment. | keyword |
| destination.geo.city_name | City name. | keyword |
| destination.geo.continent_name | Name of the continent. | keyword |
| destination.geo.country_iso_code | Country ISO code. | keyword |
| destination.geo.country_name | Country name. | keyword |
| destination.geo.location | Longitude and latitude. | geo_point |
| destination.geo.name | User-defined description of a location, at the level of granularity they care about. Could be the name of their data centers, the floor number, if this describes a local physical entity, city names. Not typically used in automated geolocation. | keyword |
| destination.geo.region_iso_code | Region ISO code. | keyword |
| destination.geo.region_name | Region name. | keyword |
| destination.ip | IP address of the destination (IPv4 or IPv6). | ip |
| destination.mac | MAC address of the destination. The notation format from RFC 7042 is suggested: Each octet (that is, 8-bit byte) is represented by two [uppercase] hexadecimal digits giving the value of the octet as an unsigned integer. Successive octets are separated by a hyphen. | keyword |
| destination.nat.ip | Translated ip of destination based NAT sessions (e.g. internet to private DMZ) Typically used with load balancers, firewalls, or routers. | ip |
| destination.nat.port | Port the source session is translated to by NAT Device. Typically used with load balancers, firewalls, or routers. | long |
| destination.packets | Packets sent from the destination to the source. | long |
| destination.port | Port of the destination. | long |
| destination.user.email | User email address. | keyword |
| ecs.version | ECS version this event conforms to. ecs.version is a required field and must exist in all events. When querying across multiple indices -- which may conform to slightly different ECS versions -- this field lets integrations adjust to the schema version of the events. |
keyword |
| email.from.address | The email address of the sender, typically from the RFC 5322 From: header field. |
keyword |
| email.subject | A brief summary of the topic of the message. | keyword |
| email.subject.text | Multi-field of email.subject. |
match_only_text |
| email.to.address | The email address of recipient | keyword |
| event.action | The action captured by the event. This describes the information in the event. It is more specific than event.category. Examples are group-add, process-started, file-created. The value is normally defined by the implementer. |
keyword |
| event.category | This is one of four ECS Categorization Fields, and indicates the second level in the ECS category hierarchy. event.category represents the "big buckets" of ECS categories. For example, filtering on event.category:process yields all events relating to process activity. This field is closely related to event.type, which is used as a subcategory. This field is an array. This will allow proper categorization of some events that fall in multiple categories. |
keyword |
| event.code | Identification code for this event, if one exists. Some event sources use event codes to identify messages unambiguously, regardless of message language or wording adjustments over time. An example of this is the Windows Event ID. | keyword |
| event.created | event.created contains the date/time when the event was first read by an agent, or by your pipeline. This field is distinct from @timestamp in that @timestamp typically contain the time extracted from the original event. In most situations, these two timestamps will be slightly different. The difference can be used to calculate the delay between your source generating an event, and the time when your agent first processed it. This can be used to monitor your agent's or pipeline's ability to keep up with your event source. In case the two timestamps are identical, @timestamp should be used. |
date |
| event.dataset | Event dataset | constant_keyword |
| event.duration | Duration of the event in nanoseconds. If event.start and event.end are known this value should be the difference between the end and start time. |
long |
| event.end | event.end contains the date when the event ended or when the activity was last observed. |
date |
| event.hash | Hash (perhaps logstash fingerprint) of raw field to be able to demonstrate log integrity. | keyword |
| event.id | Unique ID to describe the event. | keyword |
| event.ingested | Timestamp when an event arrived in the central data store. This is different from @timestamp, which is when the event originally occurred. It's also different from event.created, which is meant to capture the first time an agent saw the event. In normal conditions, assuming no tampering, the timestamps should chronologically look like this: @timestamp < event.created < event.ingested. |
date |
| event.kind | This is one of four ECS Categorization Fields, and indicates the highest level in the ECS category hierarchy. event.kind gives high-level information about what type of information the event contains, without being specific to the contents of the event. For example, values of this field distinguish alert events from metric events. The value of this field can be used to inform how these kinds of events should be handled. They may warrant different retention, different access control, it may also help understand whether the data is coming in at a regular interval or not. |
keyword |
| event.module | Event module | constant_keyword |
| event.original | Raw text message of entire event. Used to demonstrate log integrity or where the full log message (before splitting it up in multiple parts) may be required, e.g. for reindex. This field is not indexed and doc_values are disabled. It cannot be searched, but it can be retrieved from _source. If users wish to override this and index this field, please see Field data types in the Elasticsearch Reference. |
keyword |
| event.outcome | This is one of four ECS Categorization Fields, and indicates the lowest level in the ECS category hierarchy. event.outcome simply denotes whether the event represents a success or a failure from the perspective of the entity that produced the event. Note that when a single transaction is described in multiple events, each event may populate different values of event.outcome, according to their perspective. Also note that in the case of a compound event (a single event that contains multiple logical events), this field should be populated with the value that best captures the overall success or failure from the perspective of the event producer. Further note that not all events will have an associated outcome. For example, this field is generally not populated for metric events, events with event.type:info, or any events for which an outcome does not make logical sense. |
keyword |
| event.provider | Source of the event. Event transports such as Syslog or the Windows Event Log typically mention the source of an event. It can be the name of the software that generated the event (e.g. Sysmon, httpd), or of a subsystem of the operating system (kernel, Microsoft-Windows-Security-Auditing). | keyword |
| event.reason | Reason why this event happened, according to the source. This describes the why of a particular action or outcome captured in the event. Where event.action captures the action from the event, event.reason describes why that action was taken. For example, a web proxy with an event.action which denied the request may also populate event.reason with the reason why (e.g. blocked site). |
keyword |
| event.sequence | Sequence number of the event. The sequence number is a value published by some event sources, to make the exact ordering of events unambiguous, regardless of the timestamp precision. | long |
| event.severity | The numeric severity of the event according to your event source. What the different severity values mean can be different between sources and use cases. It's up to the implementer to make sure severities are consistent across events from the same source. The Syslog severity belongs in log.syslog.severity.code. event.severity is meant to represent the severity according to the event source (e.g. firewall, IDS). If the event source does not publish its own severity, you may optionally copy the log.syslog.severity.code to event.severity. |
long |
| event.start | event.start contains the date when the event started or when the activity was first observed. |
date |
| event.timezone | This field should be populated when the event's timestamp does not include timezone information already (e.g. default Syslog timestamps). It's optional otherwise. Acceptable timezone formats are: a canonical ID (e.g. "Europe/Amsterdam"), abbreviated (e.g. "EST") or an HH:mm differential (e.g. "-05:00"). | keyword |
| event.type | This is one of four ECS Categorization Fields, and indicates the third level in the ECS category hierarchy. event.type represents a categorization "sub-bucket" that, when used along with the event.category field values, enables filtering events down to a level appropriate for single visualization. This field is an array. This will allow proper categorization of some events that fall in multiple event types. |
keyword |
| file.directory | Directory where the file is located. It should include the drive letter, when appropriate. | keyword |
| file.extension | File extension, excluding the leading dot. Note that when the file name has multiple extensions (example.tar.gz), only the last one should be captured ("gz", not "tar.gz"). | keyword |
| file.hash.md5 | MD5 hash. | keyword |
| file.hash.sha1 | SHA1 hash. | keyword |
| file.hash.sha256 | SHA256 hash. | keyword |
| file.hash.sha512 | SHA512 hash. | keyword |
| file.mime_type | MIME type should identify the format of the file or stream of bytes using https://www.iana.org/assignments/media-types/media-types.xhtml[IANA official types], where possible. When more than one type is applicable, the most specific type should be used. | keyword |
| file.name | Name of the file including the extension, without the directory. | keyword |
| file.size | File size in bytes. Only relevant when file.type is "file". |
long |
| host.architecture | Operating system architecture. | keyword |
| host.containerized | If the host is a container. | boolean |
| host.domain | Name of the domain of which the host is a member. For example, on Windows this could be the host's Active Directory domain or NetBIOS domain name. For Linux this could be the domain of the host's LDAP provider. | keyword |
| host.hostname | Hostname of the host. It normally contains what the hostname command returns on the host machine. |
keyword |
| host.id | Unique host id. As hostname is not always unique, use values that are meaningful in your environment. Example: The current usage of beat.name. |
keyword |
| host.ip | Host ip addresses. | ip |
| host.mac | Host mac addresses. | keyword |
| host.name | Name of the host. It can contain what hostname returns on Unix systems, the fully qualified domain name, or a name specified by the user. The sender decides which value to use. |
keyword |
| host.os.build | OS build information. | keyword |
| host.os.codename | OS codename, if any. | keyword |
| host.os.family | OS family (such as redhat, debian, freebsd, windows). | keyword |
| host.os.kernel | Operating system kernel version as a raw string. | keyword |
| host.os.name | Operating system name, without the version. | keyword |
| host.os.name.text | Multi-field of host.os.name. |
text |
| host.os.platform | Operating system platform (such centos, ubuntu, windows). | keyword |
| host.os.version | Operating system version as a raw string. | keyword |
| host.type | Type of host. For Cloud providers this can be the machine type like t2.medium. If vm, this could be the container, for example, or other information meaningful in your environment. |
keyword |
| http.request.method | HTTP request method. The value should retain its casing from the original event. For example, GET, get, and GeT are all considered valid values for this field. |
keyword |
| http.request.referrer | Referrer for this HTTP request. | keyword |
| http.response.status_code | HTTP response status code. | long |
| http.version | HTTP version. | keyword |
| input.type | Input type | keyword |
| log.file.path | Full path to the log file this event came from, including the file name. It should include the drive letter, when appropriate. If the event wasn't read from a log file, do not populate this field. | keyword |
| log.level | Original log level of the log event. If the source of the event provides a log level or textual severity, this is the one that goes in log.level. If your source doesn't specify one, you may put your event transport's severity here (e.g. Syslog severity). Some examples are warn, err, i, informational. |
keyword |
| log.logger | The name of the logger inside an application. This is usually the name of the class which initialized the logger, or can be a custom name. | keyword |
| log.offset | Log offset | long |
| log.source.address | keyword | |
| message | For log events the message field contains the log message, optimized for viewing in a log viewer. For structured logs without an original message field, other fields can be concatenated to form a human-readable summary of the event. If multiple messages exist, they can be combined into one message. | match_only_text |
| network.bytes | Total bytes transferred in both directions. If source.bytes and destination.bytes are known, network.bytes is their sum. |
long |
| network.community_id | A hash of source and destination IPs and ports, as well as the protocol used in a communication. This is a tool-agnostic standard to identify flows. Learn more at https://github.com/corelight/community-id-spec. | keyword |
| network.direction | Direction of the network traffic. When mapping events from a host-based monitoring context, populate this field from the host's point of view, using the values "ingress" or "egress". When mapping events from a network or perimeter-based monitoring context, populate this field from the point of view of the network perimeter, using the values "inbound", "outbound", "internal" or "external". Note that "internal" is not crossing perimeter boundaries, and is meant to describe communication between two hosts within the perimeter. Note also that "external" is meant to describe traffic between two hosts that are external to the perimeter. This could for example be useful for ISPs or VPN service providers. | keyword |
| network.packets | Total packets transferred in both directions. If source.packets and destination.packets are known, network.packets is their sum. |
long |
| network.protocol | In the OSI Model this would be the Application Layer protocol. For example, http, dns, or ssh. The field value must be normalized to lowercase for querying. |
keyword |
| network.transport | Same as network.iana_number, but instead using the Keyword name of the transport layer (udp, tcp, ipv6-icmp, etc.) The field value must be normalized to lowercase for querying. | keyword |
| observer.egress.interface.name | Interface name as reported by the system. | keyword |
| observer.egress.zone | Network zone of outbound traffic as reported by the observer to categorize the destination area of egress traffic, e.g. Internal, External, DMZ, HR, Legal, etc. | keyword |
| observer.hostname | Hostname of the observer. | keyword |
| observer.ingress.interface.name | Interface name as reported by the system. | keyword |
| observer.ingress.zone | Network zone of incoming traffic as reported by the observer to categorize the source area of ingress traffic. e.g. internal, External, DMZ, HR, Legal, etc. | keyword |
| observer.product | The product name of the observer. | keyword |
| observer.serial_number | Observer serial number. | keyword |
| observer.type | The type of the observer the data is coming from. There is no predefined list of observer types. Some examples are forwarder, firewall, ids, ips, proxy, poller, sensor, APM server. |
keyword |
| observer.vendor | Vendor name of the observer. | keyword |
| related.hash | All the hashes seen on your event. Populating this field, then using it to search for hashes can help in situations where you're unsure what the hash algorithm is (and therefore which key name to search). | keyword |
| related.hosts | All hostnames or other host identifiers seen on your event. Example identifiers include FQDNs, domain names, workstation names, or aliases. | keyword |
| related.ip | All of the IPs seen on your event. | ip |
| related.user | All the user names or other user identifiers seen on the event. | keyword |
| rule.category | A categorization value keyword used by the entity using the rule for detection of this event. | keyword |
| rule.id | A rule ID that is unique within the scope of an agent, observer, or other entity using the rule for detection of this event. | keyword |
| rule.name | The name of the rule or signature generating the event. | keyword |
| rule.ruleset | Name of the ruleset, policy, group, or parent category in which the rule used to generate this event is a member. | keyword |
| sophos.xg.action | Event Action | keyword |
| sophos.xg.activityname | Web policy activity that matched and caused the policy result. | keyword |
| sophos.xg.ap | Access Point Serial ID or LocalWifi0 or LocalWifi1. | keyword |
| sophos.xg.app_category | Name of the category under which application falls | keyword |
| sophos.xg.app_filter_policy_id | Application filter policy ID applied on the traffic | keyword |
| sophos.xg.app_is_cloud | Application is Cloud | keyword |
| sophos.xg.app_name | Application name | keyword |
| sophos.xg.app_resolved_by | Application is resolved by signature or synchronized application | keyword |
| sophos.xg.app_risk | Risk level assigned to the application | keyword |
| sophos.xg.app_technology | Technology of the application | keyword |
| sophos.xg.appfilter_policy_id | Application Filter policy applied on the traffic | integer |
| sophos.xg.application | Application name | keyword |
| sophos.xg.application_category | Application is resolved by signature or synchronized application | keyword |
| sophos.xg.application_filter_policy | Application Filter policy applied on the traffic | integer |
| sophos.xg.application_name | Application name | keyword |
| sophos.xg.application_risk | Risk level assigned to the application | keyword |
| sophos.xg.application_technology | Technology of the application | keyword |
| sophos.xg.appresolvedby | Technology of the application | keyword |
| sophos.xg.auth_client | Auth Client | keyword |
| sophos.xg.auth_mechanism | Auth mechanism | keyword |
| sophos.xg.av_policy_name | Malware scanning policy name which is applied on the traffic | keyword |
| sophos.xg.backup_mode | Backup mode | keyword |
| sophos.xg.branch_name | Branch Name | keyword |
| sophos.xg.category | IPS signature category. | keyword |
| sophos.xg.category_type | Type of category under which website falls | keyword |
| sophos.xg.classification | Signature classification | keyword |
| sophos.xg.client_host_name | Client host name | keyword |
| sophos.xg.client_physical_address | Client physical address | keyword |
| sophos.xg.clients_conn_ssid | Number of client connected to the SSID. | long |
| sophos.xg.collisions | collisions | long |
| sophos.xg.con_event | Event Start/Stop | keyword |
| sophos.xg.con_id | Unique identifier of connection | integer |
| sophos.xg.configuration | Configuration | float |
| sophos.xg.conn_id | Unique identifier of connection | integer |
| sophos.xg.connectionname | Connectionname | keyword |
| sophos.xg.connectiontype | Connectiontype | keyword |
| sophos.xg.connevent | Event on which this log is generated | keyword |
| sophos.xg.connid | Connection ID | keyword |
| sophos.xg.content_type | Type of the content | keyword |
| sophos.xg.contenttype | Type of the content | keyword |
| sophos.xg.context_match | Context Match | keyword |
| sophos.xg.context_prefix | Content Prefix | keyword |
| sophos.xg.context_suffix | Context Suffix | keyword |
| sophos.xg.cookie | cookie | keyword |
| sophos.xg.date | Date (yyyy-mm-dd) when the event occurred | date |
| sophos.xg.destinationip | Original destination IP address of traffic | ip |
| sophos.xg.device | device | keyword |
| sophos.xg.device_id | Serial number of the device | keyword |
| sophos.xg.device_model | Model number of the device | keyword |
| sophos.xg.device_name | Model number of the device | keyword |
| sophos.xg.dictionary_name | Dictionary Name | keyword |
| sophos.xg.dir_disp | TPacket direction. Possible values:“org”, “reply”, “” | keyword |
| sophos.xg.direction | Direction | keyword |
| sophos.xg.domainname | Domain from which virus was downloaded | keyword |
| sophos.xg.download_file_name | Download file name | keyword |
| sophos.xg.download_file_type | Download file type | keyword |
| sophos.xg.dst_country_code | Code of the country to which the destination IP belongs | keyword |
| sophos.xg.dst_domainname | Receiver domain name | keyword |
| sophos.xg.dst_ip | Original destination IP address of traffic | ip |
| sophos.xg.dst_port | Original destination port of TCP and UDP traffic | integer |
| sophos.xg.dst_zone_type | Type of destination zone | keyword |
| sophos.xg.dstdomain | Destination Domain | keyword |
| sophos.xg.duration | Durability of traffic (seconds) | long |
| sophos.xg.email_subject | Email Subject | keyword |
| sophos.xg.ep_uuid | Endpoint UUID | keyword |
| sophos.xg.ether_type | ethernet frame type | keyword |
| sophos.xg.eventid | ATP Evenet ID | keyword |
| sophos.xg.eventtime | Event time | date |
| sophos.xg.eventtype | ATP event type | keyword |
| sophos.xg.exceptions | List of the checks excluded by web exceptions. | keyword |
| sophos.xg.execution_path | ATP execution path | keyword |
| sophos.xg.extra | extra | keyword |
| sophos.xg.file_name | Filename | keyword |
| sophos.xg.file_path | File path | keyword |
| sophos.xg.file_size | File Size | integer |
| sophos.xg.filename | File name associated with the event | keyword |
| sophos.xg.filepath | Path of the file containing virus | keyword |
| sophos.xg.filesize | Size of the file that contained virus | integer |
| sophos.xg.free | free | integer |
| sophos.xg.from_email_address | Sender email address | keyword |
| sophos.xg.ftp_direction | Direction of FTP transfer: Upload or Download | keyword |
| sophos.xg.ftp_url | FTP URL from which virus was downloaded | keyword |
| sophos.xg.ftpcommand | FTP command used when virus was found | keyword |
| sophos.xg.fw_rule_id | Firewall Rule ID which is applied on the traffic | integer |
| sophos.xg.fw_rule_name | Firewall rule name which is applied on the traffic | keyword |
| sophos.xg.fw_rule_section | Firewall rule section which is applied on the traffic | keyword |
| sophos.xg.fw_rule_type | Firewall rule type which is applied on the traffic | keyword |
| sophos.xg.hb_health | Heartbeat status | keyword |
| sophos.xg.hb_status | Heartbeat status | keyword |
| sophos.xg.host | Host | keyword |
| sophos.xg.http_category | HTTP Category | keyword |
| sophos.xg.http_category_type | HTTP Category Type | keyword |
| sophos.xg.httpresponsecode | code of HTTP response | long |
| sophos.xg.iap | Internet Access policy ID applied on the traffic | keyword |
| sophos.xg.icmp_code | ICMP code of ICMP traffic | keyword |
| sophos.xg.icmp_type | ICMP type of ICMP traffic | keyword |
| sophos.xg.idle_cpu | idle ## | float |
| sophos.xg.idp_policy_id | IPS policy ID which is applied on the traffic | integer |
| sophos.xg.idp_policy_name | IPS policy name i.e. IPS policy name which is applied on the traffic | keyword |
| sophos.xg.in_interface | Interface for incoming traffic, e.g., Port A | keyword |
| sophos.xg.interface | interface | keyword |
| sophos.xg.ipaddress | Ipaddress | keyword |
| sophos.xg.ips_policy_id | IPS policy ID applied on the traffic | integer |
| sophos.xg.lease_time | Lease Time | keyword |
| sophos.xg.localgateway | Localgateway | keyword |
| sophos.xg.localnetwork | Localnetwork | keyword |
| sophos.xg.log_component | Component responsible for logging e.g. Firewall rule | keyword |
| sophos.xg.log_id | Unique 12 characters code (0101011) | keyword |
| sophos.xg.log_subtype | Sub type of event | keyword |
| sophos.xg.log_type | Type of event e.g. firewall event | keyword |
| sophos.xg.log_version | Log Version | keyword |
| sophos.xg.login_user | ATP login user | keyword |
| sophos.xg.mailid | mailid | keyword |
| sophos.xg.mailsize | mailsize | integer |
| sophos.xg.message | Message | keyword |
| sophos.xg.mode | Mode | keyword |
| sophos.xg.nat_rule_id | NAT Rule ID | keyword |
| sophos.xg.newversion | Newversion | keyword |
| sophos.xg.oldversion | Oldversion | keyword |
| sophos.xg.out_interface | Interface for outgoing traffic, e.g., Port B | keyword |
| sophos.xg.override_authorizer | Override authorizer | keyword |
| sophos.xg.override_name | Override name | keyword |
| sophos.xg.override_token | Override token | keyword |
| sophos.xg.phpsessid | PHP session ID | keyword |
| sophos.xg.platform | Platform of the traffic. | keyword |
| sophos.xg.policy_type | Policy type applied to the traffic | keyword |
| sophos.xg.priority | Severity level of traffic | keyword |
| sophos.xg.protocol | Protocol number of traffic | keyword |
| sophos.xg.qualifier | Qualifier | keyword |
| sophos.xg.quarantine | Path and filename of the file quarantined | keyword |
| sophos.xg.quarantine_reason | Quarantine reason | keyword |
| sophos.xg.querystring | querystring | keyword |
| sophos.xg.raw_data | Raw data | keyword |
| sophos.xg.received_pkts | Total number of packets received | long |
| sophos.xg.receiveddrops | received drops | long |
| sophos.xg.receivederrors | received errors | keyword |
| sophos.xg.receivedkbits | received kbits | long |
| sophos.xg.recv_bytes | Total number of bytes received | long |
| sophos.xg.red_id | RED ID | keyword |
| sophos.xg.referer | Referer | keyword |
| sophos.xg.remote_ip | Remote IP | ip |
| sophos.xg.remotenetwork | remotenetwork | keyword |
| sophos.xg.reported_host | Reported Host | keyword |
| sophos.xg.reported_ip | Reported IP | keyword |
| sophos.xg.reports | Reports | float |
| sophos.xg.rule_priority | Priority of IPS policy | keyword |
| sophos.xg.sent_bytes | Total number of bytes sent | long |
| sophos.xg.sent_pkts | Total number of packets sent | long |
| sophos.xg.server | Server | keyword |
| sophos.xg.sessionid | Sessionid | keyword |
| sophos.xg.sha1sum | SHA1 checksum of the item being analyzed | keyword |
| sophos.xg.signature | Signature | float |
| sophos.xg.signature_id | Signature ID | keyword |
| sophos.xg.signature_msg | Signature messsage | keyword |
| sophos.xg.site_category | Site Category | keyword |
| sophos.xg.source | Source | keyword |
| sophos.xg.sourceip | Original source IP address of traffic | ip |
| sophos.xg.spamaction | Spam Action | keyword |
| sophos.xg.sqli | related SQLI caught by the WAF | keyword |
| sophos.xg.src_country_code | Code of the country to which the source IP belongs | keyword |
| sophos.xg.src_domainname | Sender domain name | keyword |
| sophos.xg.src_ip | Original source IP address of traffic | ip |
| sophos.xg.src_mac | Original source MAC address of traffic | keyword |
| sophos.xg.src_port | Original source port of TCP and UDP traffic | integer |
| sophos.xg.src_zone_type | Type of source zone | keyword |
| sophos.xg.ssid | Configured SSID name. | keyword |
| sophos.xg.start_time | Start time | date |
| sophos.xg.starttime | Starttime | date |
| sophos.xg.status | Ultimate status of traffic – Allowed or Denied | keyword |
| sophos.xg.status_code | Status code | keyword |
| sophos.xg.subject | Email subject | keyword |
| sophos.xg.syslog_server_name | Syslog server name. | keyword |
| sophos.xg.system_cpu | system | float |
| sophos.xg.target | Platform of the traffic. | keyword |
| sophos.xg.temp | Temp | float |
| sophos.xg.threatname | ATP threatname | keyword |
| sophos.xg.timestamp | timestamp | date |
| sophos.xg.timezone | Original reported timezone for the event timestamp. | keyword |
| sophos.xg.to_email_address | Receipeint email address | keyword |
| sophos.xg.total_memory | Total Memory | integer |
| sophos.xg.trans_dst_ip | Translated destination IP address for outgoing traffic | ip |
| sophos.xg.trans_dst_port | Translated destination port for outgoing traffic | integer |
| sophos.xg.trans_src_ip | Translated source IP address for outgoing traffic | ip |
| sophos.xg.trans_src_port | Translated source port for outgoing traffic | integer |
| sophos.xg.transaction_id | Transaction ID | keyword |
| sophos.xg.transactionid | Transaction ID of the AV scan. | keyword |
| sophos.xg.transmitteddrops | transmitted drops | long |
| sophos.xg.transmittederrors | transmitted errors | keyword |
| sophos.xg.transmittedkbits | transmitted kbits | long |
| sophos.xg.unit | unit | keyword |
| sophos.xg.updatedip | updatedip | ip |
| sophos.xg.upload_file_name | Upload file name | keyword |
| sophos.xg.upload_file_type | Upload file type | keyword |
| sophos.xg.url | URL from which virus was downloaded | keyword |
| sophos.xg.used | used | integer |
| sophos.xg.used_quota | Used Quota | keyword |
| sophos.xg.user | User | keyword |
| sophos.xg.user_cpu | system | float |
| sophos.xg.user_gp | Group name to which the user belongs. | keyword |
| sophos.xg.user_group | Group name to which the user belongs | keyword |
| sophos.xg.user_name | user_name | keyword |
| sophos.xg.users | Number of users from System Health / Live User events. | long |
| sophos.xg.vconn_id | Connection ID of the master connection | integer |
| sophos.xg.virus | virus name | keyword |
| sophos.xg.web_policy_id | Web policy ID | keyword |
| sophos.xg.website | Website | keyword |
| sophos.xg.xss | related XSS caught by the WAF | keyword |
| source.as.number | Unique number allocated to the autonomous system. The autonomous system number (ASN) uniquely identifies each network on the Internet. | long |
| source.as.organization.name | Organization name. | keyword |
| source.as.organization.name.text | Multi-field of source.as.organization.name. |
match_only_text |
| source.bytes | Bytes sent from the source to the destination. | long |
| source.domain | The domain name of the source system. This value may be a host name, a fully qualified domain name, or another host naming format. The value may derive from the original event or be added from enrichment. | keyword |
| source.geo.city_name | City name. | keyword |
| source.geo.continent_name | Name of the continent. | keyword |
| source.geo.country_iso_code | Country ISO code. | keyword |
| source.geo.country_name | Country name. | keyword |
| source.geo.location | Longitude and latitude. | geo_point |
| source.geo.name | User-defined description of a location, at the level of granularity they care about. Could be the name of their data centers, the floor number, if this describes a local physical entity, city names. Not typically used in automated geolocation. | keyword |
| source.geo.region_iso_code | Region ISO code. | keyword |
| source.geo.region_name | Region name. | keyword |
| source.ip | IP address of the source (IPv4 or IPv6). | ip |
| source.mac | MAC address of the source. The notation format from RFC 7042 is suggested: Each octet (that is, 8-bit byte) is represented by two [uppercase] hexadecimal digits giving the value of the octet as an unsigned integer. Successive octets are separated by a hyphen. | keyword |
| source.nat.ip | Translated ip of source based NAT sessions (e.g. internal client to internet) Typically connections traversing load balancers, firewalls, or routers. | ip |
| source.nat.port | Translated port of source based NAT sessions. (e.g. internal client to internet) Typically used with load balancers, firewalls, or routers. | long |
| source.packets | Packets sent from the source to the destination. | long |
| source.port | Port of the source. | long |
| source.user.domain | Name of the directory the user is a member of. For example, an LDAP or Active Directory domain name. | keyword |
| source.user.email | User email address. | keyword |
| source.user.group.name | Name of the group. | keyword |
| source.user.name | Short name or login of the user. | keyword |
| source.user.name.text | Multi-field of source.user.name. |
match_only_text |
| tags | List of keywords used to tag each event. | keyword |
| url.domain | Domain of the url, such as "www.elastic.co". In some cases a URL may refer to an IP and/or port directly, without a domain name. In this case, the IP address would go to the domain field. If the URL contains a literal IPv6 address enclosed by [ and ] (IETF RFC 2732), the [ and ] characters should also be captured in the domain field. |
keyword |
| url.extension | The field contains the file extension from the original request url, excluding the leading dot. The file extension is only set if it exists, as not every url has a file extension. The leading period must not be included. For example, the value must be "png", not ".png". Note that when the file name has multiple extensions (example.tar.gz), only the last one should be captured ("gz", not "tar.gz"). | keyword |
| url.fragment | Portion of the url after the #, such as "top". The # is not part of the fragment. |
keyword |
| url.full | If full URLs are important to your use case, they should be stored in url.full, whether this field is reconstructed or present in the event source. |
wildcard |
| url.full.text | Multi-field of url.full. |
match_only_text |
| url.original | Unmodified original url as seen in the event source. Note that in network monitoring, the observed URL may be a full URL, whereas in access logs, the URL is often just represented as a path. This field is meant to represent the URL as it was observed, complete or not. | wildcard |
| url.original.text | Multi-field of url.original. |
match_only_text |
| url.password | Password of the request. | keyword |
| url.path | Path of the request, such as "/search". | wildcard |
| url.port | Port of the request, such as 443. | long |
| url.query | The query field describes the query string of the request, such as "q=elasticsearch". The ? is excluded from the query string. If a URL contains no ?, there is no query field. If there is a ? but no query, the query field exists with an empty string. The exists query can be used to differentiate between the two cases. |
keyword |
| url.registered_domain | The highest registered url domain, stripped of the subdomain. For example, the registered domain for "foo.example.com" is "example.com". This value can be determined precisely with a list like the public suffix list (https://publicsuffix.org). Trying to approximate this by simply taking the last two labels will not work well for TLDs such as "co.uk". | keyword |
| url.scheme | Scheme of the request, such as "https". Note: The : is not part of the scheme. |
keyword |
| url.subdomain | The subdomain portion of a fully qualified domain name includes all of the names except the host name under the registered_domain. In a partially qualified domain, or if the the qualification level of the full name cannot be determined, subdomain contains all of the names below the registered domain. For example the subdomain portion of "www.east.example.com" is "east". If the domain has multiple levels of subdomain, such as "sub2.sub1.example.com", the subdomain field should contain "sub2.sub1", with no trailing period. | keyword |
| url.top_level_domain | The effective top level domain (eTLD), also known as the domain suffix, is the last part of the domain name. For example, the top level domain for example.com is "com". This value can be determined precisely with a list like the public suffix list (https://publicsuffix.org). Trying to approximate this by simply taking the last label will not work well for effective TLDs such as "co.uk". | keyword |
| url.username | Username of the request. | keyword |
| user.domain | Name of the directory the user is a member of. For example, an LDAP or Active Directory domain name. | keyword |
| user.email | User email address. | keyword |
| user.name | Short name or login of the user. | keyword |
| user.name.text | Multi-field of user.name. |
match_only_text |
| user_agent.device.name | Name of the device. | keyword |
| user_agent.name | Name of the user agent. | keyword |
| user_agent.original | Unparsed user_agent string. | keyword |
| user_agent.original.text | Multi-field of user_agent.original. |
match_only_text |
| user_agent.os.family | OS family (such as redhat, debian, freebsd, windows). | keyword |
| user_agent.os.full | Operating system name, including the version or code name. | keyword |
| user_agent.os.full.text | Multi-field of user_agent.os.full. |
match_only_text |
| user_agent.os.kernel | Operating system kernel version as a raw string. | keyword |
| user_agent.os.name | Operating system name, without the version. | keyword |
| user_agent.os.name.text | Multi-field of user_agent.os.name. |
match_only_text |
| user_agent.os.platform | Operating system platform (such centos, ubuntu, windows). | keyword |
| user_agent.os.version | Operating system version as a raw string. | keyword |
| user_agent.version | Version of the user agent. | keyword |
Example
{
    "@timestamp": "2016-12-02T18:50:20.000Z",
    "agent": {
        "ephemeral_id": "244d391d-55cb-405e-baff-e091145a351c",
        "id": "e756de30-a6b6-437a-8c56-cd75349c61bf",
        "name": "docker-fleet-agent",
        "type": "filebeat",
        "version": "8.10.3"
    },
    "data_stream": {
        "dataset": "sophos.xg",
        "namespace": "ep",
        "type": "logs"
    },
    "ecs": {
        "version": "8.17.0"
    },
    "elastic_agent": {
        "id": "e756de30-a6b6-437a-8c56-cd75349c61bf",
        "snapshot": false,
        "version": "8.10.3"
    },
    "event": {
        "action": "alert",
        "agent_id_status": "verified",
        "category": [
            "network"
        ],
        "code": "16010",
        "dataset": "sophos.xg",
        "ingested": "2023-11-15T05:39:21Z",
        "kind": "event",
        "outcome": "success",
        "severity": 1,
        "timezone": "GMT"
    },
    "host": {
        "name": "XG230"
    },
    "input": {
        "type": "tcp"
    },
    "log": {
        "level": "alert",
        "source": {
            "address": "192.168.32.4:40336"
        }
    },
    "observer": {
        "product": "XG",
        "serial_number": "1234567890123456",
        "type": "firewall",
        "vendor": "Sophos"
    },
    "related": {
        "hosts": [
            "XG230"
        ],
        "ip": [
            "10.108.108.49"
        ]
    },
    "sophos": {
        "xg": {
            "action": "Deny",
            "context_match": "Not",
            "context_prefix": "blah blah hello ",
            "context_suffix": " hello blah ",
            "device": "SFW",
            "device_name": "SF01V",
            "dictionary_name": "complicated_Custom",
            "direction": "in",
            "file_name": "cgi_echo.pl",
            "log_component": "Web Content Policy",
            "log_id": "058420116010",
            "log_subtype": "Alert",
            "log_type": "Content Filtering",
            "site_category": "Information Technology",
            "timezone": "GMT",
            "transaction_id": "e4a127f7-a850-477c-920e-a471b38727c1",
            "user": "gi123456",
            "website": "ta-web-static-testing.qa. astaro.de"
        }
    },
    "source": {
        "ip": "10.108.108.49"
    },
    "tags": [
        "sophos-xg",
        "forwarded"
    ]
}
This integration includes one or more Kibana dashboards that visualizes the data collected by the integration. The screenshots below illustrate how the ingested data is displayed.
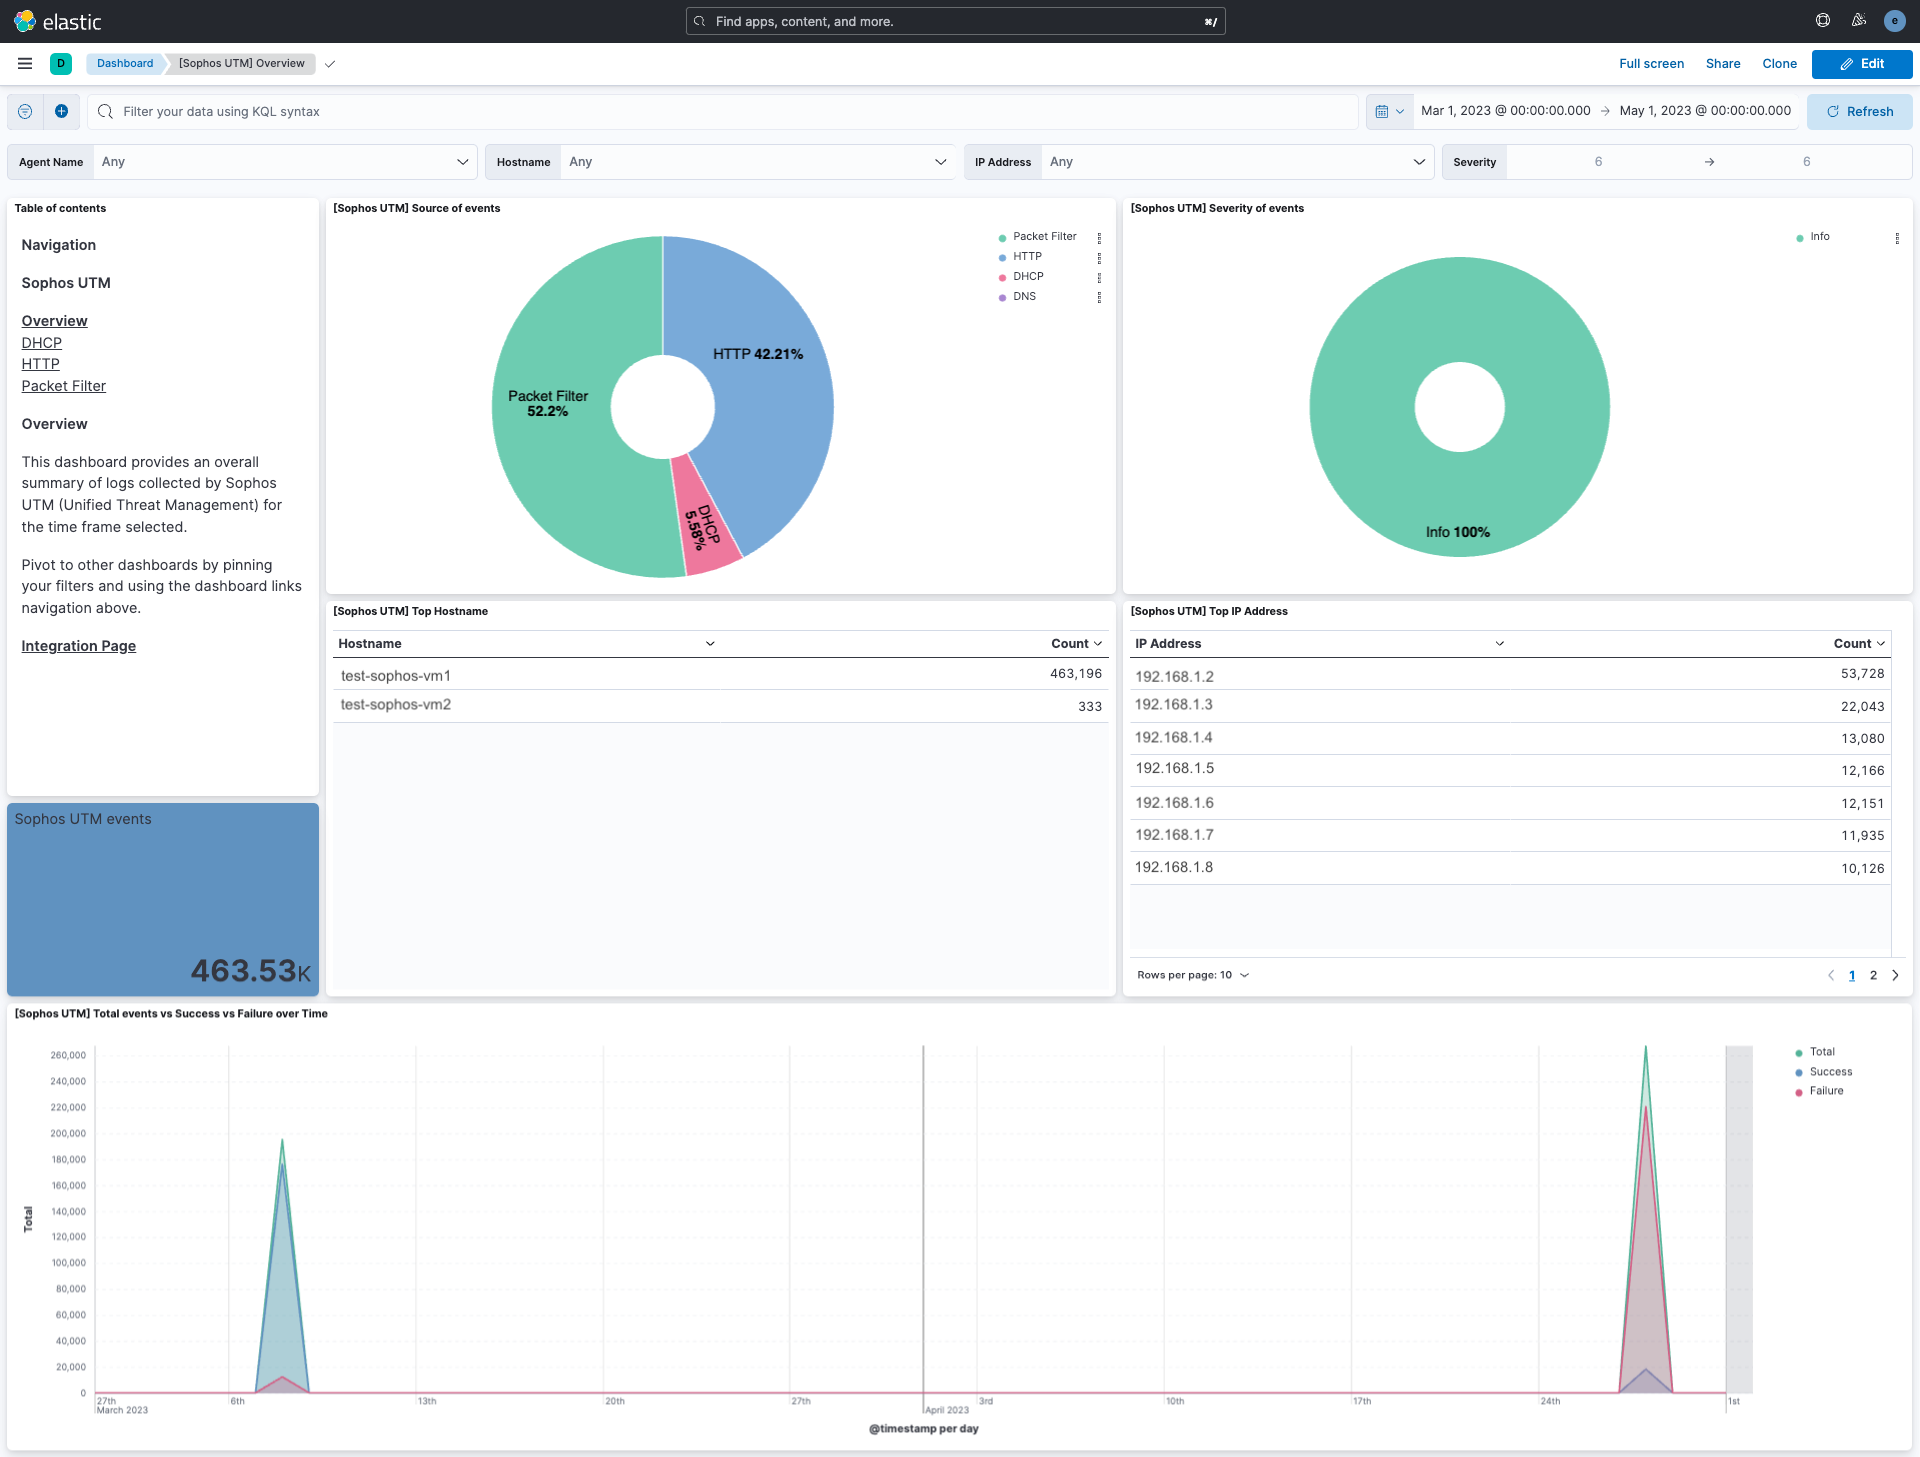
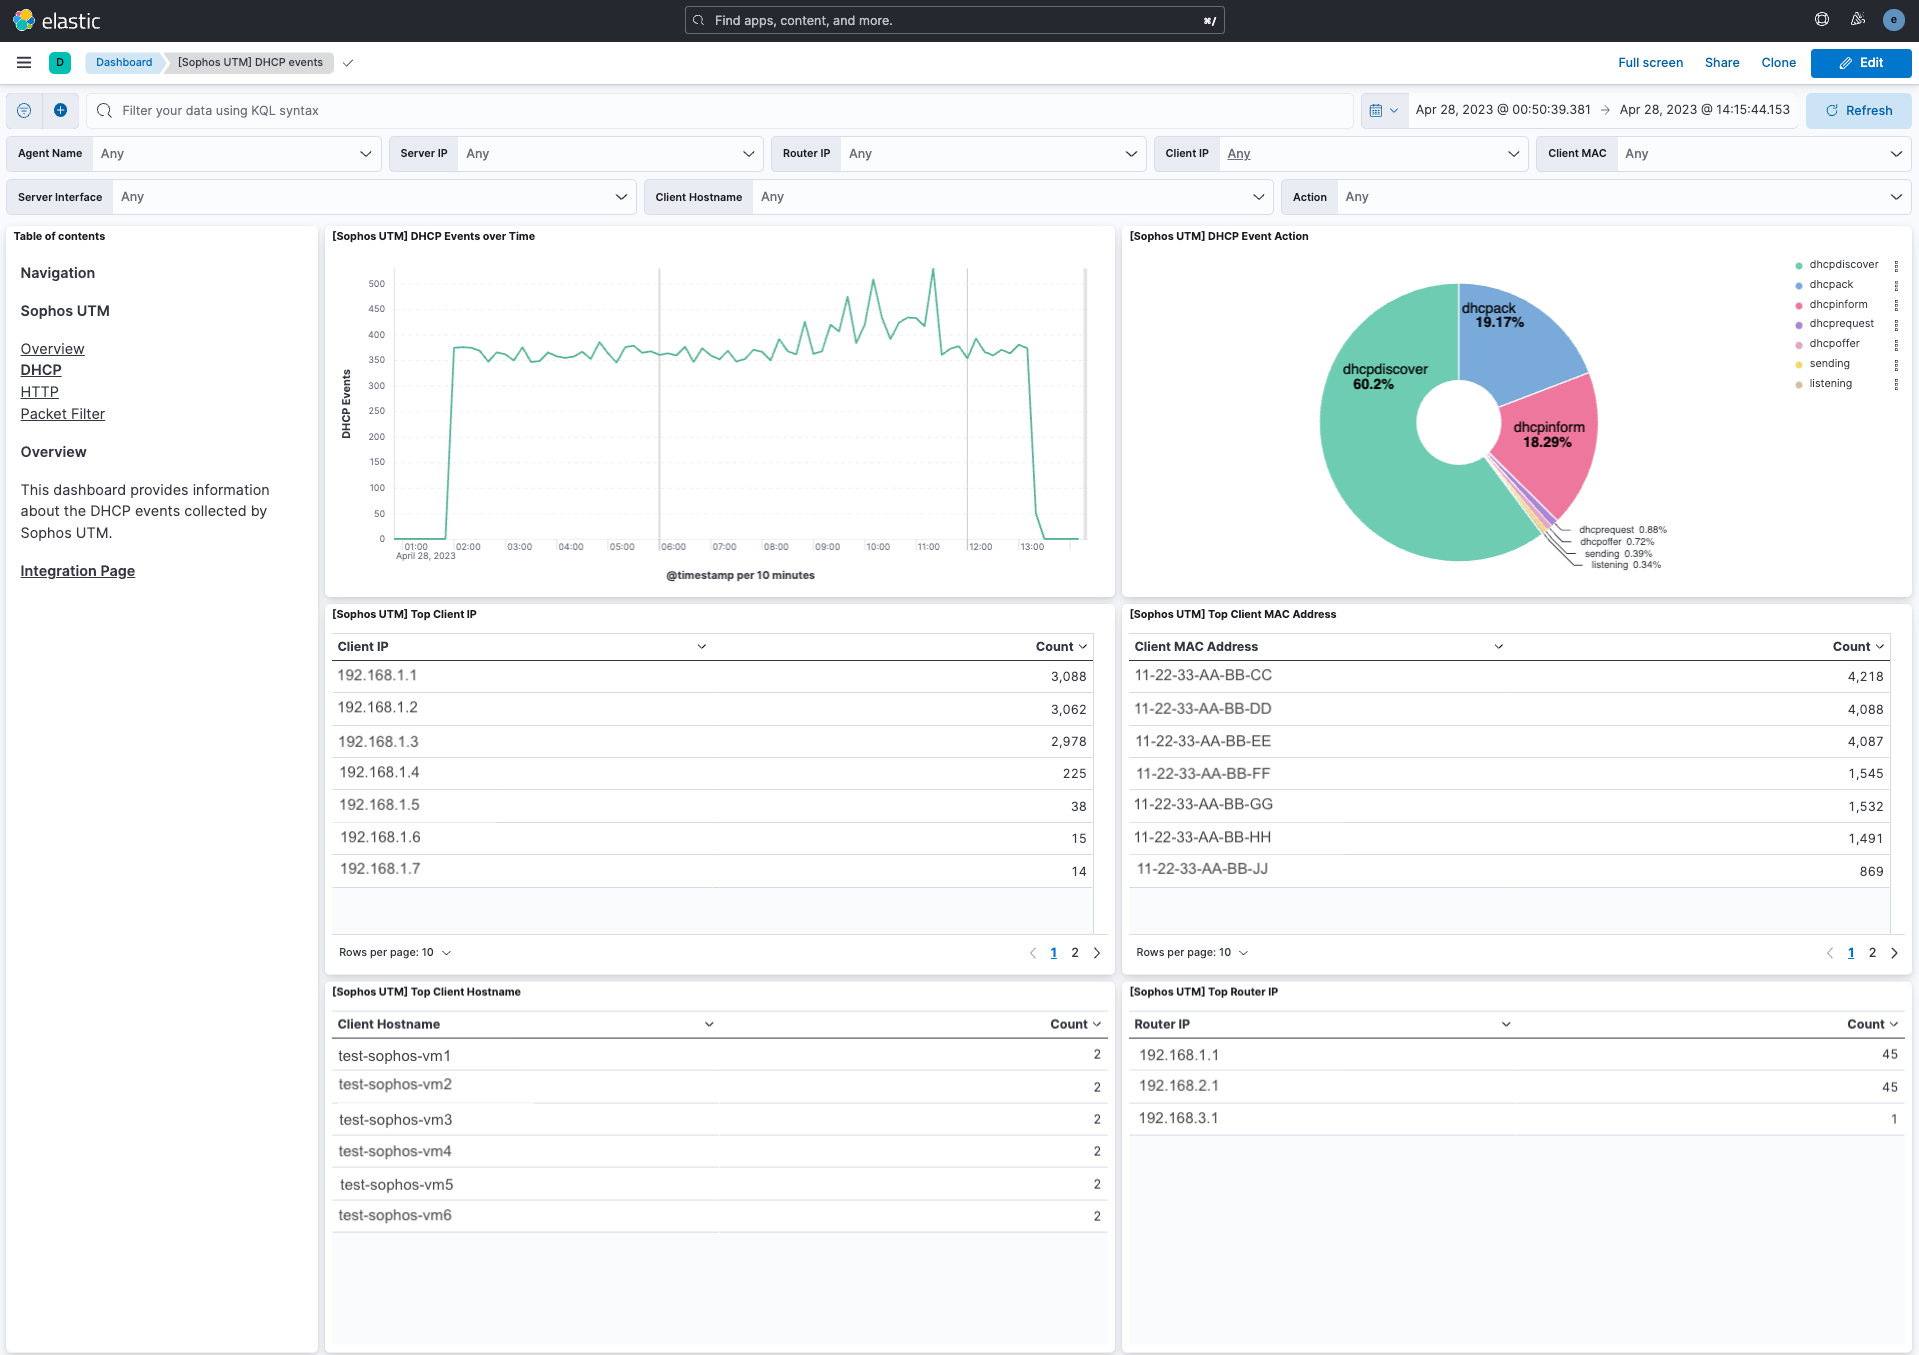
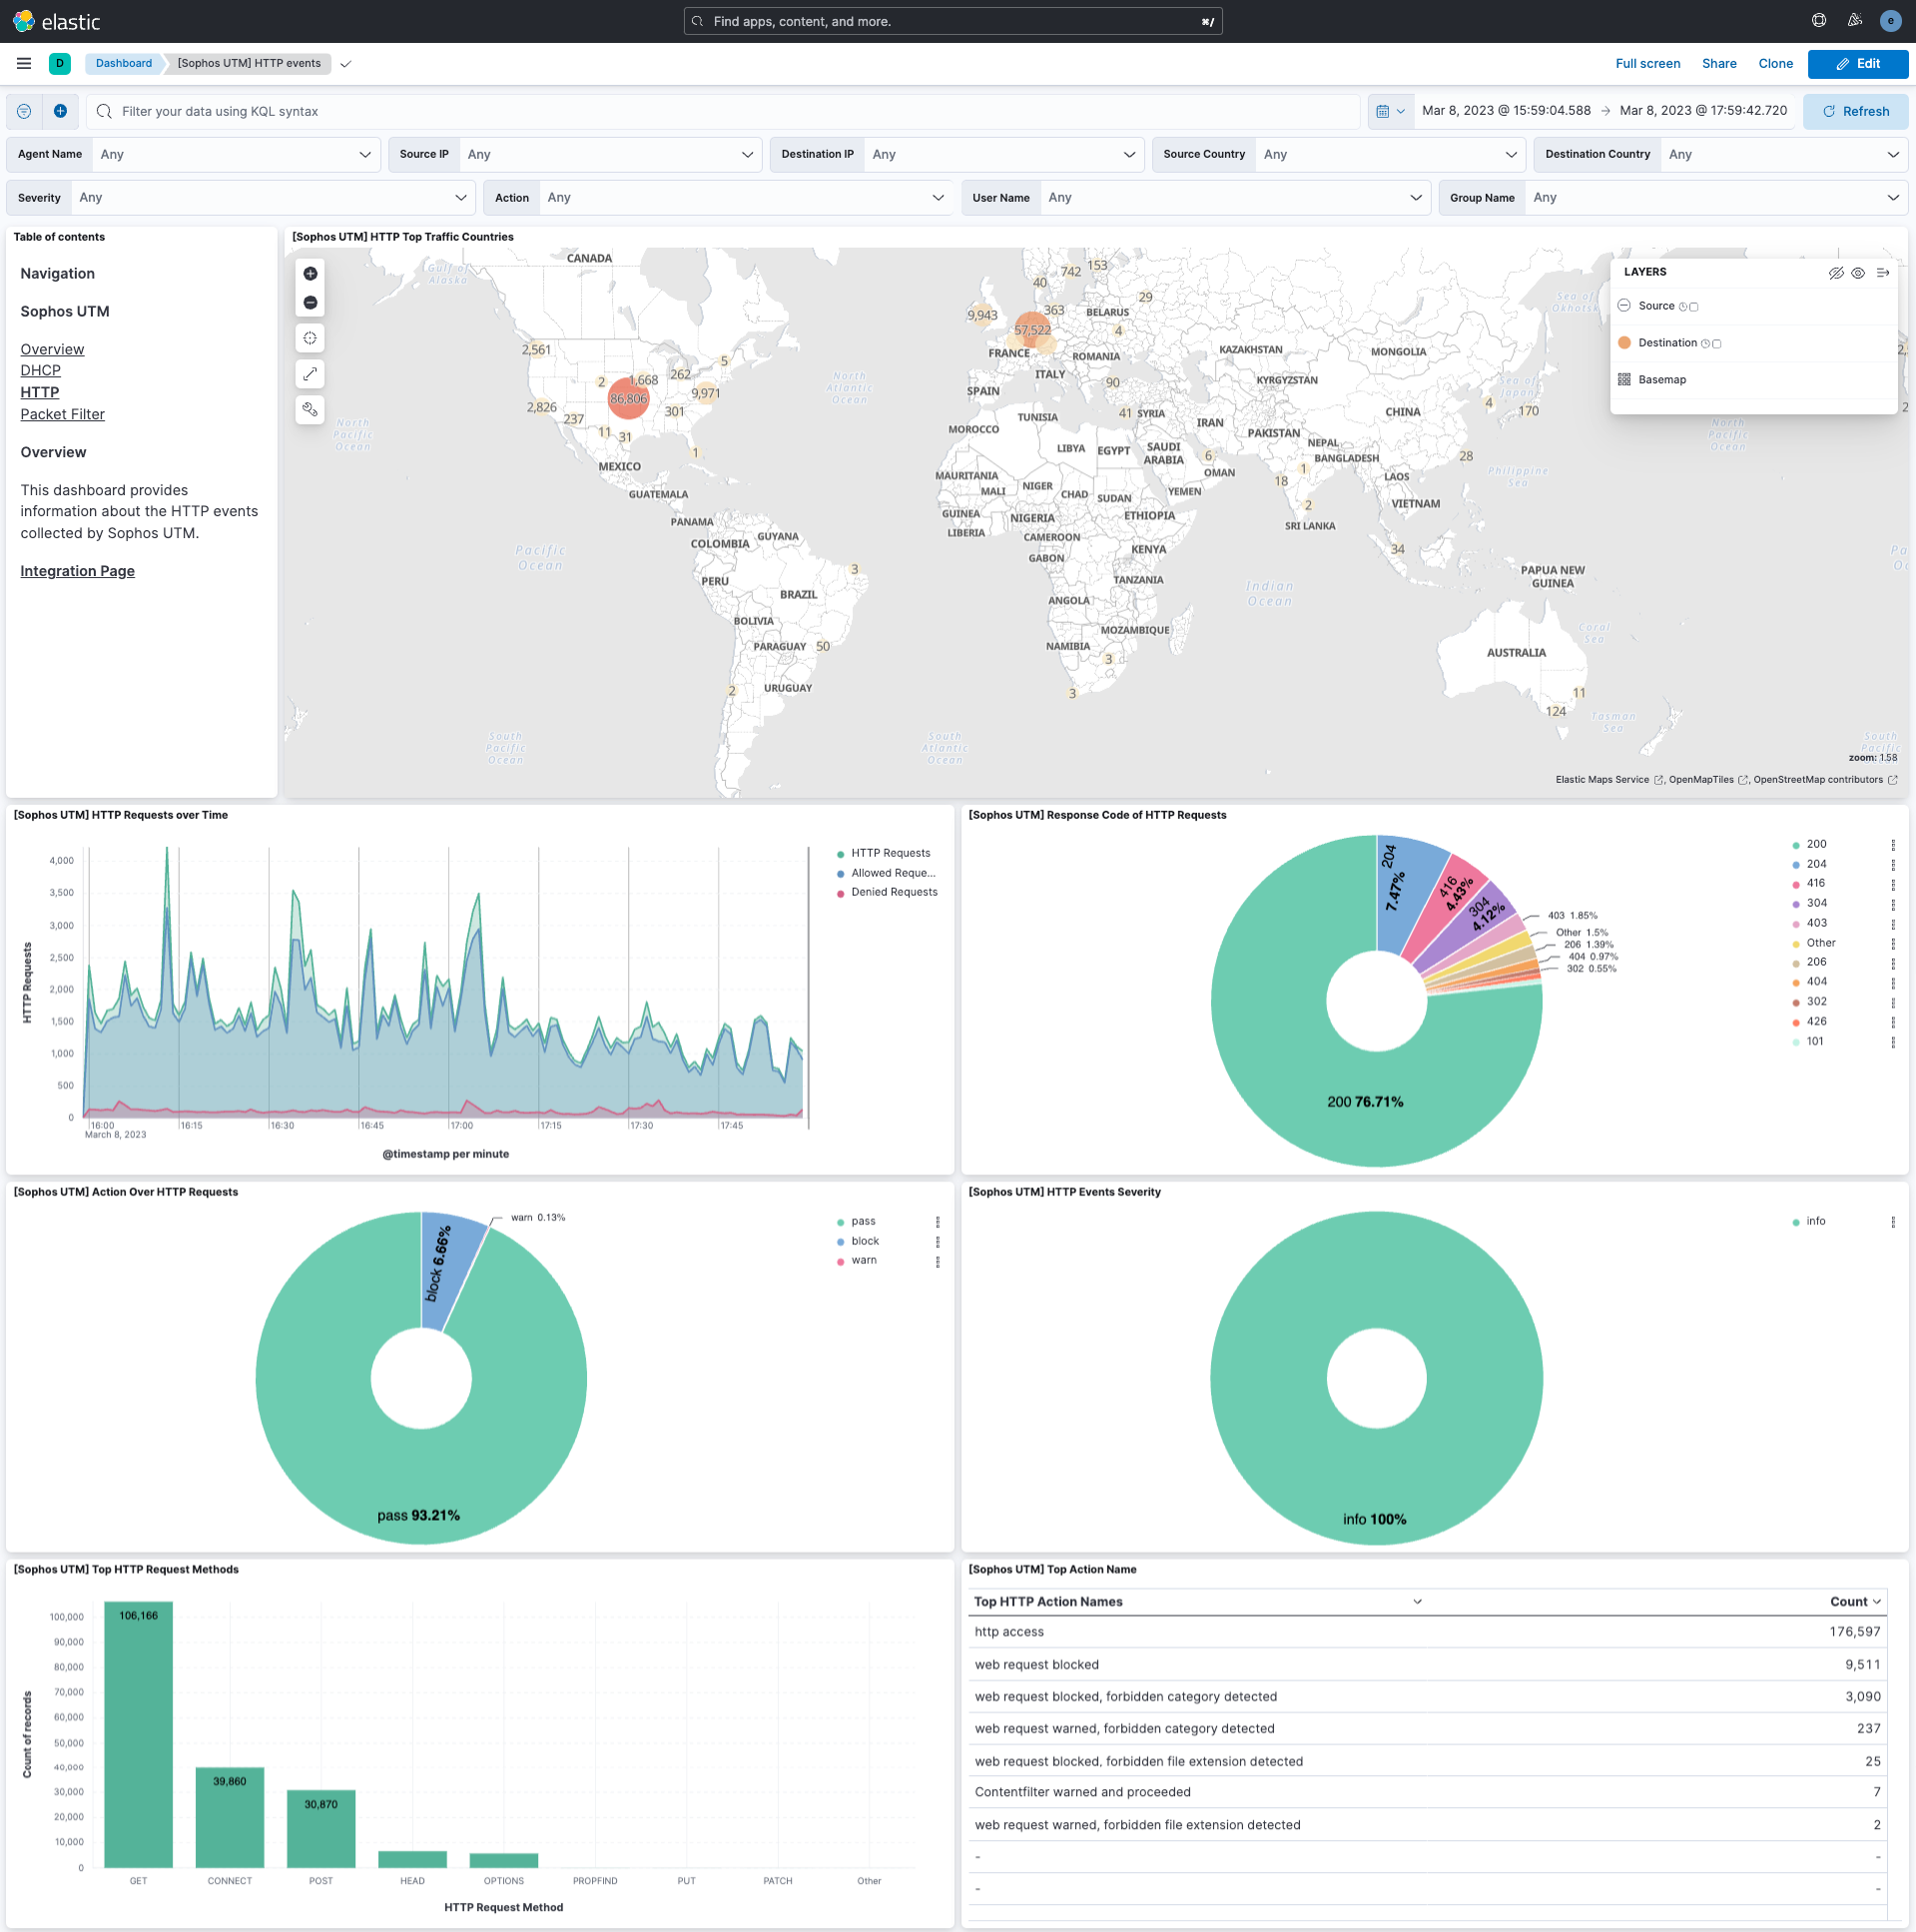
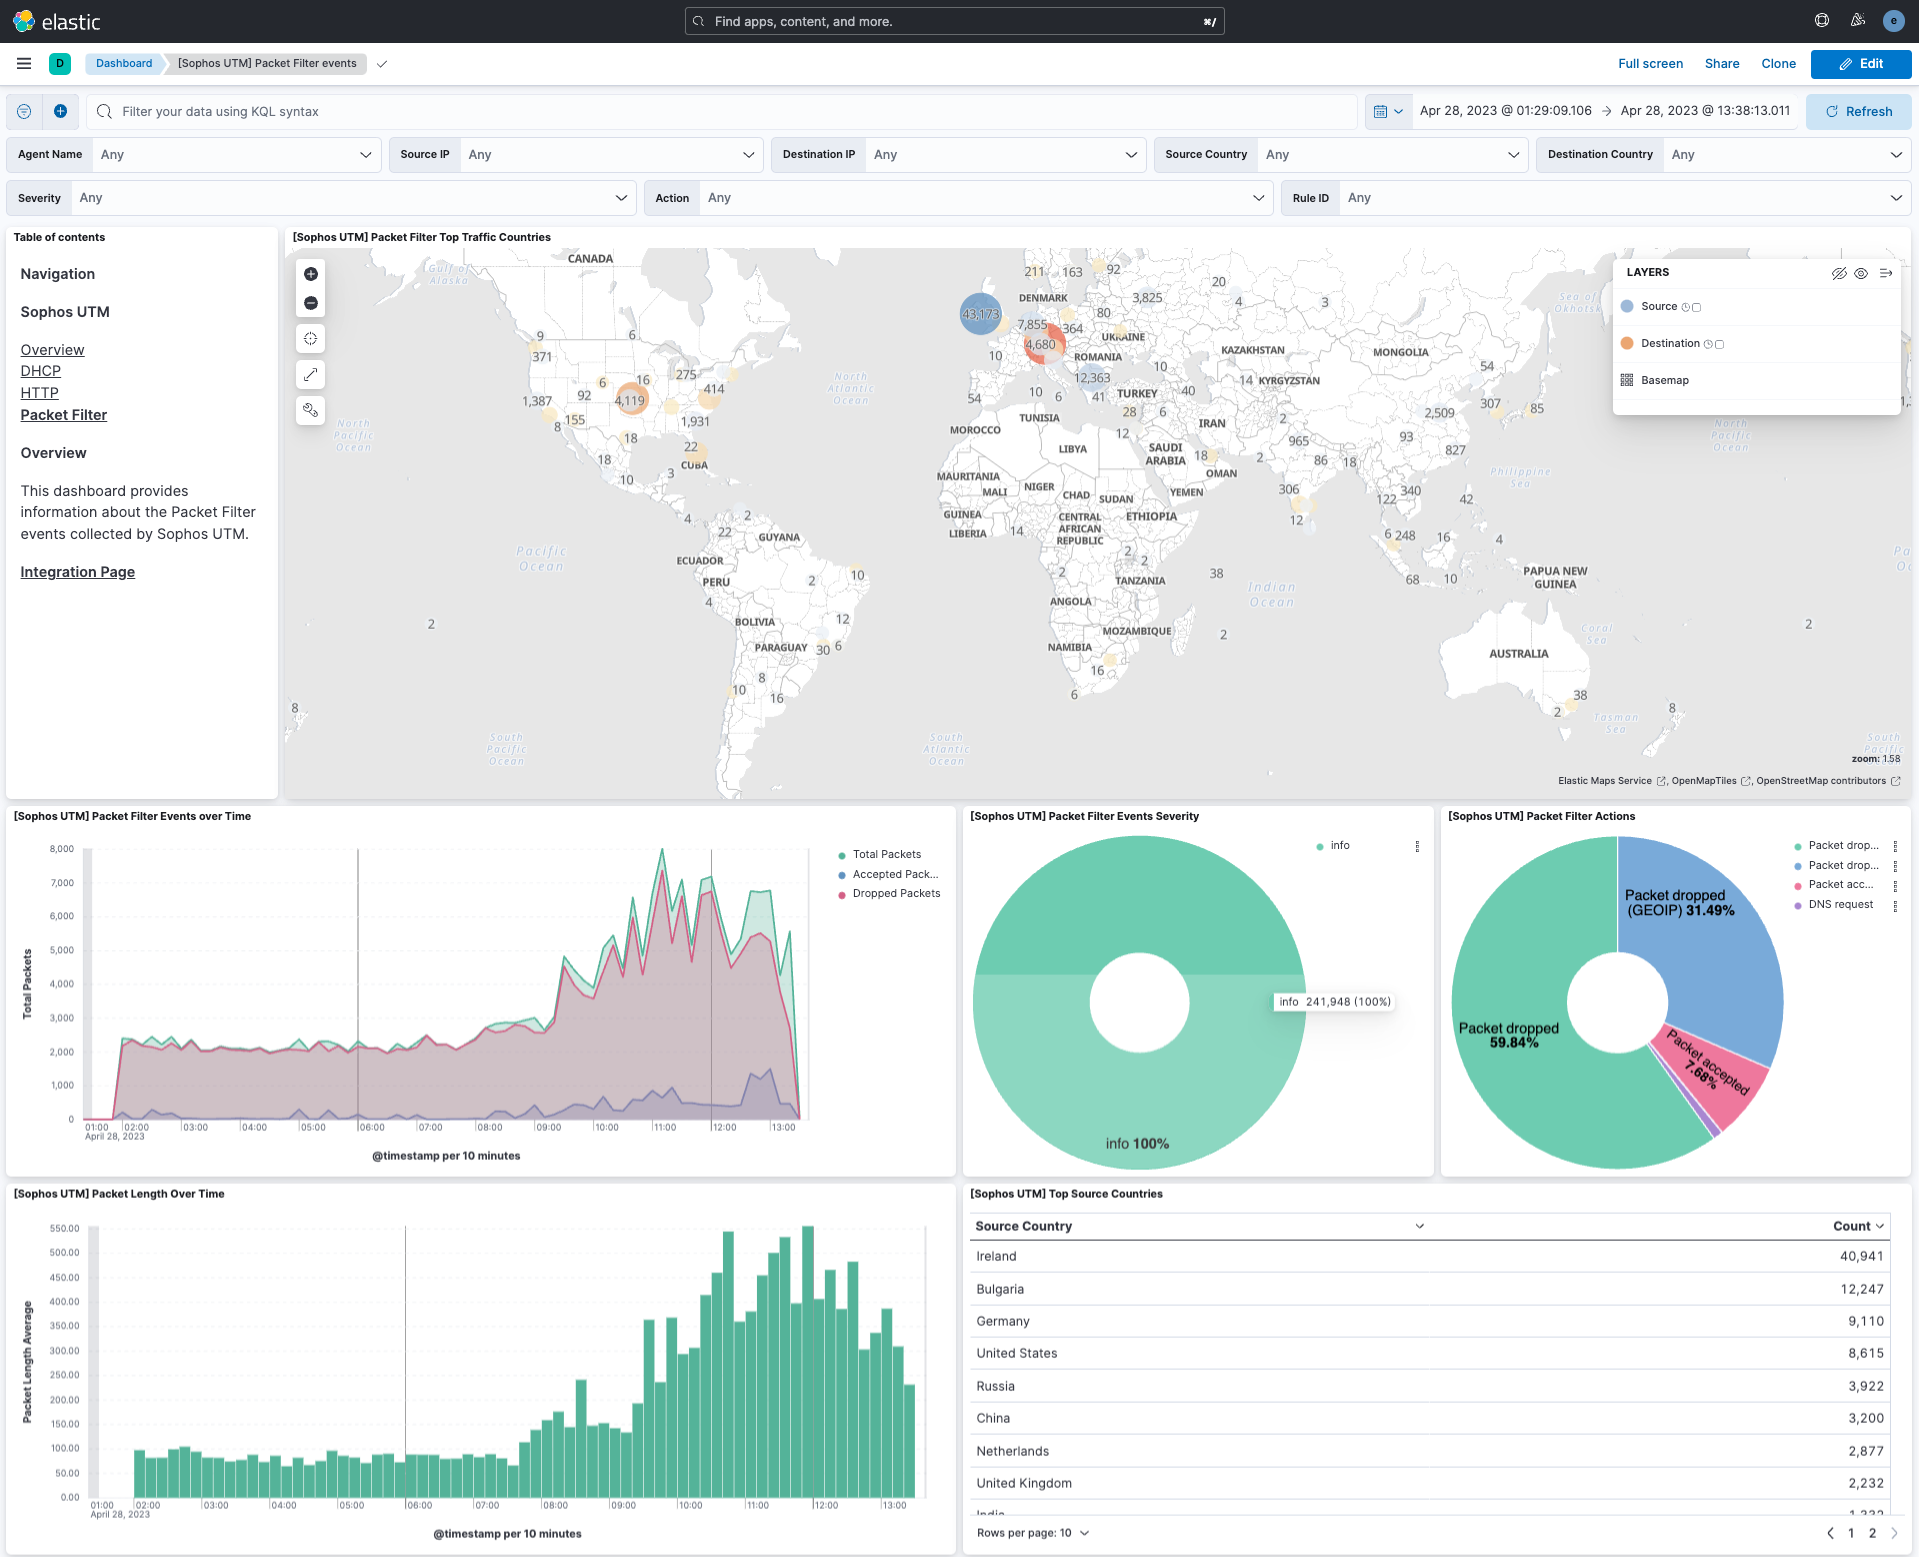
Changelog
| Version | Details | Minimum Kibana version |
|---|---|---|
| 3.17.2 | Bug fix (View pull request) Fix uri_parts processor failure on malformed URLs in XG content filtering logs. Bug fix (View pull request) Map XG content-filtering http_referer and http_user_agent fields to ECS. |
9.0.0 8.11.0 |
| 3.17.1 | Bug fix (View pull request) Remove top level note from docs |
9.0.0 8.11.0 |
| 3.17.0 | Enhancement (View pull request) Update the documenttation. |
9.0.0 8.11.0 |
| 3.16.0 | Enhancement (View pull request) Preserve event.original on pipeline error. |
9.0.0 8.11.0 |
| 3.15.4 | Enhancement (View pull request) Generate processor tags and normalize error handler. |
9.0.0 8.11.0 |
| 3.15.3 | Bug fix (View pull request) Fix add_locale time zone handling |
9.0.0 8.11.0 |
| 3.15.2 | Bug fix (View pull request) Add conditions to GeoIP processors to prevent failure on empty strings |
9.0.0 8.11.0 |
| 3.15.1 | Enhancement (View pull request) Changed owners. |
9.0.0 8.11.0 |
| 3.15.0 | Enhancement (View pull request) Standardize user fields processing across integrations. |
9.0.0 8.11.0 |
| 3.14.0 | Enhancement (View pull request) Allow @custom pipeline access to event.original without setting preserve_original_event. |
9.0.0 8.11.0 |
| 3.13.0 | Enhancement (View pull request) Support stack version 9.0. |
9.0.0 8.6.1 |
| 3.12.1 | Bug fix (View pull request) Updated SSL description to be uniform and to include links to documentation. |
8.6.1 |
| 3.12.0 | Enhancement (View pull request) Allow the usage of deprecated log input and support for stack 9.0 |
8.6.1 |
| 3.11.0 | Enhancement (View pull request) ECS version updated to 8.17.0. |
8.6.1 |
| 3.10.0 | Enhancement (View pull request) Support user-defined timezones |
8.6.1 |
| 3.9.2 | Bug fix (View pull request) Use triple-brace Mustache templating when referencing variables in ingest pipelines. |
8.6.1 |
| 3.9.1 | Bug fix (View pull request) Use triple-brace Mustache templating when referencing variables in ingest pipelines. |
8.6.1 |
| 3.9.0 | Enhancement (View pull request) Update package-spec to 3.0.3. |
8.6.1 |
| 3.8.2 | Enhancement (View pull request) Changed owners |
8.6.1 |
| 3.8.1 | Bug fix (View pull request) Fix exclude_files pattern. |
8.6.1 |
| 3.8.0 | Enhancement (View pull request) Retain host name in host.name as well as host.hostname in UTM datastream. |
8.6.1 |
| 3.7.0 | Enhancement (View pull request) Use Timezone config value when invalid IANA timezone present in events. |
8.6.1 |
| 3.6.1 | Bug fix (View pull request) Fix the parse of syslog priority for Sophos UTM events. |
8.6.1 |
| 3.6.0 | Enhancement (View pull request) ECS version updated to 8.11.0. |
8.6.1 |
| 3.5.0 | Enhancement (View pull request) Improve 'event.original' check to avoid errors if set. |
8.6.1 |
| 3.4.0 | Enhancement (View pull request) ECS version updated to 8.10.0. |
8.6.1 |
| 3.3.0 | Enhancement (View pull request) The format_version in the package manifest changed from 2.11.0 to 3.0.0. Removed dotted YAML keys from package manifest. Added 'owner.type: elastic' to package manifest. |
8.6.1 |
| 3.2.0 | Enhancement (View pull request) Add tags.yml file so that integration's dashboards and saved searches are tagged with "Security Solution" and displayed in the Security Solution UI. |
8.6.1 |
| 3.1.0 | Enhancement (View pull request) Update package to ECS 8.9.0. |
8.6.1 |
| 3.0.0 | Enhancement (View pull request) Add support to UTM Packetfilter logs. Enhancement (View pull request) Add support to UTM HTTP logs. Enhancement (View pull request) Add support to UTM DHCP logs. Enhancement (View pull request) Add support to UTM DNS logs. Enhancement (View pull request) Deprecate JavaScript processing in favor of ingest pipelines for UTM logs. |
8.6.1 |
| 2.11.1 | Bug fix (View pull request) Fix indentation in log agent config. |
8.0.0 7.17.0 |
| 2.11.0 | Enhancement (View pull request) Allow user configuration of timezone offset in XG data stream. Bug fix (View pull request) Fix handling of sophos.xg.eventtime when it contains an invalid timezone. |
8.0.0 7.17.0 |
| 2.10.0 | Enhancement (View pull request) Ensure event.kind is correctly set for pipeline errors. |
8.0.0 7.17.0 |
| 2.9.0 | Enhancement (View pull request) Update package to ECS 8.8.0. |
8.0.0 7.17.0 |
| 2.8.0 | Enhancement (View pull request) Update package to ECS 8.7.0. |
8.0.0 7.17.0 |
| 2.7.1 | Enhancement (View pull request) Added categories and/or subcategories. |
8.0.0 7.17.0 |
| 2.7.0 | Enhancement (View pull request) Update package to ECS 8.6.0. |
8.0.0 7.17.0 |
| 2.6.0 | Enhancement (View pull request) Add udp_options to the UDP input. |
8.0.0 7.17.0 |
| 2.5.1 | Bug fix (View pull request) Remove duplicate fields. |
8.0.0 7.17.0 |
| 2.5.0 | Enhancement (View pull request) Update package to ECS 8.5.0. |
8.0.0 7.17.0 |
| 2.4.2 | Bug fix (View pull request) Remove duplicate field. |
8.0.0 7.17.0 |
| 2.4.1 | Enhancement (View pull request) Use ECS geo.location definition. |
8.0.0 7.17.0 |
| 2.4.0 | Enhancement (View pull request) Update package to ECS 8.4.0 |
8.0.0 7.17.0 |
| 2.3.2 | Enhancement (View pull request) Improve TCP, SSL config description and example for Sophos XG. |
8.0.0 7.17.0 |
| 2.3.1 | Enhancement (View pull request) Update package name and description to align with standard wording |
8.0.0 7.17.0 |
| 2.3.0 | Enhancement (View pull request) Update package to ECS 8.3.0. |
8.0.0 7.17.0 |
| 2.2.2 | Enhancement (View pull request) Update Readme to include links to Sophos's documentation. Also used the latest product name for Astaro |
8.0.0 7.17.0 |
| 2.2.1 | Bug fix (View pull request) Format source.mac and destination.mac as per ECS for the UTM data stream. |
8.0.0 7.17.0 |
| 2.2.0 | Enhancement (View pull request) Improve inputs for Sophos XG pipeline. |
— |
| 2.1.0 | Enhancement (View pull request) Update to ECS 8.2.0 to use new email field set. |
8.0.0 7.17.0 |
| 2.0.0 | Bug fix (View pull request) Remove space from sophos.xg.trans_src_ip field. Bug fix (View pull request) Do not modify event.original. Enhancement (View pull request) Populate url.* fields based on sophos.xg.url.Enhancement (View pull request) Rename sophos.xg.reason to event.reason (ECS).Bug fix (View pull request) Lowercase network.transport as per ECS.Bug fix (View pull request) Format source.mac and destination.mac as per ECS.Enhancement (View pull request) Set the event.code from the message ID (and remove sophos.xg.message_id).Enhancement (View pull request) Add network.community_id.Breaking change (View pull request) Reduce event size by removing client and server fields that are clones of source and destination, respectively. |
— |
| 1.2.3 | Enhancement (View pull request) Update pipelines to parse new fields |
— |
| 1.2.2 | Enhancement (View pull request) Add documentation for multi-fields |
8.0.0 7.14.1 |
| 1.2.1 | Bug fix (View pull request) Add missing ingest pipeline for "System Health" logs |
8.0.0 7.14.1 |
| 1.2.0 | Enhancement (View pull request) Update to ECS 8.0.0 |
8.0.0 7.14.1 |
| 1.1.3 | Bug fix (View pull request) Fix KV splitting and syslog header handling |
8.0.0 7.14.1 |
| 1.1.2 | Bug fix (View pull request) Regenerate test files using the new GeoIP database |
— |
| 1.1.1 | Bug fix (View pull request) Change test public IPs to the supported subset |
— |
| 1.1.0 | Enhancement (View pull request) Add 8.0.0 version constraint |
8.0.0 7.14.1 |
| 1.0.6 | Enhancement (View pull request) Uniform with guidelines |
7.14.1 |
| 1.0.5 | Enhancement (View pull request) Support hostname in syslog header in UTM data stream. |
— |
| 1.0.4 | Enhancement (View pull request) Update Title and Description. |
— |
| 1.0.3 | Bug fix (View pull request) Fixed a bug that prevents the package from working in 7.16. |
— |
| 1.0.2 | Bug fix (View pull request) Fix logic that adds known devices to policy |
— |
| 1.0.1 | Bug fix (View pull request) Fix logic that checks for the 'forwarded' tag |
— |
| 1.0.0 | Enhancement (View pull request) make GA |
— |
| 0.6.0 | Enhancement (View pull request) Update to ECS 1.12.0 |
— |
| 0.5.4 | Bug fix (View pull request) Requires version 7.14.1 of the stack |
— |
| 0.5.3 | Enhancement (View pull request) Convert to generated ECS fields |
— |
| 0.5.2 | Enhancement (View pull request) update to ECS 1.11.0 |
— |
| 0.5.1 | Enhancement (View pull request) Escape special characters in docs |
— |
| 0.5.0 | Enhancement (View pull request) Update integration description |
— |
| 0.4.0 | Enhancement (View pull request) Set "event.module" and "event.dataset" |
— |
| 0.3.0 | Enhancement (View pull request) update to ECS 1.10.0 and adding event.original options |
— |
| 0.2.1 | Enhancement (View pull request) update to ECS 1.9.0 |
— |
| 0.2.0 | Enhancement (View pull request) Add XG data stream |
— |
| 0.1.0 | Enhancement (View pull request) initial release |
— |