Kibana privileges
The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes.
Stack
Generally available
Kibana privileges grant users access to features within Kibana. Roles have privileges to determine whether users have write or read access.
To learn how to assign privileges to a role, refer to Defining roles.
Assigning a base privilege applies the same access level across all feature groups instead of setting a level for each feature.
Some features and sub-feature privileges are excluded from base privileges and must be granted individually.
- All: Grants full read-write access.
- Read: Grants read-only access.
- Customize: Allows you to set the access level for each feature separately.
From the role management screen:
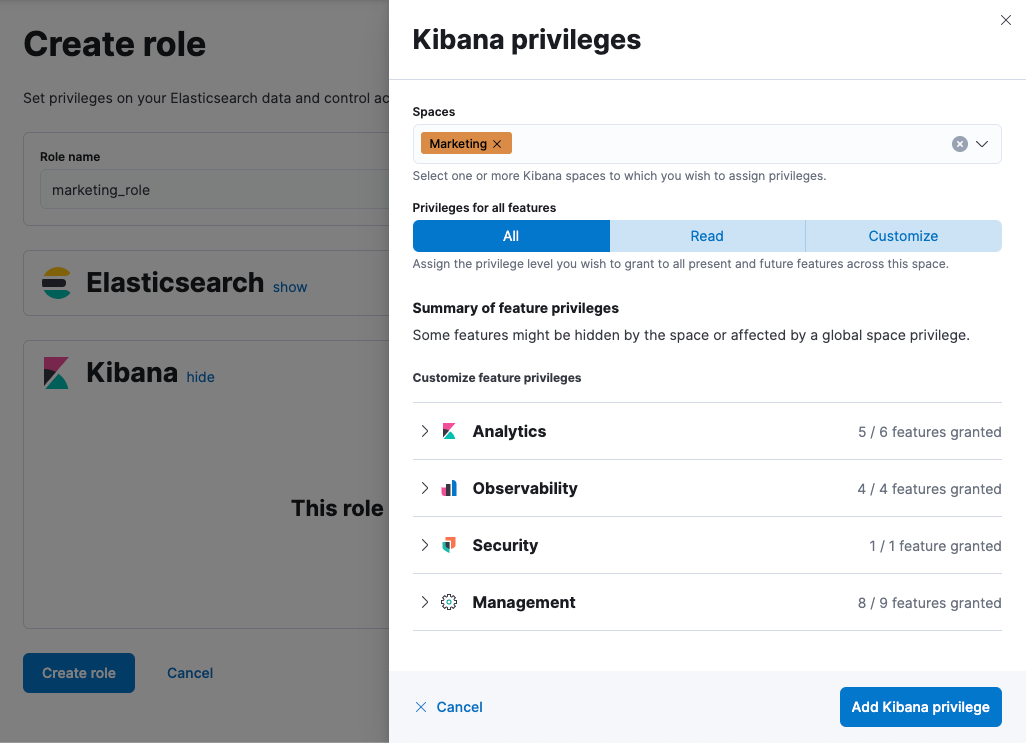
Using the role APIs:
PUT /api/security/role/my_kibana_role
{
  "elasticsearch": {
    "cluster" : [ ],
    "indices" : [ ]
  },
  "kibana": [
    {
      "base": ["all"],
      "feature": {},
      "spaces": ["marketing"]
    }
  ]
}
Assigning a feature privilege grants access to a specific feature. For each feature, select the type of access you want to allow:
- All: Users have full access to the feature, which includes performing all available actions and managing configuration.
- Read: Users can view the feature, but can't perform any actions or manage configuration.
- None: Users can't access or view the feature.
Some features don't have a Read privilege.
In role management, features are organized into the following groups.
| Group | What it contains |
|---|---|
| Analytics | Privileges for the features you use to explore and visualize data. Refer to Privileges in the Analytics group. |
| Universal Alerting Elastic Cloud Serverless projects are autoscaled environments, fully managed by Elastic and available on Elastic Cloud. Availability Generally available This functionality is generally available and ready for production usage. Serverless interfaces and procedures might differ from classic Elastic Stack deployments. The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Planned We plan to add this functionality in a future Elastic Stack update. Subject to changes. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | Privileges for Kibana Universal Alerting. Refer to Configure access to Kibana Universal Alerting. |
| Elasticsearch | Privileges for Elasticsearch features. |
| Observability | Privileges for Elastic Observability features. Refer to Observability Kibana privileges. |
| Security | Privileges for Elastic Security features. Refer to Security Kibana privileges. |
| Management | Privileges for the features you use to administer Kibana and your data. Refer to Privileges in the Management group. |
Some features allow for finer access control than the All and Read privileges. This additional level of control is a subscription feature.
From the role management screen:
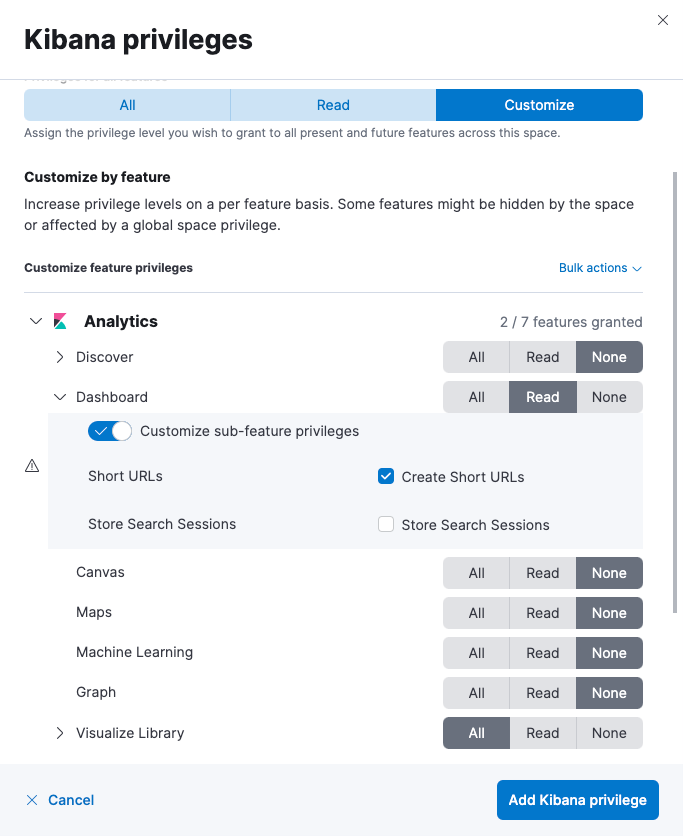
Using the role APIs:
PUT /api/security/role/my_kibana_role
{
  "elasticsearch": {
    "cluster" : [ ],
    "indices" : [ ]
  },
  "kibana": [
    {
      "base": [],
      "feature": {
        "visualize_v2": ["all"],
        "dashboard_v2": ["read", "url_create"]
      },
      "spaces": ["marketing"]
    }
  ]
}
Each of the following privileges controls access to a different feature.
| Privilege | What it allows |
|---|---|
| Discover | Access Discover, and save and manage Discover sessions. Turn on Customize sub-feature privileges to grant individual Discover privileges. For the full list, refer to Discover sub-feature privileges. |
| Dashboard | Access dashboards, and create and edit them. To add new visualizations or maps to a dashboard, users also need the Visualize library or Maps privilege. Turn on Customize sub-feature privileges to grant individual dashboard privileges. For the full list, refer to Dashboard sub-feature privileges. |
| Canvas | Access Canvas, and create and edit workpads. Turn on Customize sub-feature privileges to grant the reporting privilege. For details, refer to Canvas sub-feature privileges. |
| Maps | Access Maps, create and edit maps, and add maps to dashboards. |
| Machine Learning | Access machine learning, and create and manage jobs and trained models. This privilege grants the same access level to data views, dashboards, Discover sessions, and visualizations. |
| Graph | Access Graph, and create and edit graphs. |
| Visualize library | Access the Visualize library, create and edit visualizations, and add visualizations to dashboards. Turn on Customize sub-feature privileges to grant individual Visualize library privileges. For the full list, refer to Visualize library sub-feature privileges. |
| Agent Builder The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.2 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | Access Elastic Agent Builder, including agents, tools, and conversations. The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.4 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. Turn on Customize sub-feature privileges to grant individual Elastic Agent Builder privileges. For the full list, refer to Elastic Agent Builder permissions. |
| Context Engine The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Planned We plan to add this functionality in a future Elastic Stack update. Subject to changes. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. Elastic Cloud Serverless projects are autoscaled environments, fully managed by Elastic and available on Elastic Cloud. Availability Experimental This functionality is experimental and is not ready for production usage. Experimental features may change or be removed at any time. Elastic will work to fix any issues, but experimental features are not subject to the support SLA of official GA features. Specific Support terms apply. Serverless interfaces and procedures might differ from classic Elastic Stack deployments. | Access Context Engine. Read allows viewing AI indices and retrieving context. All also allows creating, editing, and deleting AI indices. Users need separate Elasticsearch index privileges to access backing indices and source data. |
| Agent Builder - Semantic Metadata Layer (SML) The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.5 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | Access the semantic metadata that Elastic Agent Builder uses to interpret your data. The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available in 9.5 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. This privilege is called Agent Context Layer. |
| Workflows The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.3 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | Access Workflows, and create, edit, and run workflows. Turn on Customize sub-feature privileges to grant individual workflow privileges. For the full list, refer to Workflows sub-feature privileges. |
| Proposed Actions The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Planned We plan to add this functionality in a future Elastic Stack update. Subject to changes. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. Elastic Cloud Serverless projects are autoscaled environments, fully managed by Elastic and available on Elastic Cloud. Availability Preview This functionality is in technical preview and is ready for evaluation. Use with caution in production; it is not recommended for mission-critical workloads. Elastic will work to fix any issues, but features in technical preview are not subject to the support SLA of official GA features. Specific Support terms apply. Serverless interfaces and procedures might differ from classic Elastic Stack deployments. | View proposed actions, which are recommendations an agent makes for a user to decide on. All also allows users to approve or decline them. |
| Agentic Investigations The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Planned We plan to add this functionality in a future Elastic Stack update. Subject to changes. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. Elastic Cloud Serverless projects are autoscaled environments, fully managed by Elastic and available on Elastic Cloud. Availability Preview This functionality is in technical preview and is ready for evaluation. Use with caution in production; it is not recommended for mission-critical workloads. Elastic will work to fix any issues, but features in technical preview are not subject to the support SLA of official GA features. Specific Support terms apply. Serverless interfaces and procedures might differ from classic Elastic Stack deployments. | View investigations and escalations. Turn on Customize sub-feature privileges to grant individual investigation and escalation privileges. For the full list, refer to Agentic Investigations sub-feature privileges. |
These privileges control specific actions in Discover. Selecting All includes everything in the following table.
| Privilege | What it allows |
|---|---|
| Create Short URLs | Create short URLs for Discover sessions, so that they can be shared. |
| Store Background search | Save the results of a long-running search, so that they can be viewed again without rerunning the search. The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available from 9.0 to 9.1 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. This privilege is called Store Search Sessions. |
| Generate CSV reports | Export the results of a Discover session as a CSV file. |
These privileges control specific actions on dashboards. Selecting All includes everything in the following table.
| Privilege | What it allows |
|---|---|
| Create Short URLs | Create short URLs for dashboards, so that they can be shared. |
| Store Background search | Save the results of a long-running search, so that they can be viewed again without rerunning the search. The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available from 9.0 to 9.1 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. This privilege is called Store Search Sessions. |
| Generate PDF or PNG reports | Export a dashboard as a PDF or PNG file. |
| Generate CSV reports from Discover session panels | Export the data behind a Discover session panel as a CSV file. |
This privilege controls a specific action in Canvas. Selecting All includes everything in the following table.
| Privilege | What it allows |
|---|---|
| Generate PDF reports | Export a workpad as a PDF file. |
These privileges control specific actions in the Visualize library. Selecting All includes everything in the following table.
| Privilege | What it allows |
|---|---|
| Create Short URLs | Create short URLs for visualizations, so that they can be shared. |
| Generate PDF or PNG reports | Export a visualization as a PDF or PNG file. |
The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes.
Stack
9.3+
Generally available since 9.3
These privileges control specific actions on workflows. Selecting All includes every privilege in the following table except Update managed workflows, which you grant separately.
| Privilege | What it allows |
|---|---|
| Create | Create workflows. |
| Update | Edit existing workflows. |
| Delete | Delete workflows. |
| Execute | Run workflows. |
| Read | View workflows. |
| Read Workflow Execution | View the results of a workflow run, including its logs. |
| Cancel Workflow Execution | Stop a workflow that's currently running. |
| Read managed workflows The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.5 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | View the workflows that Elastic provides. |
| Read managed workflow execution The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.5 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | View the results of a managed workflow run. |
| Update managed workflows The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.5 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | Edit the workflows that Elastic provides. |
Elastic Cloud Serverless projects are autoscaled environments, fully managed by Elastic and available on Elastic Cloud. Availability This functionality is in technical preview and is ready for evaluation. Use with caution in production; it is not recommended for mission-critical workloads. Elastic will work to fix any issues, but features in technical preview are not subject to the support SLA of official GA features. Specific Support terms apply. Serverless interfaces and procedures might differ from classic Elastic Stack deployments. The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability We plan to add this functionality in a future Elastic Stack update. Subject to changes. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes.
Serverless
Preview
Preview
Stack
Planned
Planned
These privileges control specific actions on investigations and escalations. Selecting All for Agentic Investigations includes Manage investigations, but not Manage escalations. Selecting Read includes only View escalations.
| Privilege | What it allows |
|---|---|
| Manage investigations | Assign investigations and change their status, including closing and reopening them. |
| View escalations | View escalations. |
| Manage escalations | Create escalations, add investigations to them, and change who is assigned to them. To close an escalation, you also need Manage investigations. |
Each of the following privileges controls access to a different feature.
| Privilege | What it allows |
|---|---|
| Streams The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.1 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | Access Streams, and change stream processing, retention, and routing. The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available in 9.1 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. This privilege is in the Observability group. |
| AI Anonymization The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.4 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | Change the anonymization rules that control which field values are masked before they're sent to a large language model. |
| Dev Tools | Access Console, Search Profiler, and Grok Debugger. Users also need the matching Elasticsearch cluster and index privileges for the requests they run. |
| Advanced Settings | Change the settings that control how Kibana behaves in a space, such as the default index pattern and date format. |
| Data View Management | Create and edit data views. |
| Files Management | Manage the files that other features store in Kibana. |
| Shared images | Upload and manage the images that other features reuse, such as dashboard panel images. |
| Saved Objects Management | Manage saved objects, including importing, exporting, and copying them between spaces. |
| Saved Query Management | Save and manage queries across all features that use them. |
| Tag Management | Create and edit tags, and apply them to saved objects. |
| Stack Rules | Create and manage Elastic Stack rules, such as index threshold and Elasticsearch query rules. |
| Stack Alerts The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.5 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | View and manage the alerts that Elastic Stack rules generate, without granting access to the rules themselves. |
| Osquery | Access Osquery, and run and save queries. Turn on Customize sub-feature privileges to grant individual Osquery privileges. For the full list, refer to Osquery sub-feature privileges. |
| Actions and Connectors | Create and manage connectors, and run the actions that rules and cases trigger. Turn on Customize sub-feature privileges to grant the endpoint security privilege. For details, refer to Actions and Connectors sub-feature privileges. |
| Cases | Access cases, and create and edit them. Turn on Customize sub-feature privileges to grant individual case privileges. For the full list, refer to Customize sub-feature privileges for cases. |
| Inference Endpoints | Create and manage inference endpoints. The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available from 9.0 to 9.3 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. This privilege is in the Elasticsearch group. |
| Cloud Connect The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.3 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | Connect a cluster to Elastic Cloud services. This privilege appears on Elastic Cloud Enterprise and self-managed clusters, but not on Elastic Cloud Hosted. |
| Automatic Import The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.4 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | Access Automatic Import, and create custom integrations from sample data. |
| Data Set Quality | Access the Data Set Quality page. Turn on Customize sub-feature privileges to grant individual data set quality privileges. For the full list, refer to Data Set Quality sub-feature privileges. |
| Fleet | Access Fleet, and manage agents, agent policies, and Fleet settings. Turn on Customize sub-feature privileges to grant individual Fleet privileges. For the full list, refer to Fleet privileges and available actions. |
| Integrations | Browse and install integrations. To install integrations or add them to agent policies, users also need All for Fleet or its Agent policies sub-feature. |
| Maintenance Windows | Create and manage maintenance windows, which suppress rule notifications for a scheduled period. |
| Manage Scheduled Reports The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.1 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | View and manage the scheduled reports of every user in the space. |
| Query activity The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.4 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | Access Query activity, and cancel long-running queries. |
| Rules Settings | Change the settings that apply to all rules in a space. Turn on Customize sub-feature privileges to grant individual rule settings privileges. For the full list, refer to Rules Settings sub-feature privileges. |
| Stack Monitoring | Access Elastic Stack monitoring. This privilege has no access levels to select: to grant access, assign the monitoring_user role. |
| AI Assistant The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Removed in 9.3 This functionality was removed. You can no longer use it if you're running on this version or a later one. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | Change which AI Assistants are available, from the AI Assistant settings in Elastic Stack Management. The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available in 9.2 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. This privilege is called AI Assistant Settings. |
| Setup guides The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Removed in 9.2 This functionality was removed. You can no longer use it if you're running on this version or a later one. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | Access the getting-started page that helps you ingest data and start using Search, Observability, or Security. |
| Entity Manager The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Removed in 9.1 This functionality was removed. You can no longer use it if you're running on this version or a later one. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | Access the Elastic Entity Model of hosts, containers, and services in Observability. |
These privileges control specific parts of Osquery. Selecting All includes everything in the following table.
| Privilege | What it allows |
|---|---|
| Live queries | Run live queries against hosts, and view the results. Read allows viewing the results of queries that other users ran. Select Run Saved queries within this privilege to also allow running saved queries without being able to change them. |
| Saved queries | Create, edit, and delete saved queries. |
| Packs | Create, edit, and delete query packs, and schedule them to run against agent policies. |
This privilege controls a specific action on connectors. Selecting All includes everything in the following table.
| Privilege | What it allows |
|---|---|
| Execute | Run the endpoint security connectors, which include SentinelOne, CrowdStrike, and Microsoft Defender for Endpoint. |
The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes.
Stack
9.1+
Generally available since 9.1
These privileges control specific actions on the Data Set Quality page. Selecting All includes everything in the following table.
| Privilege | What it allows |
|---|---|
| Manage rules | Create and edit the rules that alert on degraded documents. |
| Manage alerts | View and manage the alerts that those rules generate. |
These privileges control the settings that apply to all rules in a space. Selecting All includes everything in the following table.
| Privilege | What it allows |
|---|---|
| Flapping detection | Change the settings that control when an alert is treated as flapping between states. |
| Alert deletion The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.1 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | Change how long alerts are kept before they're deleted, and delete them on demand. |