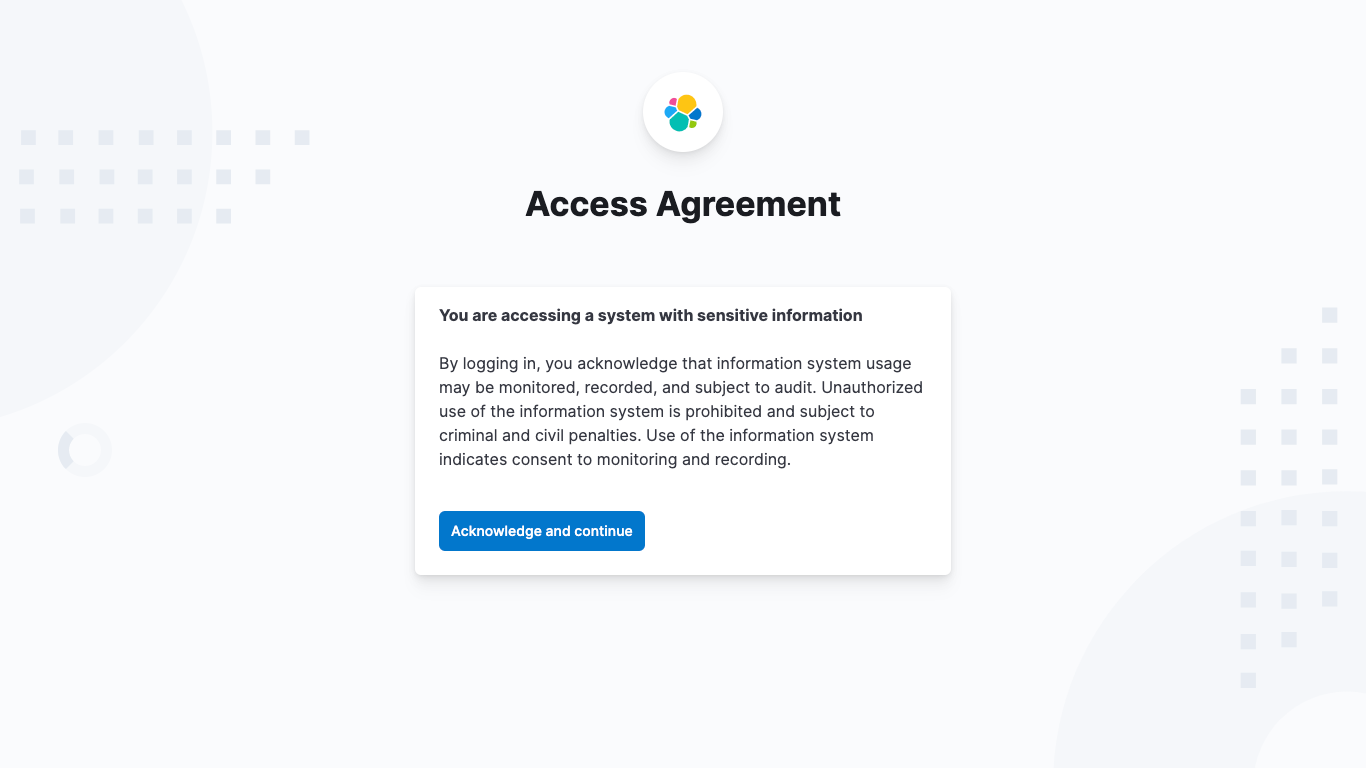
Kibana access agreement
The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes.
Stack
Generally available
Access agreement is a subscription feature that requires users to acknowledge and accept an agreement before accessing Kibana. The agreement text supports Markdown format and can be specified using the xpack.security.authc.providers.<provider-type>.<provider-name>.accessAgreement.message setting.
You can specify a default access agreement using the xpack.security.accessAgreement.message setting. This message will be used for each provider who doesn’t specify an access agreement.
You need to acknowledge the access agreement only once per session, and Kibana reports the acknowledgement in the audit logs.
Here is an example of defining an access agreement in kibana.yml:
xpack.security.authc.providers:
  basic.basic1:
    order: 0
    accessAgreement:
      message: |
        **You are accessing a system with sensitive information**

        By logging in, you acknowledge that information system usage
        ...(shortened)
When you authenticate using basic.basic1, you’ll see the following agreement that you must acknowledge before you can access Kibana: