Hosts page
Elastic Cloud Serverless projects are autoscaled environments, fully managed by Elastic and available on Elastic Cloud. Availability This functionality is generally available and ready for production usage. The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes.
Serverless Security
Generally available
Stack
Generally available
The Hosts page provides a comprehensive overview of all hosts and host-related security events. Key performance indicator (KPI) charts, data tables, and interactive widgets let you view specific data, drill down for deeper insights, and interact with Timeline for further investigation.
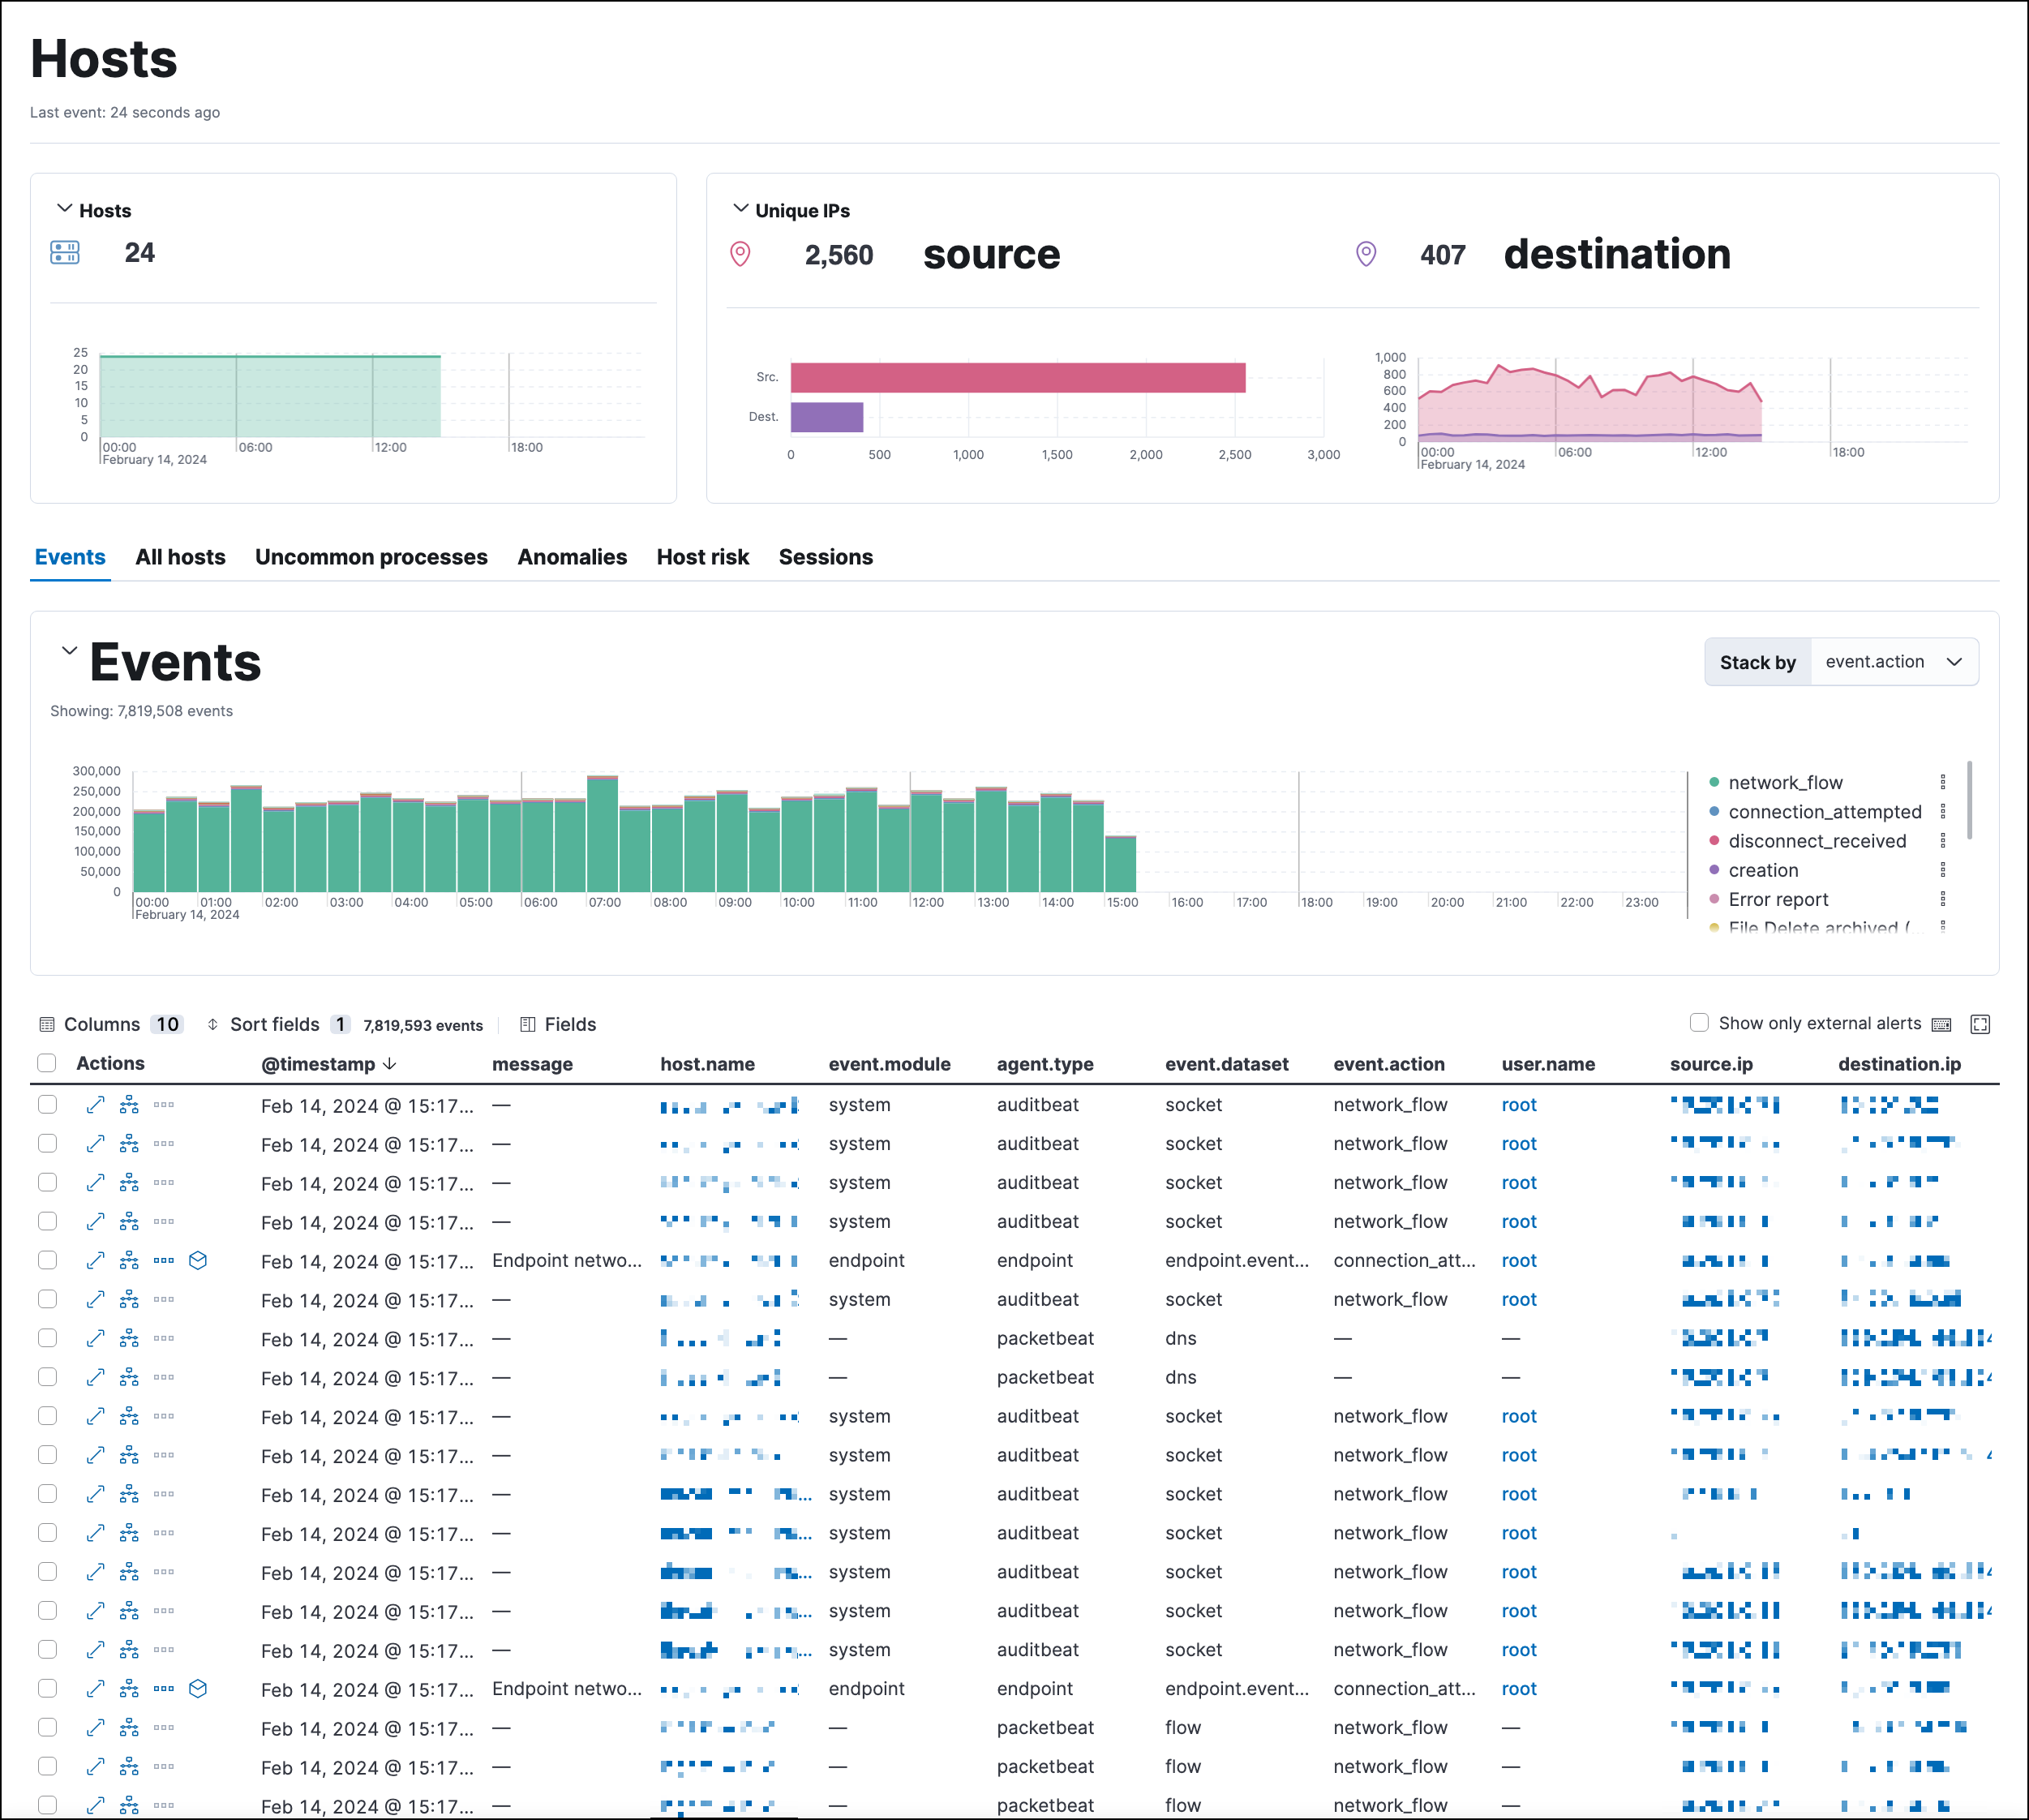
The Hosts page has the following sections:
KPI charts show metrics for hosts and unique IPs within the time range specified in the date picker. This data is visualized using linear or bar graphs.
Hover inside a KPI chart to display the actions menu (…), where you can perform these actions: inspect, open in Lens, and add to a new or existing case.
Beneath the KPI charts are data tables, categorized by individual tabs, which are useful for viewing and investigating specific types of data. Select the relevant tab to view the following data:
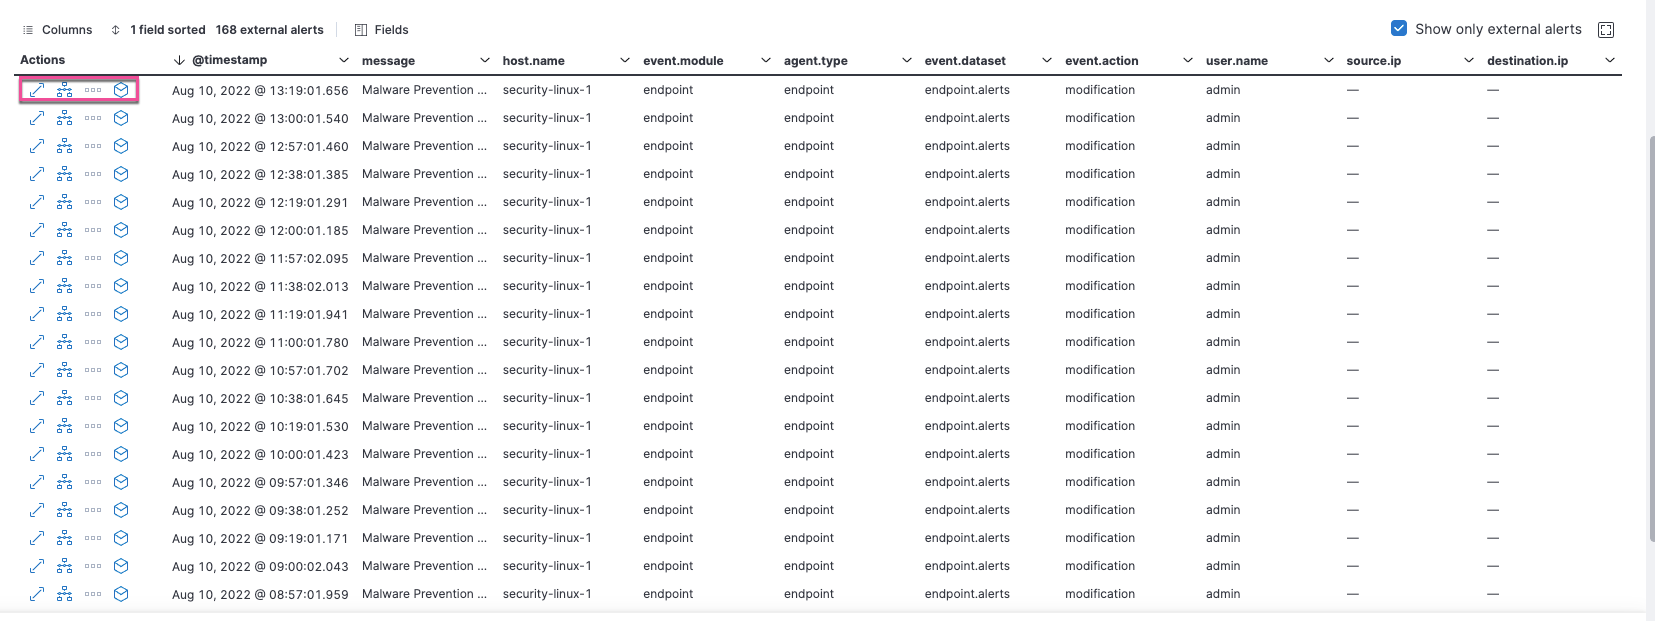
- Events: All host events. To display alerts received from external monitoring tools, scroll down to the Events table and select Show only external alerts on the right.
- All hosts: High-level host details.
- Uncommon processes: Uncommon processes running on hosts.
- Anomalies: Anomalies discovered by machine learning jobs.
- Host risk: The latest recorded host risk score for each host, and its host risk classification. In Elastic Stack, this feature requires a Platinum subscription or higher. In serverless, this feature requires the Security Analytics Complete project feature tier. Click Enable on the Host risk tab to get started. To learn more, refer to our entity risk scoring documentation.
- Sessions: Linux process events that you can open in Session View, an investigation tool that allows you to examine Linux process data at a hierarchal level.
The tables within the Events and Sessions tabs include inline actions and several customization options. To learn more about what you can do with the data in these tables, refer to Manage detection alerts.
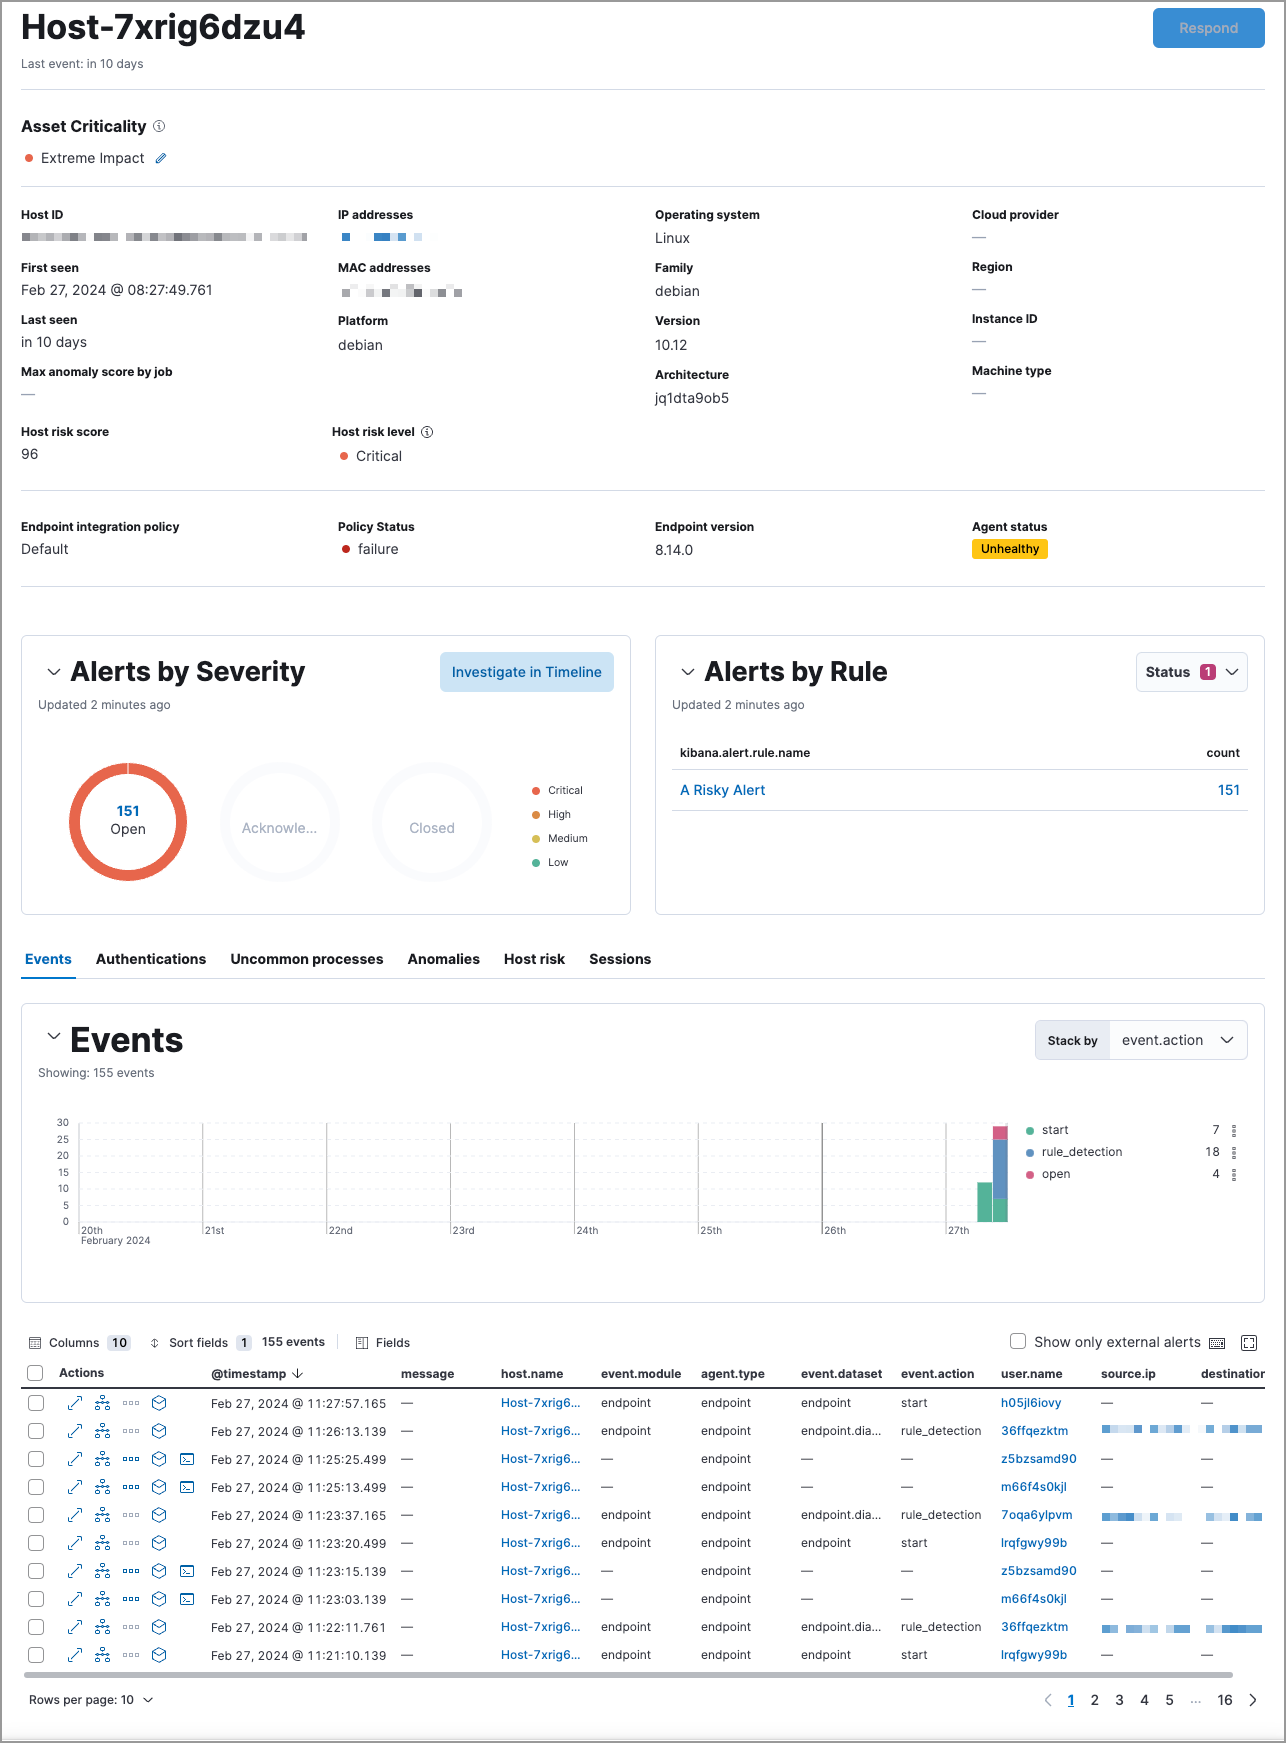
A host’s details page displays all relevant information for the selected host. To view a host’s details page, click its Host name link in the All hosts table.
The host details page includes the following sections:
- Asset Criticality: This section displays the host’s current asset criticality level.
- Summary: Details such as the host ID, when the host was first and last seen, the associated IP addresses, and associated operating system. If the host risk score feature is enabled, this section also displays host risk score data.
- Alert metrics: The total number of alerts by severity, rule, and status (
Open,Acknowledged, orClosed). - Data tables: The same data tables as on the main Hosts page, except with values for the selected host instead of all hosts.