Services
Elastic Cloud Serverless projects are autoscaled environments, fully managed by Elastic and available on Elastic Cloud. Availability This functionality is generally available and ready for production usage. Serverless interfaces and procedures might differ from classic Elastic Stack deployments. The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes.
Serverless
Generally available
Stack
Generally available
The Services inventory provides a quick, high-level overview of the health and general performance of all instrumented services.
A service only appears in the Services inventory if it has sent transactions or spans within the selected time window. Services that send only logs are not listed. If a service is missing, verify that it is sending transaction or span data and that the selected time range includes recent activity.
Active alerts for each service are prominently displayed in the service inventory table. Clicking an active alert badge brings you to the Alerts tab where you can learn more about the active alert and take action.
The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.4 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. Elastic Cloud Serverless projects are autoscaled environments, fully managed by Elastic and available on Elastic Cloud. Availability Generally available This functionality is generally available and ready for production usage. Serverless interfaces and procedures might differ from classic Elastic Stack deployments. SLOs for each service are also shown in the service inventory table. Use the Actions menu on any service row to act on the service directly, or the Environment selector to filter the inventory by environment.
The inventory also uses machine learning to surface potential problems with your services. To see these results, anomaly detection must be enabled:
- The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Planned We plan to add this functionality in a future Elastic Stack update. Subject to changes. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. Elastic Cloud Serverless projects are autoscaled environments, fully managed by Elastic and available on Elastic Cloud. Availability Generally available This functionality is generally available and ready for production usage. Serverless interfaces and procedures might differ from classic Elastic Stack deployments. Low transaction count anomalies also contribute to the service's highest anomaly score, as long as the environment's job includes the low-count detector.
- The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.5 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. Elastic Cloud Serverless projects are autoscaled environments, fully managed by Elastic and available on Elastic Cloud. Availability Generally available This functionality is generally available and ready for production usage. Serverless interfaces and procedures might differ from classic Elastic Stack deployments. The Anomalies column shows each service's highest anomaly score for the selected time range, replacing the previous health status.
- The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available from 9.0 to 9.3 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. Services are sorted by their health status: critical → warning → healthy → unknown.
For Observability Serverless projects, the Editor role or higher is required to create and manage service groups. To learn more, refer to Assign user roles and privileges.
The Service grouping functionality is in beta and is subject to change. The design and code is less mature than official generally available features and is being provided as-is with no warranties.
Group services together to build meaningful views that remove noise, simplify investigations across services, and combine related alerts.
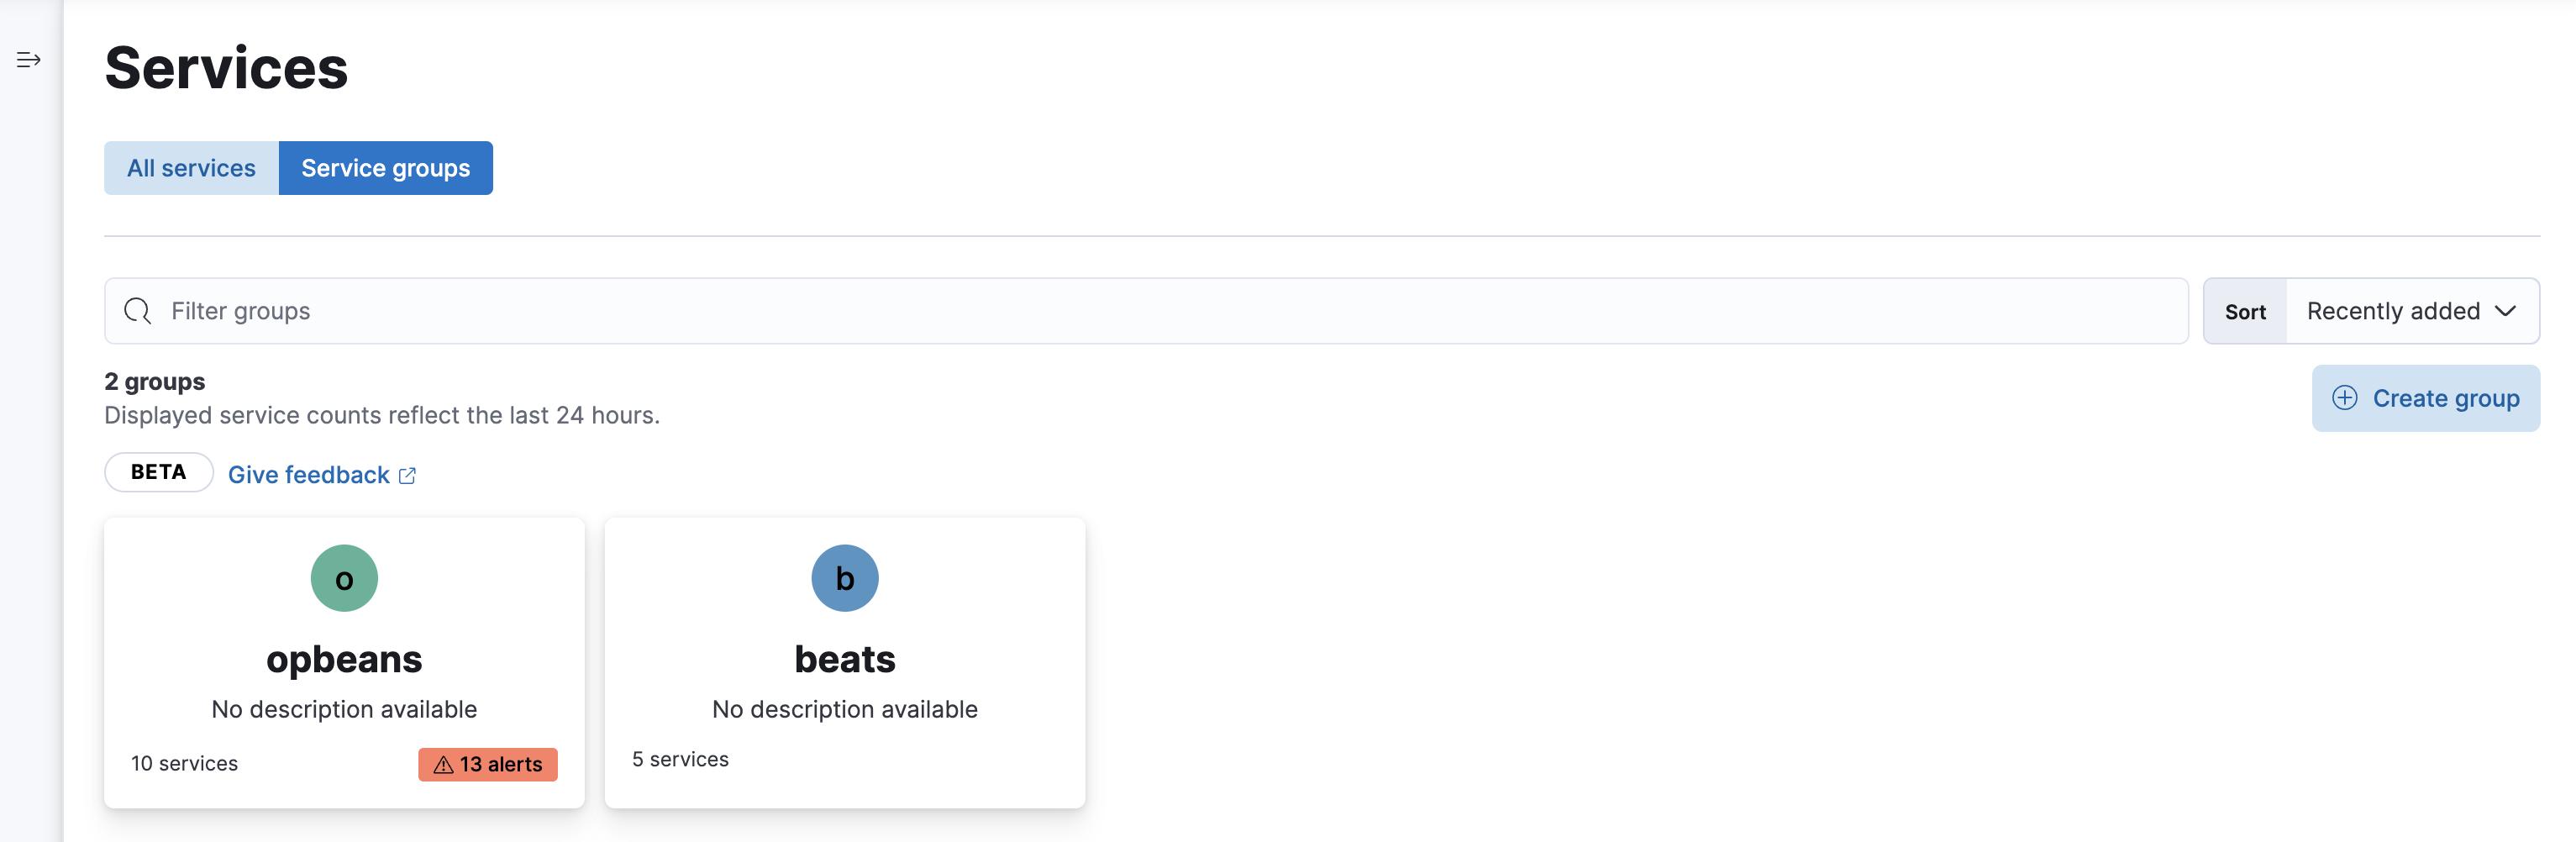
To create a service group:
- To open Service inventory, find Applications in the main menu or use the global search field.
- Switch to Service groups.
- Click Create group.
- Specify a name, color, and description.
- Click Select services.
- Specify a Kibana Query Language (KQL) query to filter services by one or more of the following dimensions:
agent.name,service.name,service.language.name,service.environment,labels.<xyz>. Services that match the query within the last 24 hours will be assigned to the group.
Not sure where to get started? Here are some sample queries you can build from:
- Group services by environment: To group "production" services, use
service.environment : "production". - Group services by name: To group all services that end in "beat", use
service.name : *beat. This will match services named "Auditbeat", "Heartbeat", "Filebeat", and so on.