ES|QL COUNT function
Elastic Cloud Serverless projects are autoscaled environments, fully managed by Elastic and available on Elastic Cloud. Availability This functionality is generally available and ready for production usage. Serverless interfaces and procedures might differ from classic Elastic Stack deployments. The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes.
Serverless
Generally available
Stack
Generally available
Returns the total number of input values.
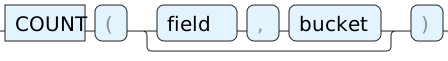
field- Expression that outputs values to be counted. If omitted, equivalent to
COUNT(*)(the number of rows). bucket-
Range of histogram values to count.
Returns the total number (count) of input values.
| field | bucket | result |
|---|---|---|
| aggregate_metric_double | long | |
| boolean | long | |
| cartesian_point | long | |
| cartesian_shape | long | |
| counter_double The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Planned We plan to add this functionality in a future Elastic Stack update. Subject to changes. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | long | |
| counter_integer The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Planned We plan to add this functionality in a future Elastic Stack update. Subject to changes. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | long | |
| counter_long The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Planned We plan to add this functionality in a future Elastic Stack update. Subject to changes. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | long | |
| date | long | |
| date_nanos | long | |
| date_range The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Preview since 9.5 This functionality is in technical preview and is ready for evaluation. Use with caution in production; it is not recommended for mission-critical workloads. Elastic will work to fix any issues, but features in technical preview are not subject to the support SLA of official GA features. Specific Support terms apply. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | long | |
| dense_vector | long | |
| double | long | |
| double_range The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Planned We plan to add this functionality in a future Elastic Stack update. Subject to changes. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | long | |
| exponential_histogram The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.4 This functionality is generally available and ready for production usage. Preview in 9.3 This functionality is in technical preview and is ready for evaluation. Use with caution in production; it is not recommended for mission-critical workloads. Elastic will work to fix any issues, but features in technical preview are not subject to the support SLA of official GA features. Specific Support terms apply. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | long | |
| exponential_histogram The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Planned We plan to add this functionality in a future Elastic Stack update. Subject to changes. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | double_range The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Planned We plan to add this functionality in a future Elastic Stack update. Subject to changes. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | long |
| flattened The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Preview since 9.5 This functionality is in technical preview and is ready for evaluation. Use with caution in production; it is not recommended for mission-critical workloads. Elastic will work to fix any issues, but features in technical preview are not subject to the support SLA of official GA features. Specific Support terms apply. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | long | |
| geo_point | long | |
| geo_shape | long | |
| geohash | long | |
| geohex | long | |
| geotile | long | |
| integer | long | |
| ip | long | |
| keyword | long | |
| long | long | |
| tdigest The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.4 This functionality is generally available and ready for production usage. Preview in 9.3 This functionality is in technical preview and is ready for evaluation. Use with caution in production; it is not recommended for mission-critical workloads. Elastic will work to fix any issues, but features in technical preview are not subject to the support SLA of official GA features. Specific Support terms apply. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | long | |
| tdigest The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Planned We plan to add this functionality in a future Elastic Stack update. Subject to changes. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | double_range The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Planned We plan to add this functionality in a future Elastic Stack update. Subject to changes. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. | long |
| text | long | |
| unsigned_long | long | |
| version | long |
FROM employees
| STATS COUNT(height)
| COUNT(height):long |
|---|
| 100 |
To count the number of rows, use COUNT() or COUNT(*)
FROM employees
| STATS count = COUNT(*) BY languages
| SORT languages DESC
| count:long | languages:integer |
|---|---|
| 10 | null |
| 21 | 5 |
| 18 | 4 |
| 17 | 3 |
| 19 | 2 |
| 15 | 1 |
The expression can use inline functions. This example splits a string into multiple values
using the SPLIT function and counts the values.
ROW words="foo;bar;baz;qux;quux;foo"
| STATS word_count = COUNT(SPLIT(words, ";"))
| word_count:long |
|---|
| 6 |
To count the number of times an expression returns TRUE use a
WHERE command to remove rows that
shouldn’t be included.
ROW n=1
| WHERE n < 0
| STATS COUNT(n)
| COUNT(n):long |
|---|
| 0 |
To count the number of times multiple expressions return TRUE use a WHERE inside the STATS.
FROM employees
| STATS
    gte20 = COUNT(*) WHERE height >= 2,
    lte18 = COUNT(*) WHERE height <= 1.8
| gte20:long | lte18:long |
|---|---|
| 20 | 56 |
COUNTing a multivalued field returns the number of values. COUNTing NULL returns 0.
COUNTing true returns 1. COUNTing false returns 1.
ROW mv = [1, 2], n = NULL, t = TRUE, f = FALSE
| STATS COUNT(mv), COUNT(n), COUNT(t), COUNT(f)
| COUNT(mv):long | COUNT(n):long | COUNT(t):long | COUNT(f):long |
|---|---|---|---|
| 2 | 0 | 1 | 1 |
You may see a pattern like COUNT(<expression> OR NULL). This has the same meaning as
COUNT() WHERE <expression>. This relies on COUNT(NULL) to return 0 and builds on the
three-valued logic (3VL): TRUE OR NULL is TRUE, but
FALSE OR NULL is NULL. Prefer the COUNT() WHERE <expression> pattern.
ROW n=1
| STATS COUNT(n > 0 OR NULL), COUNT(n < 0 OR NULL)
| COUNT(n > 0 OR NULL):long | COUNT(n < 0 OR NULL):long |
|---|---|
| 1 | 0 |
COUNT can also operate on exponential_histogram fields, returning the total number of values which were used to construct the histograms.
TS exp_histo_sample
| WHERE instance == "instance-0"
| STATS cnt = COUNT(responseTime)
| cnt:long |
|---|
| 8841 |
COUNT can also operate on tdigest and casted histogram fields, returning the total number of values which were used to construct the digests.
TS histogram_timeseries_index
| WHERE instance == "instance-0"
| STATS cnt = COUNT(responseTime::tdigest)
| cnt:long |
|---|
| 8841 |
To count only the histogram values that fall into a range, pass a double_range (for example from
TO_RANGE) as the
second argument. Combine this with
BUCKET on the same
histogram field to create a histogram of the recorded values:
TS exp_histo_sample
| WHERE instance == "instance-0"
| STATS count = COUNT(responseTime, bucket) BY bucket = BUCKET(responseTime, 1)
| SORT RANGE_MIN(bucket)
| count:long | bucket:double_range |
|---|---|
| 8723 | 0.0..1.0 |
| 112 | 1.0..2.0 |
| 1 | 2.0..3.0 |
| 2 | 3.0..4.0 |
| 2 | 5.0..6.0 |
| 1 | 6.0..7.0 |
Histograms only record approximate value distributions, so the counts per bucket are estimates.
The same works for tdigest and casted histogram fields:
TS histogram_timeseries_index
| WHERE instance == "instance-0"
| STATS count = COUNT(responseTime::tdigest, bucket) BY bucket = BUCKET(responseTime::tdigest, 1)
| SORT RANGE_MIN(bucket)
| count:long | bucket:double_range |
|---|---|
| 8733 | 0.0..1.0 |
| 100 | 1.0..2.0 |
| 4 | 2.0..3.0 |
| 2 | 3.0..4.0 |
| 0 | 4.0..5.0 |
| 0 | 5.0..6.0 |
| 2 | 6.0..7.0 |
A tdigest does not track which ranges between its centroids are empty, so BUCKET returns every bucket
between the smallest and the largest centroid of a digest, and some of them may end up with a count of 0.