Webhook connector and action
Elastic Cloud Serverless projects are autoscaled environments, fully managed by Elastic and available on Elastic Cloud. Availability This functionality is generally available and ready for production usage. Serverless interfaces and procedures might differ from classic Elastic Stack deployments. The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes.
Serverless
Generally available
Stack
Generally available
The Webhook connector uses axios to send a request to a web service.
You can create connectors in Stack Management > Connectors or as needed when you’re creating a rule. For example:
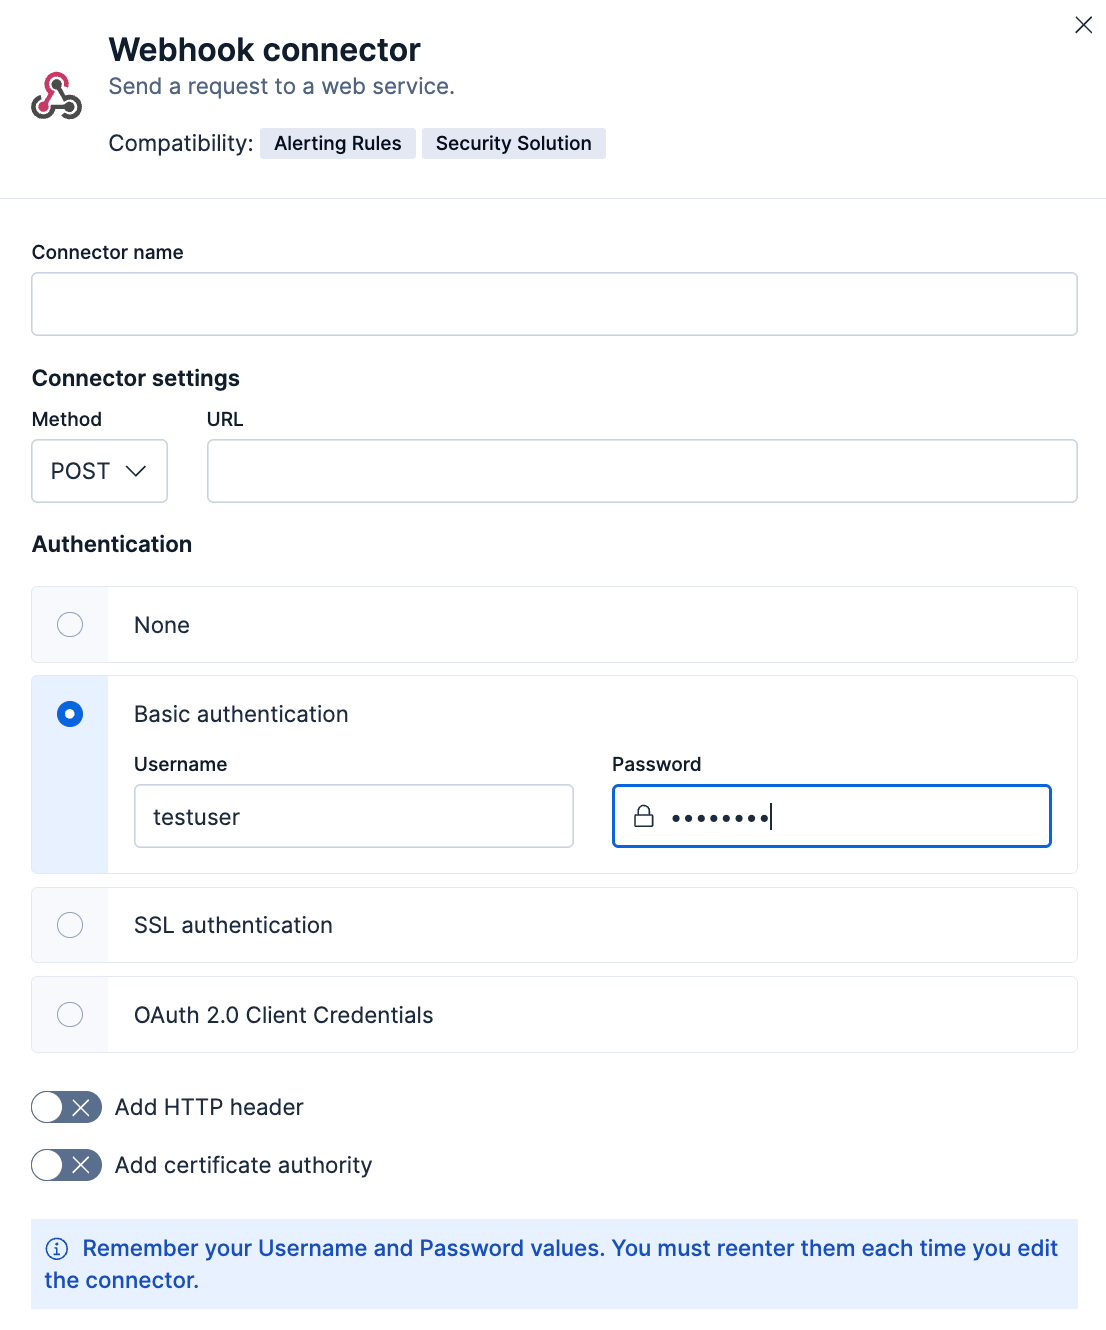
Webhook connectors have the following configuration properties:
- Name
- The name of the connector.
- Method
-
The HTTP method to send a request to a web service:
POST(default)PUT-
The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats.
Availability
Generally available since 9.3
This functionality is generally available and ready for production usage.
Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments.
This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes.
PATCH -
The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats.
Availability
Generally available since 9.3
This functionality is generally available and ready for production usage.
Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments.
This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes.
GET -
The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats.
Availability
Generally available since 9.3
This functionality is generally available and ready for production usage.
Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments.
This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes.
DELETE
- URL
- The request URL must start with
http://orhttps://. Internal hostnames such ashttp://dev-logstash:10200are supported. If you are using thexpack.actions.allowedHostssetting, make sure the hostname is added to the allowed hosts. - Authentication
-
The authentication type: none, basic, SSL, or The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.2 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes. OAuth 2.0 authentication.
- Basic
- If you choose basic authentication, you must provide a user name and password.
- SSL
- If you choose SSL authentication, you must provide SSL server certificate authentication data in a CRT and key file format or a PFX file format. You can also optionally provide a passphrase if the files are password-protected.
- OAuth 2.0 authentication The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.2 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes.
- If you choose OAuth 2.0 authentication, you must provide an access token URL, client ID, and client secret. Specifying the access token scope is optional. You also have the option to specify additional parameters that your authentication provider might require.
- HTTP headers (optional)
-
A custom set of HTTP headers that you can send with API requests.
- Config
- If you choose the config type, values in headers will be sent as plain text in requests.
- Secret The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability Generally available since 9.2 This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes.
- If you choose the secret type, values in your headers will be encrypted in requests.
- Certificate authority (optional)
-
A certificate authority (CA) that the connector can trust, for example to sign and validate server certificates. This option is available for all authentication types.
- CA file
- The certificate authority file.
- Verification mode
-
Controls the certificate verification.
- Use
fullto validate that the certificate has an issue date within thenot_beforeandnot_afterdates, chains to a trusted certificate authority, and has a hostname or IP address that matches the names within the certificate. - Use
certificateto validate the certificate and verifies that it is signed by a trusted authority; this option does not check the certificate hostname. - Use
noneto skip certificate validation.
- Use
You can test connectors as you’re creating or editing the connector in Kibana. For example:
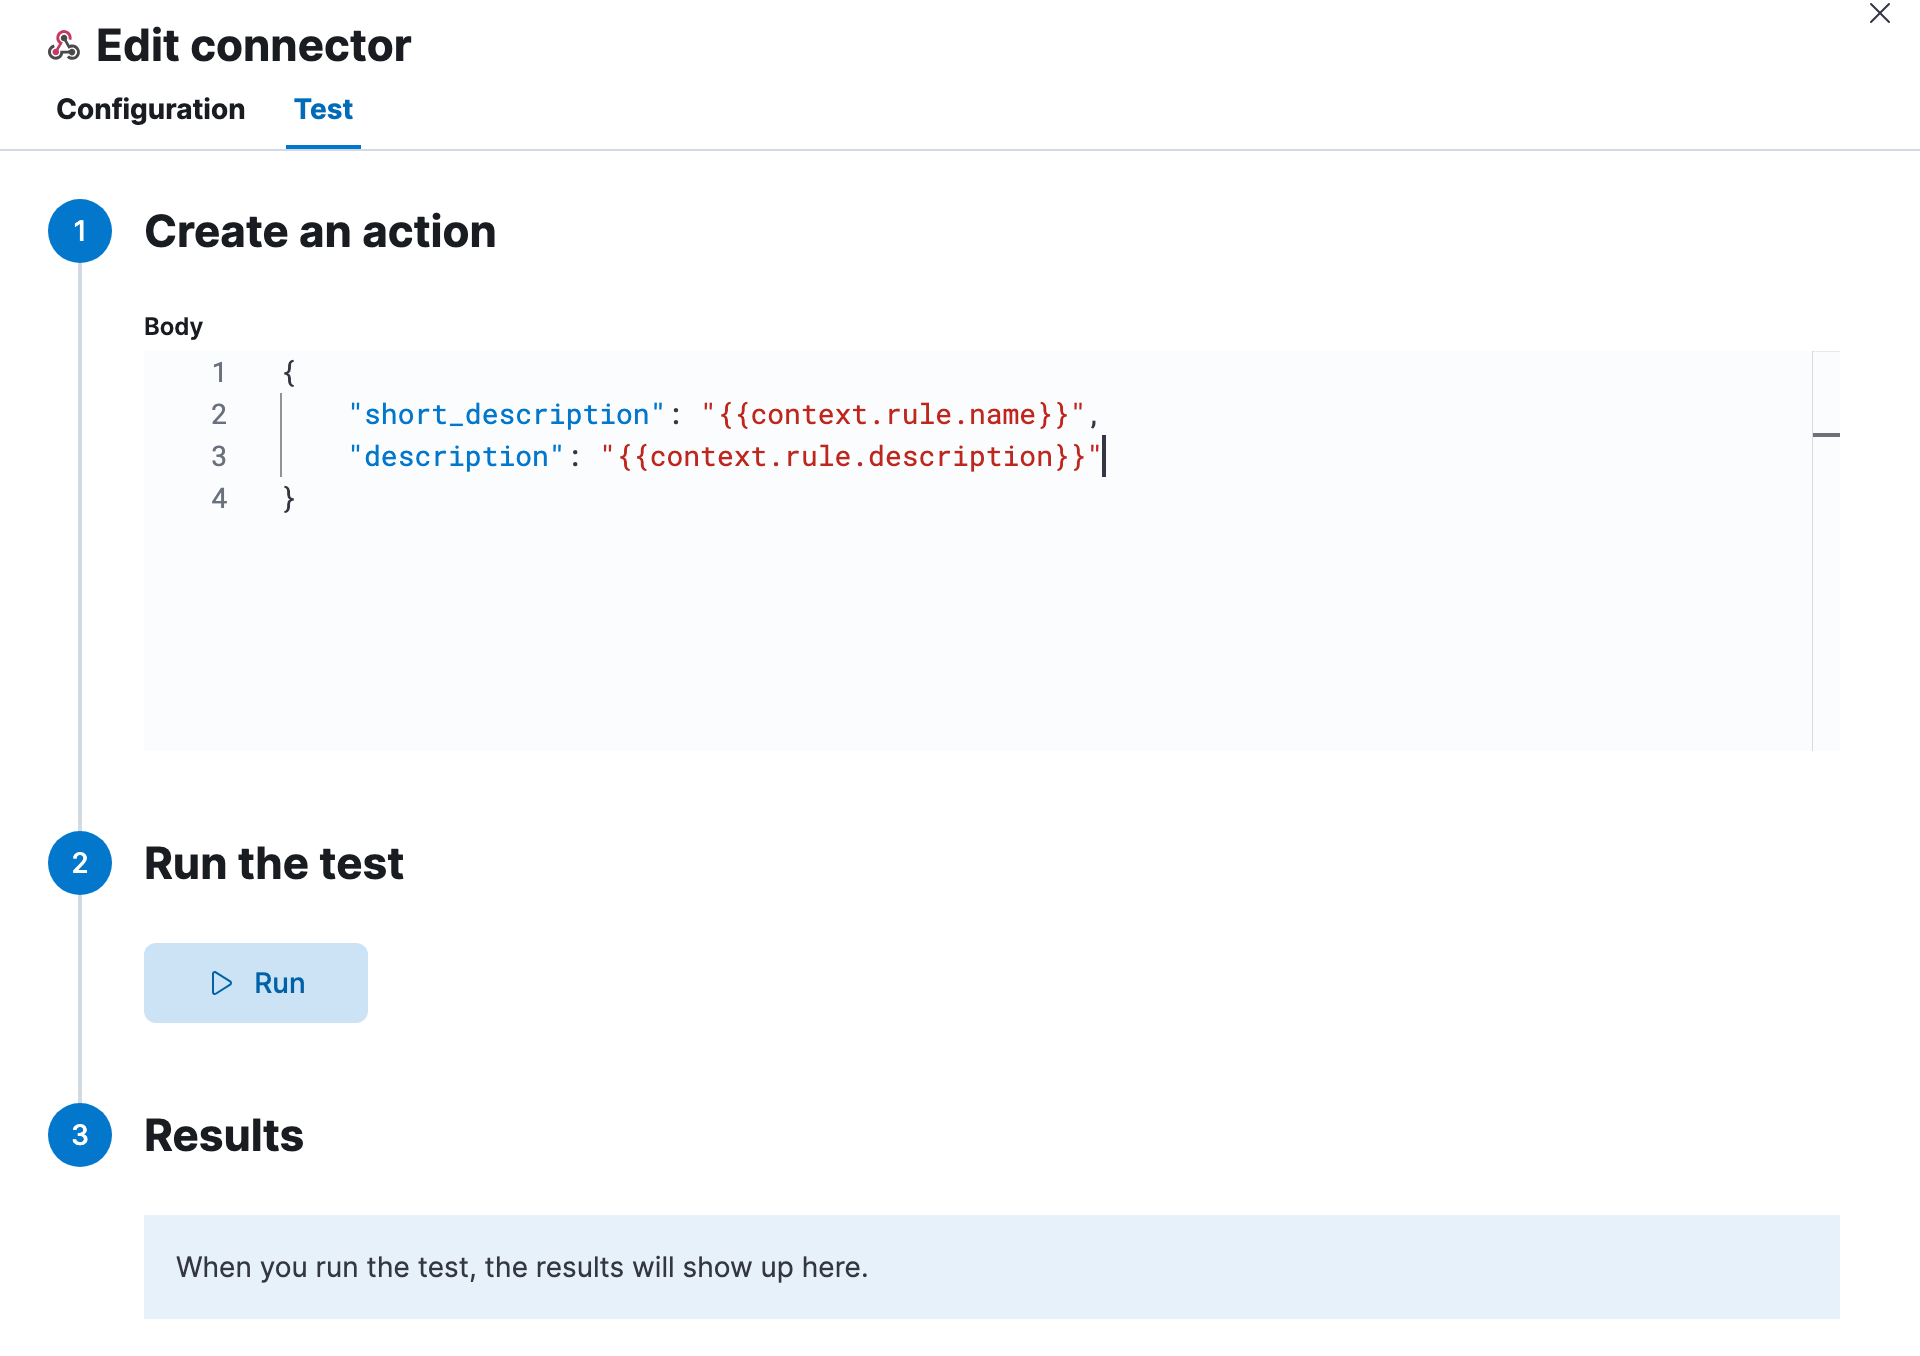
Webhook actions have the following properties.
- Body
-
A JSON payload sent to the request URL using the
POST,PUT, orPATCHHTTP methods. For example:Text { "short_description": "{{context.rule.name}}", "description": "{{context.rule.description}}", ... }
Mustache template variables (the text enclosed in double braces, for example, context.rule.name) have their values escaped, so that the final JSON will be valid (escaping double quote characters). For more information on Mustache template variables, refer to Actions.
Use the Action configuration settings to customize connector networking configurations, such as proxies, certificates, or TLS settings. You can set configurations that apply to all your connectors or use xpack.actions.customHostSettings to set per-host configurations.