Swimlane connector and action
Elastic Cloud Serverless projects are autoscaled environments, fully managed by Elastic and available on Elastic Cloud. Availability This functionality is generally available and ready for production usage. Elastic Cloud Serverless projects are autoscaled environments, fully managed by Elastic and available on Elastic Cloud. Availability This functionality is generally available and ready for production usage. The Elastic Stack includes Elastic's core products such as Elasticsearch, Kibana, Logstash, and Beats. Availability This functionality is generally available and ready for production usage. Unless stated otherwise on the page, this functionality is available when your Elastic Stack is deployed on Elastic Cloud Hosted, Elastic Cloud Enterprise, Elastic Cloud on Kubernetes, and self-managed environments. This documentation corresponds to the latest patch available for each minor version. If you're not using the latest patch, check the release notes for changes.
Serverless Observability
Generally available
Serverless Security
Generally available
Stack
Generally available
The Swimlane connector uses the Swimlane REST API to create Swimlane records.
The Swimlane connector works with the Swimlane API v2. Swimlane Turbine is not supported.
You can create connectors in Stack Management > Connectors or as needed when you're creating a rule. For example:
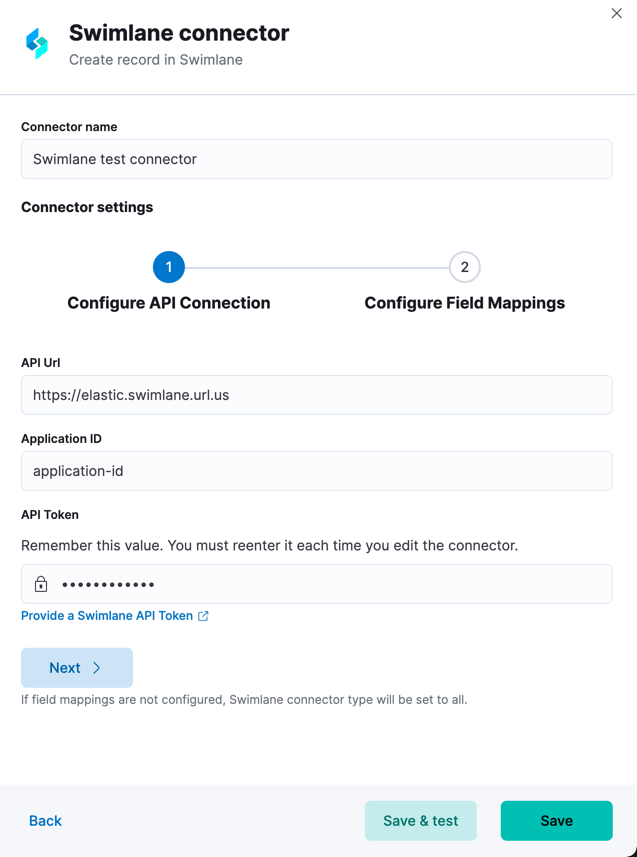
Swimlane connectors have the following configuration properties:
- Name
- The name of the connector.
- URL
- Swimlane instance URL.
- Application ID
- Swimlane application ID.
- API token
- Swimlane API authentication token for HTTP basic authentication.
You can test connectors as you're creating or editing the connector in Kibana. For example:
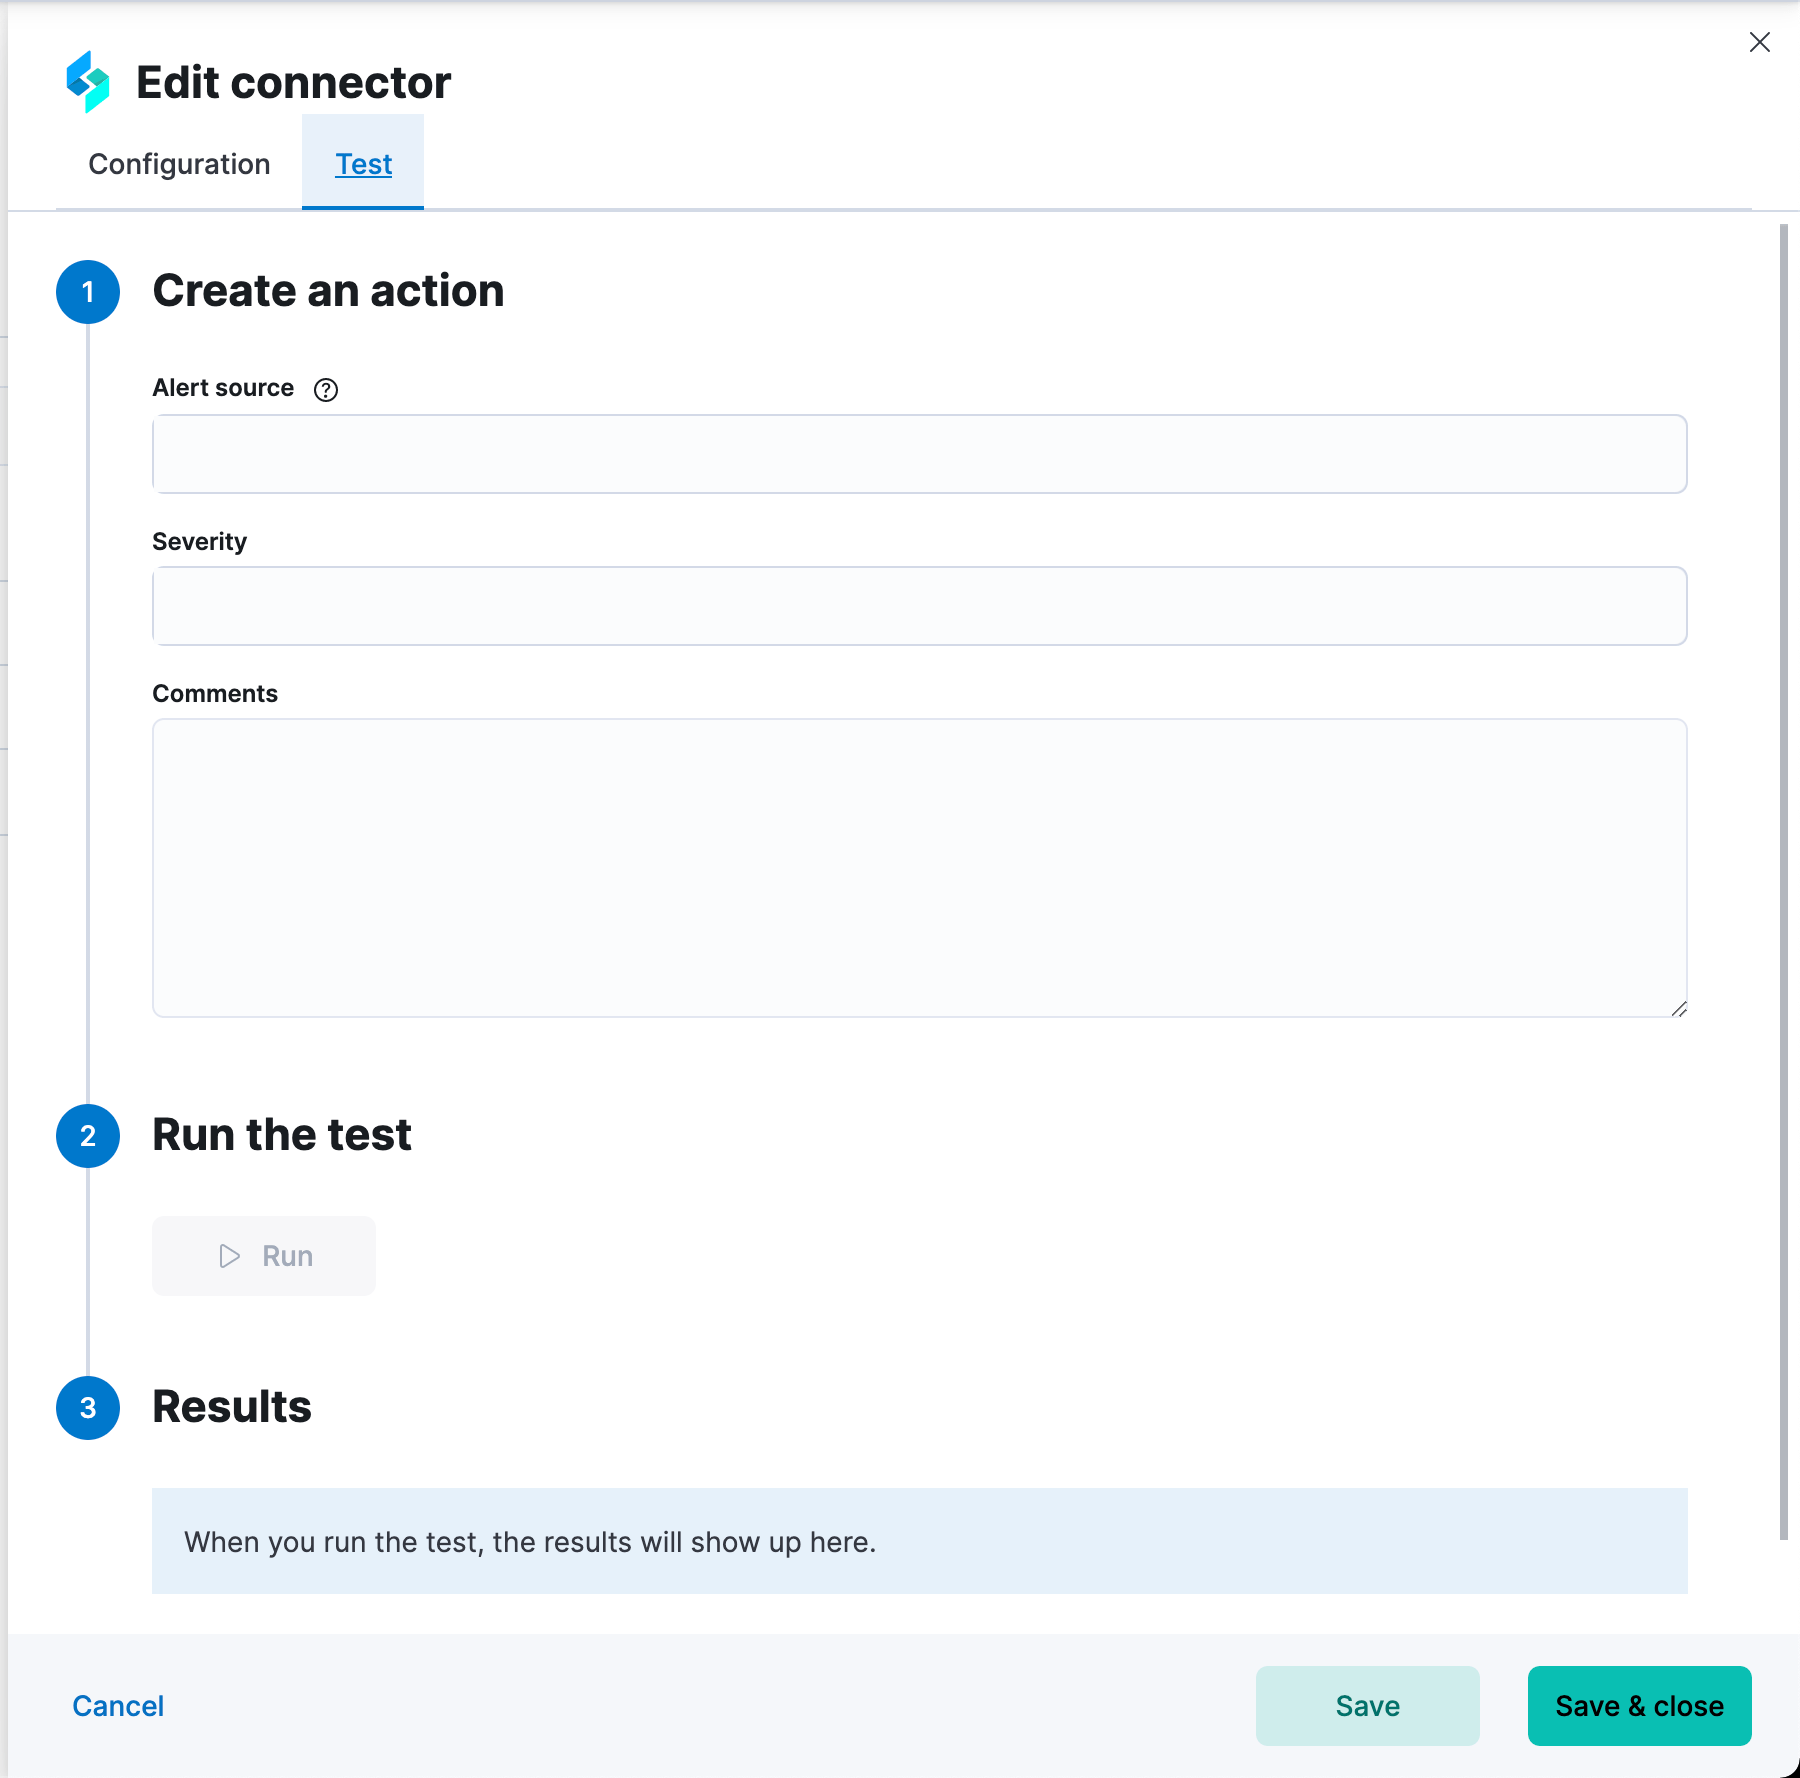
Swimlane actions have the following configuration properties.
- Comments
- Additional information for the client, such as how to troubleshoot the issue.
- Severity
- The severity of the incident.
Alert ID and Rule Name are filled automatically. Specifically, Alert ID is set to {{alert.id}} and Rule Name to {{rule.name}}.