---
title: Fleet and Integrations roles and privileges
description: Control access to Fleet and Integrations with Kibana built-in and custom roles. Reference tables list what each Fleet privilege allows, including managing integration policies and packages.
url: https://www.elastic.co/docs/reference/fleet/fleet-roles-privileges
products:
- Elastic Agent
- Elastic Documentation
- Fleet
applies_to:
- Elastic Cloud Serverless: Generally available
- Elastic Stack: Generally available
---
# Fleet and Integrations roles and privileges
Use Kibana roles and privileges to grant users access to Fleet and Integrations. For each of these features, select the type of access you want to allow:
- **All**: Users have full access to the feature, which includes performing all available actions and managing configuration.
- **Read**: Users can view the feature, but can't perform any actions or manage configuration.
- **None**: Users can't access or view the feature.
In Fleet, **Read** access for **Agents** also allows requesting agent diagnostics.
You can take advantage of these privilege settings by:
- [Using an Elasticsearch built-in role](#fleet-roles-and-privileges-built-in)
- [Creating a new role](#fleet-roles-and-privileges-create).
To configure access at a more granular level, select a custom set of privileges for individual Fleet features:
- [Customize sub-feature privileges for Fleet](#fleet-roles-and-privileges-sub-features)
Some actions, such as adding an integration to an agent policy, require privileges for both Fleet and Integrations. Refer to [Privileges for integrations and integration policies](#fleet-roles-and-privileges-integrations).
## Built-in roles
Elasticsearch comes with built-in roles that include default privileges.
The built-in `editor` role grants these privileges, supporting full read-write access to Fleet and Integrations:
- Fleet: `all`
- Integrations: `all`
The built-in `viewer` role grants these privileges, supporting read-only access to Fleet and Integrations:
- Fleet: `read`
- Integrations: `read`
You can also create a new role that can be assigned to a user to grant more specific levels of access to Fleet and Integrations.
## Create a new role for Fleet
In Serverless projects, create a custom role as described in [Serverless project custom roles](https://www.elastic.co/docs/deploy-manage/users-roles/serverless-custom-roles), then follow steps 4 to 6 to select spaces and set the **Fleet** and **Integrations** privileges.
To create a new role with access to Fleet and Integrations:
1. Go to the **Roles** management page in the navigation menu or use the [global search field](https://www.elastic.co/docs/explore-analyze/find-and-organize/find-apps-and-objects).
2. Select **Create role**, then enter a **Role name**.
3. Leave the Elasticsearch settings at their defaults, or refer to [Security privileges](https://docs-demo.elastic.dev/docs/reference/elasticsearch/security-privileges) for descriptions of the available settings.
4. In the Kibana section, select **Assign to space**. In the **Select spaces** field, select the spaces where the role needs access to Fleet and Integrations.
- Elastic Cloud Serverless: Generally available Elastic Stack: Generally available since 9.1 You can grant Fleet privileges in specific spaces. For how agent policies and integration assets behave across spaces, refer to [Using Spaces with Fleet](https://www.elastic.co/docs/deploy-manage/manage-spaces-fleet).
- Elastic Stack: Generally available in 9.0 Fleet privileges apply to all spaces, so select **All Spaces**.
5. Expand the **Management** section, then choose the access level that you'd like the role to have with respect to Fleet and integrations:
1. To grant the role full access to use and manage Fleet and integrations, set both the **Fleet** and **Integrations** privileges to `All`.
2. To create a read-only user for Fleet and Integrations, set both the **Fleet** and **Integrations** privileges to `Read`.
3. If you'd like to define more specialized access to Fleet based on individual components, set **Fleet** to `All` or `Read`, then expand the **Fleet** menu and enable **Customize sub-feature privileges**.
The sub-feature privileges you select replace the general **Fleet** privilege and determine which Fleet UI features the role can access. For details, refer to [Customize sub-feature privileges for Fleet](#fleet-roles-and-privileges-sub-features).
Customizing sub-feature privileges is a [subscription feature](https://www.elastic.co/subscriptions).
To let the role add integrations to agent policies or edit integration policies, also set **Integrations** to `All`. Refer to [Privileges for integrations and integration policies](#fleet-roles-and-privileges-integrations).
6. Select **Assign role**, then select **Create role**.
After you've created a new role, you can assign it to any Elasticsearch user.
You can edit the role at any time by returning to the **Roles** page in Kibana.
## Customize sub-feature privileges for Fleet
You have more granular control when [creating a new role](#fleet-roles-and-privileges-create) or editing it. This is useful when people in your organization access Fleet for different purposes, and you need to fine-tune the components that they can view and the actions that they can perform.
The Fleet UI varies depending on the privileges granted to the role.
### Example 1: Read access for Elastic Agents
Set `Read` access for Elastic Agents only:
- Agents: `Read`
- Agent policies: `None`
- Settings: `None`
With these privileges, the Fleet UI shows only the **Agents** and **Data streams** tabs.
The **Agent policies**, **Enrollment tokens**, **Uninstall tokens**, and **Settings** tabs are unavailable.
The set of actions available for an agent are limited to viewing the agent and requesting a diagnostics bundle.
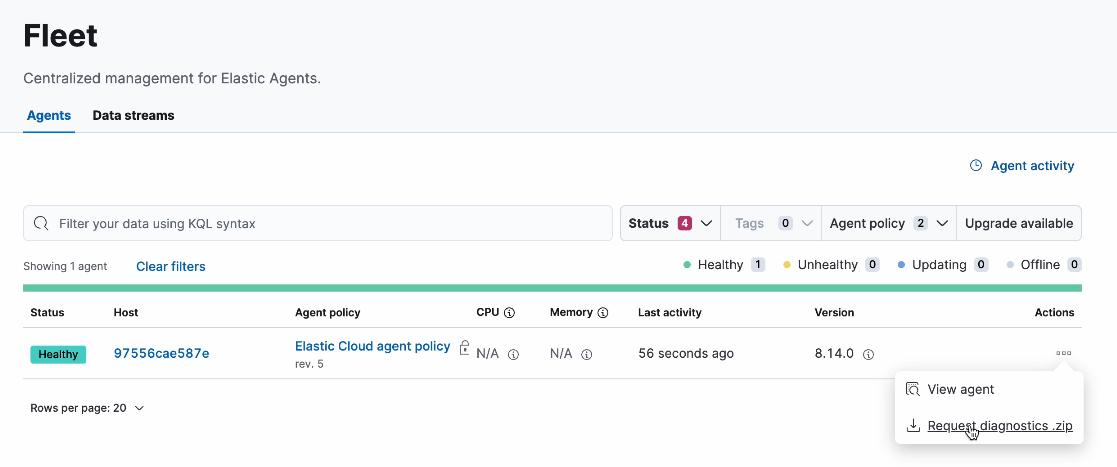
Change the **Agents** privilege to `All` to enable the role to perform the [full set of available actions](https://www.elastic.co/docs/reference/fleet/manage-agents) on Elastic Agents.
### Example 2: Read access for all Fleet features
Set `Read` access for Elastic Agents, agent policies, and Fleet settings:
- Agents: `Read`
- Agent policies: `Read`
- Settings: `Read`
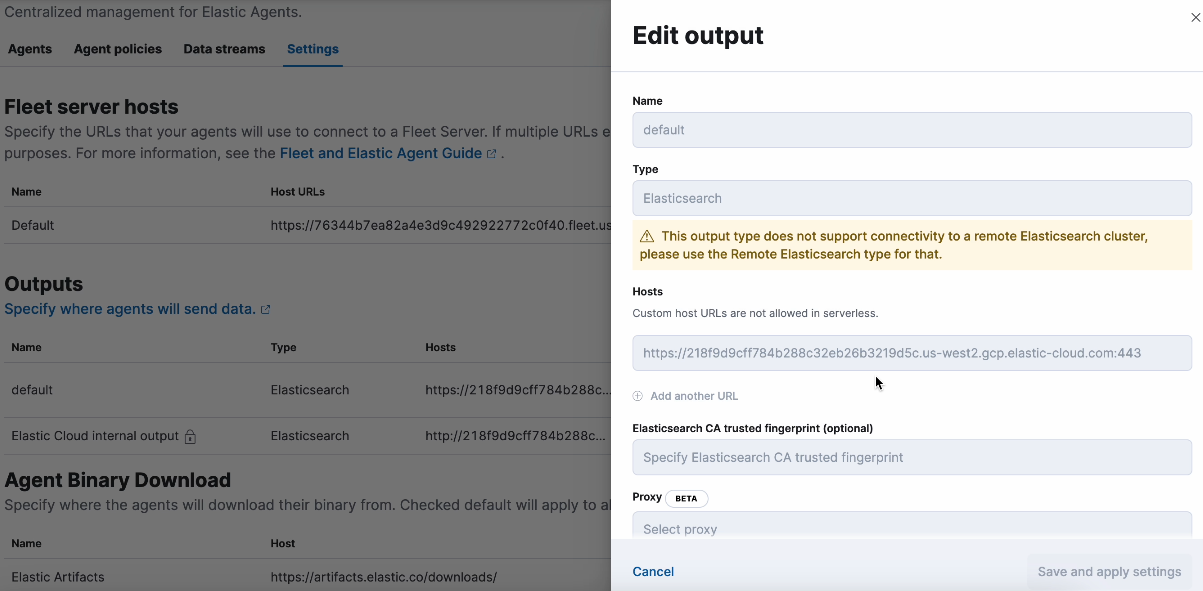
With these privileges, the Fleet UI shows the **Agents**, **Agent policies**, **Data streams**, and **Settings** tabs.
The **Enrollment tokens** and **Uninstall tokens** tabs are unavailable.
The set of actions available for an agent are limited to viewing the agent and requesting a diagnostics bundle.
You can view agent policies, but you cannot create a new policy.
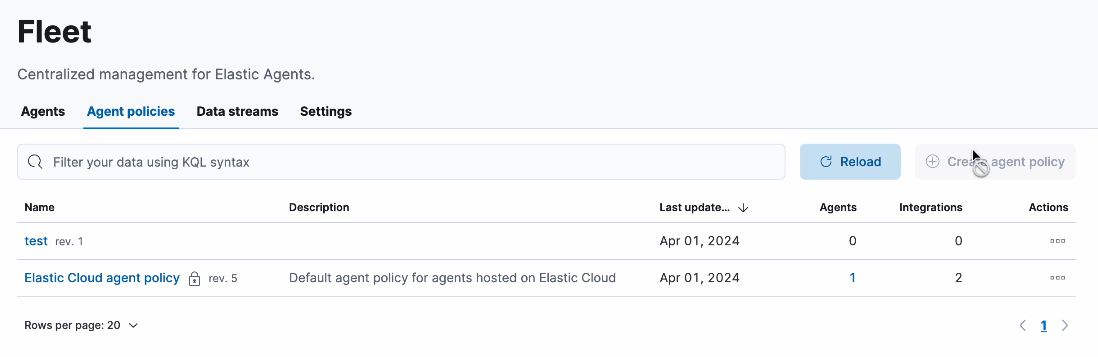
You can view Fleet settings, but they are not editable.
### Example 3: All access for Elastic Agents
Set `All` access for Elastic Agents only:
- Agents: `All`
- Agent policies: `Read`
- Settings: `Read`
With these privileges, the Fleet UI shows all tabs.
All Elastic Agent actions can be performed and new agents can be created. Enrollment tokens and uninstall tokens are both available. Access to Fleet settings is still read-only.
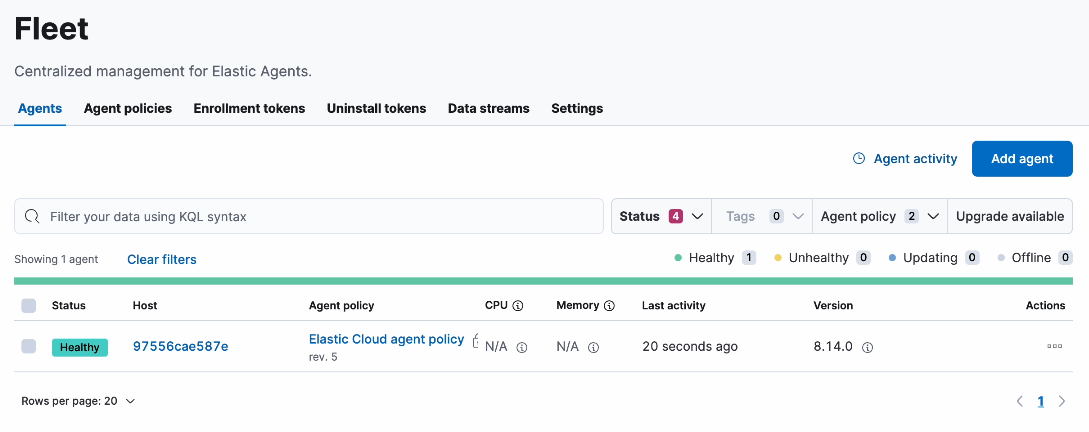
To add a Fleet Server, also set the **Agent policies** and **Settings** privileges to `All`.
## Fleet privileges and available actions
This table shows the set of available actions for the `read` or `all` privilege for each Fleet feature.
| Component | `read` privilege | `all` privilege |
|---------------------------------------------------------------------------------------------------------------------------------------------------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| Agents | View-only access to Elastic Agents, including:* [View a list of all agents and their status](/docs/reference/fleet/monitor-elastic-agent#view-agent-status)* [Request agent diagnostic packages](/docs/reference/fleet/monitor-elastic-agent#collect-agent-diagnostics) | Full access to manage Elastic Agents, including:* [Assign agents to a policy](/docs/reference/fleet/agent-policy#apply-a-policy)* [Perform upgrades](https://www.elastic.co/docs/reference/fleet/upgrade-elastic-agent)* [Migrate agents to a new cluster](https://www.elastic.co/docs/reference/fleet/migrate-elastic-agent)* [Unenroll agents from Fleet](https://www.elastic.co/docs/reference/fleet/unenroll-elastic-agent)* [Create and revoke enrollment tokens](https://www.elastic.co/docs/reference/fleet/fleet-enrollment-tokens) |
| Agent policies | View-only access, including:* Agent policies and settings* The integrations associated with a policy, if the role also has `read` or `all` for **Integrations** | Full access to manage agent policies, including:* [Create a policy](/docs/reference/fleet/agent-policy#create-a-policy)* [Edit or delete a policy](/docs/reference/fleet/agent-policy#policy-main-settings)* [Change the output of a policy](/docs/reference/fleet/agent-policy#change-policy-output)* [Configure agent monitoring](/docs/reference/fleet/agent-policy#change-policy-enable-agent-monitoring)* [Set the inactivity timeout](https://www.elastic.co/docs/reference/fleet/set-inactivity-timeout)If the role also has `all` for **Integrations**:* [Add an integration to a policy](/docs/reference/fleet/agent-policy#add-integration)* [Edit or delete an integration policy](/docs/reference/fleet/agent-policy#policy-edit-or-delete)* [Copy a policy](/docs/reference/fleet/agent-policy#copy-policy) |
| Settings | View-only access, including:* Configured Fleet hosts* Fleet output settings* The location to download agent binaries | Full access to manage Fleet settings, including:* [Editing hosts](/docs/reference/fleet/fleet-settings#fleet-server-hosts-setting)* [Adding or editing outputs](/docs/reference/fleet/fleet-settings#output-settings)* [Update the location for downloading agent binaries](/docs/reference/fleet/fleet-settings#fleet-agent-binary-download-settings) |
| Generate reports Elastic Cloud Serverless: Generally available Elastic Stack: Generally available since 9.4 | Not available. This component has an `all` privilege only. | [Export the Elastic Agents list to a CSV file](https://www.elastic.co/docs/reference/fleet/export-agents-csv) from the **Agents** tab. The role also needs `read` or `all` for **Agents**. |
## Privileges for integrations and integration policies
When you add an integration to an agent policy, Fleet creates an [integration policy](https://www.elastic.co/docs/reference/fleet/view-integration-policies) that stores the integration's settings. Viewing or managing integration policies, and installing integration packages, requires privileges for both Fleet **Agent policies** and **Integrations**. If you don't customize Fleet sub-feature privileges, the **Fleet** privilege sets the **Agent policies** access level.
| Action | Fleet **Agent policies** privilege | **Integrations** privilege |
|---------------------------------------------------------------------------------------|------------------------------------|----------------------------|
| Browse integrations and view their details | Not required | `read` or `all` |
| View integration policies | `read` or `all` | `read` or `all` |
| Add integrations to agent policies, and edit, upgrade, or delete integration policies | `all` | `all` |
| Install, upgrade, uninstall, or upload integration packages | `all` | `all` |
The **Integrations** feature has no sub-feature privileges. A role that can edit integration policies can also install, upgrade, and uninstall integration packages.